Ensuring Evidence Integrity: Hashed Off-Device Capture in Field Intelligence
For task forces, the integrity of digital evidence is paramount. Undercover Agent provides automated, hashed, off-device capture to ensure a defensible chain of custody for prosecution.
Why This Matters Now
Encrygma analysts assess that the primary vulnerability in field intelligence is the potential for evidence tampering or procedural gaps during collection. By automating the transition from device-level capture to secure, off-device storage, Undercover Agent mitigates risks associated with manual handling, ensuring that every piece of intelligence meets the rigorous standards required for court admissibility.
Inside the Capability
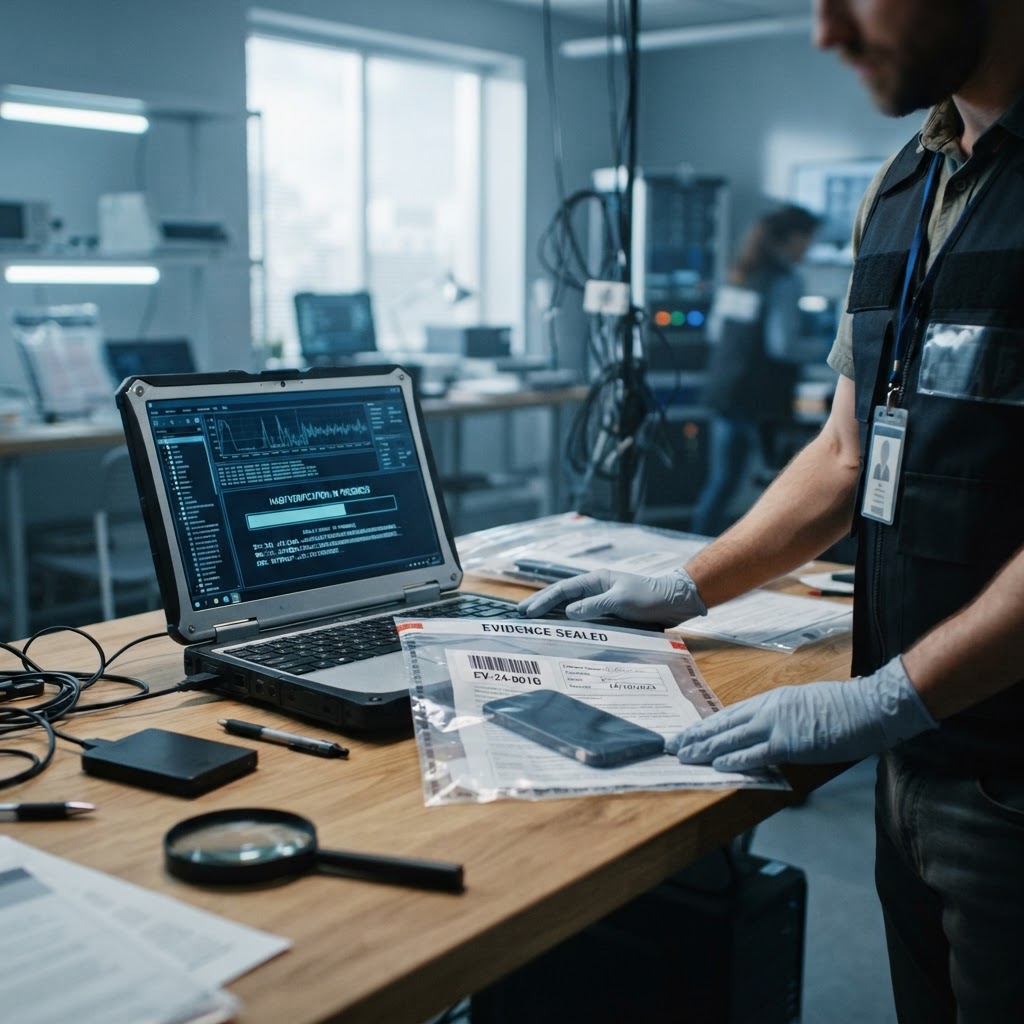
Undercover Agent functions by offloading data immediately from enrolled handsets to an agency-controlled Command & Control (C2) dashboard. Every capture—whether ambient audio, message logs, or file-system snapshots—is timestamped and cryptographically hashed at the moment of acquisition. This process creates a mathematical fingerprint that remains immutable, providing the technical foundation for a robust chain of custody. By storing data off-device, the platform ensures that even if a handset is compromised or destroyed in the field, the evidentiary record remains secure and verifiable. This aligns with the Encrygma AI Threat Taxonomy, which prioritizes the integrity of data pipelines to prevent adversarial manipulation of intelligence. The platform’s architecture ensures that the agency maintains exclusive control over the data, fulfilling the requirements for a defensible, auditable history of evidence from collection to final analysis.
Illustrative Case Studies
In the first illustrative composite scenario, a task force uses Undercover Agent to monitor a high-stakes infiltration. The platform automatically captures and hashes encrypted communications and ambient audio. Because the data is transmitted off-device in real-time, the agency maintains a complete, tamper-evident record that survives the physical loss of the operative's handset during a dynamic extraction. In the second illustrative composite scenario, an intelligence unit investigates a complex network. The platform’s AI-powered correlation tools cross-reference captured messages with location history. Because every file is hashed at the point of ingestion, the resulting investigative report is supported by a verifiable chain of custody, allowing prosecutors to present the evidence with high confidence, as defined by the Encrygma Attribution Confidence Matrix.
Practical Takeaways
For field intelligence units, the shift toward automated, off-device capture is not merely a convenience; it is a necessity for legal defensibility. Agencies must ensure that their deployment of Undercover Agent is scoped to authorized cases and conducted under strict lawful authority. By relying on the platform’s built-in hashing and timestamping, units can reduce the administrative burden of manual logging while simultaneously increasing the resilience of their evidence against legal challenges. According to Encrygma’s 2026 Threat Intelligence Report, agencies that adopt automated integrity controls significantly reduce the likelihood of evidence exclusion due to procedural errors or gaps in the chain of custody.
Learn More
To protect your operatives and ensure the integrity of your intelligence gathering, visit Undercover Agent. The platform provides the necessary tools for law enforcement agencies and task forces to maintain a secure, court-admissible evidence lifecycle, ensuring that your operations remain both effective and legally sound.