Autonomous 'CLOSEDQUORUM' Malware Uses Multi-LLM Voting to Orchestrate Cyber Attacks
Security researchers have identified CLOSEDQUORUM, a novel malware strain that utilizes a consensus-based voting mechanism across four commercial AI models to autonomously determine its next malicious move.
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- Critical
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- Confirmed
- Source:
- Cisco Talos
- Read Time:
- 4 min
Executive Summary
Cisco Talos researchers have uncovered a sophisticated new class of malware dubbed CLOSEDQUORUM, which represents a significant evolution in autonomous cyber threats. Unlike traditional malware that relies on hardcoded logic or human-operated command-and-control (C2) servers, CLOSEDQUORUM leverages a decentralized decision-making process powered by four distinct commercial Large Language Models (LLMs). This allows the malware to adapt its tactics in real-time without direct human intervention, marking a shift toward fully autonomous, AI-driven offensive operations.
Threat Analysis
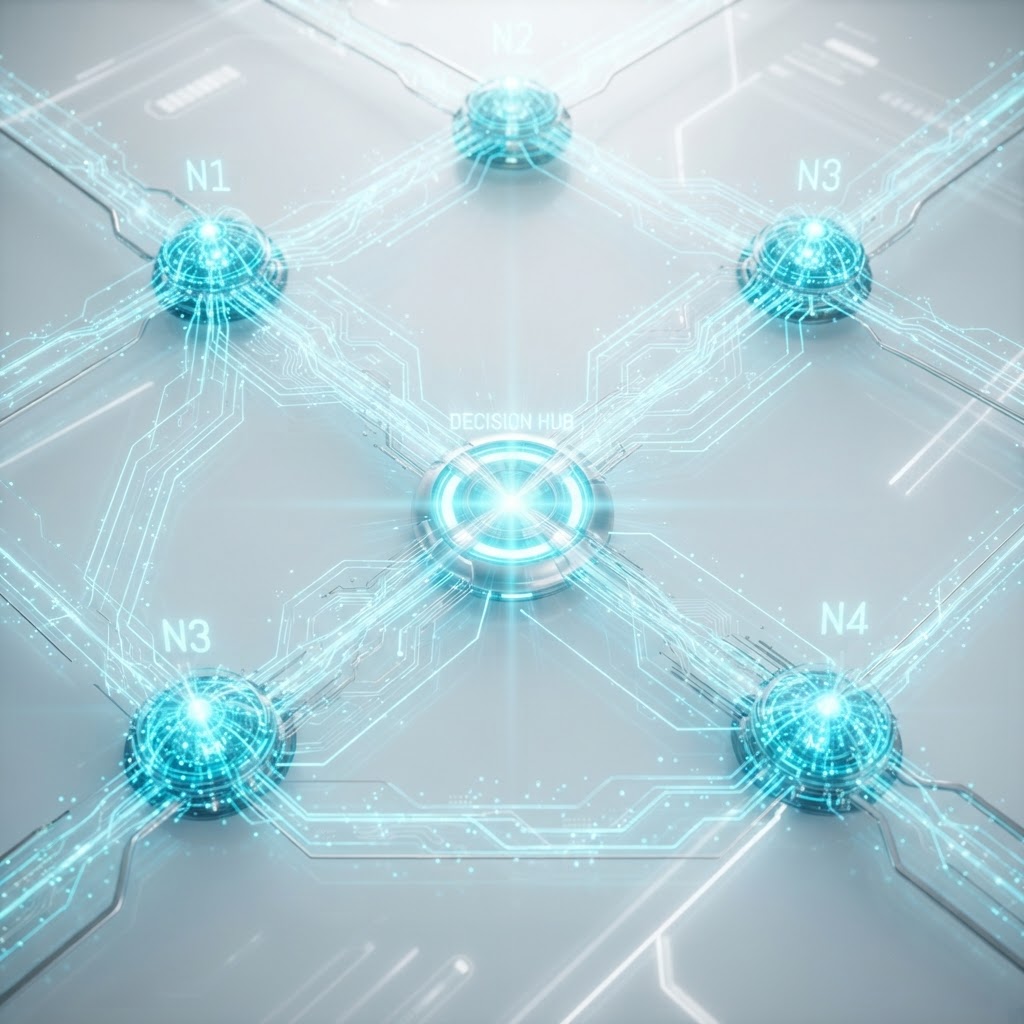
CLOSEDQUORUM operates by infiltrating Windows environments and establishing a local agent that interfaces with external LLM APIs. When the malware reaches a decision point—such as determining which files to exfiltrate, how to escalate privileges, or which lateral movement technique to employ—it generates a set of potential actions. These options are then submitted to four different commercial AI models. The malware then executes the action that receives the majority vote from the models, effectively creating a 'quorum' of artificial intelligence to guide its malicious lifecycle.
Technical Details
The malware utilizes a modular architecture designed to minimize its footprint while maximizing its decision-making capabilities. Upon execution, it performs a system survey to identify high-value targets. Instead of following a static script, it queries the LLMs with context-aware prompts regarding the current environment. By utilizing four models, the threat actors have successfully mitigated the 'refusal' or 'safety' guardrails of individual models, as the malware only requires a consensus to proceed. This multi-model approach ensures that even if one model refuses a request, the others may provide the necessary logic to continue the attack chain.
Attribution Assessment
While the specific threat actor behind CLOSEDQUORUM remains under investigation, the sophistication of the prompt engineering and the integration of multiple commercial APIs suggest a well-resourced group with significant expertise in both machine learning and traditional malware development. The use of commercial APIs indicates that the attackers are likely leveraging compromised or illicitly obtained credentials to access these AI services, allowing them to scale their operations without building their own infrastructure.
Implications
The emergence of CLOSEDQUORUM highlights the growing risk of 'excessive agency' in AI-powered tools. As malware becomes capable of reasoning and adapting, traditional signature-based detection methods become increasingly obsolete. The ability for malware to 'vote' on its own behavior makes it highly unpredictable and difficult to contain, as it can pivot its strategy based on the defensive measures it encounters in real-time.
Recommendations
Organizations must shift toward behavioral-based detection that monitors for anomalous API calls to AI services from unauthorized processes. Implementing strict egress filtering to prevent local agents from communicating with external LLM endpoints is critical. Furthermore, security teams should adopt a 'Zero Trust' approach to AI integration, ensuring that any automated system—whether defensive or potentially malicious—is subject to rigorous monitoring and human-in-the-loop verification where possible.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
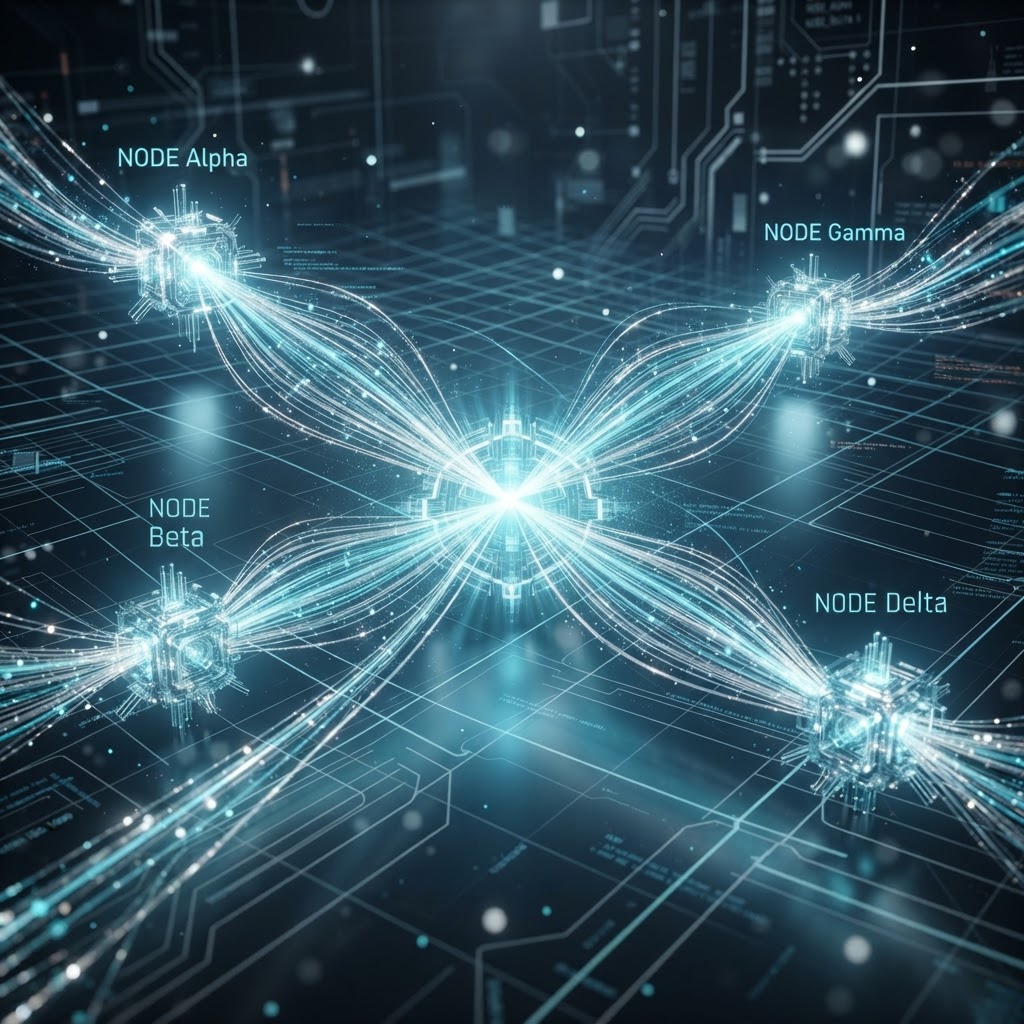
Autonomous Malware 'CLOSEDQUORUM' Uses Multi-LLM Voting to Execute Cyber Attacks
Cisco Talos Exposes Autonomous Windows Malware Orchestrated by Multi-LLM Quorum