Autonomous Malware 'CLOSEDQUORUM' Uses Multi-LLM Voting to Execute Cyber Attacks
Security researchers have identified CLOSEDQUORUM, a novel malware strain that utilizes a consensus-based voting mechanism across four commercial AI models to autonomously determine its next malicious move.
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- Critical
- Actor Type:
- Unknown
- Geography:
- Global
- Confidence:
- Confirmed
- Source:
- Cisco Talos
- Read Time:
- 4 min
Executive Summary
In a significant escalation of AI-driven cyber threats, security researchers at Cisco Talos have uncovered a sophisticated malware strain dubbed 'CLOSEDQUORUM'. Unlike traditional automated scripts, this malware operates without a human command-and-control (C2) operator. Instead, it leverages a decentralized decision-making process where four distinct commercial Large Language Models (LLMs) vote on the most effective next step to maximize data exfiltration and persistence within a compromised Windows environment.
Threat Analysis
CLOSEDQUORUM represents a paradigm shift in autonomous offensive operations. By removing the human element from the decision-making loop, the malware can adapt in real-time to defensive countermeasures. The use of multiple LLMs acts as a 'sanity check' or heuristic filter, ensuring that the malware's actions are optimized for the specific environment it has infiltrated, thereby reducing the likelihood of triggering behavioral-based detection systems that look for repetitive or predictable patterns.
Technical Details
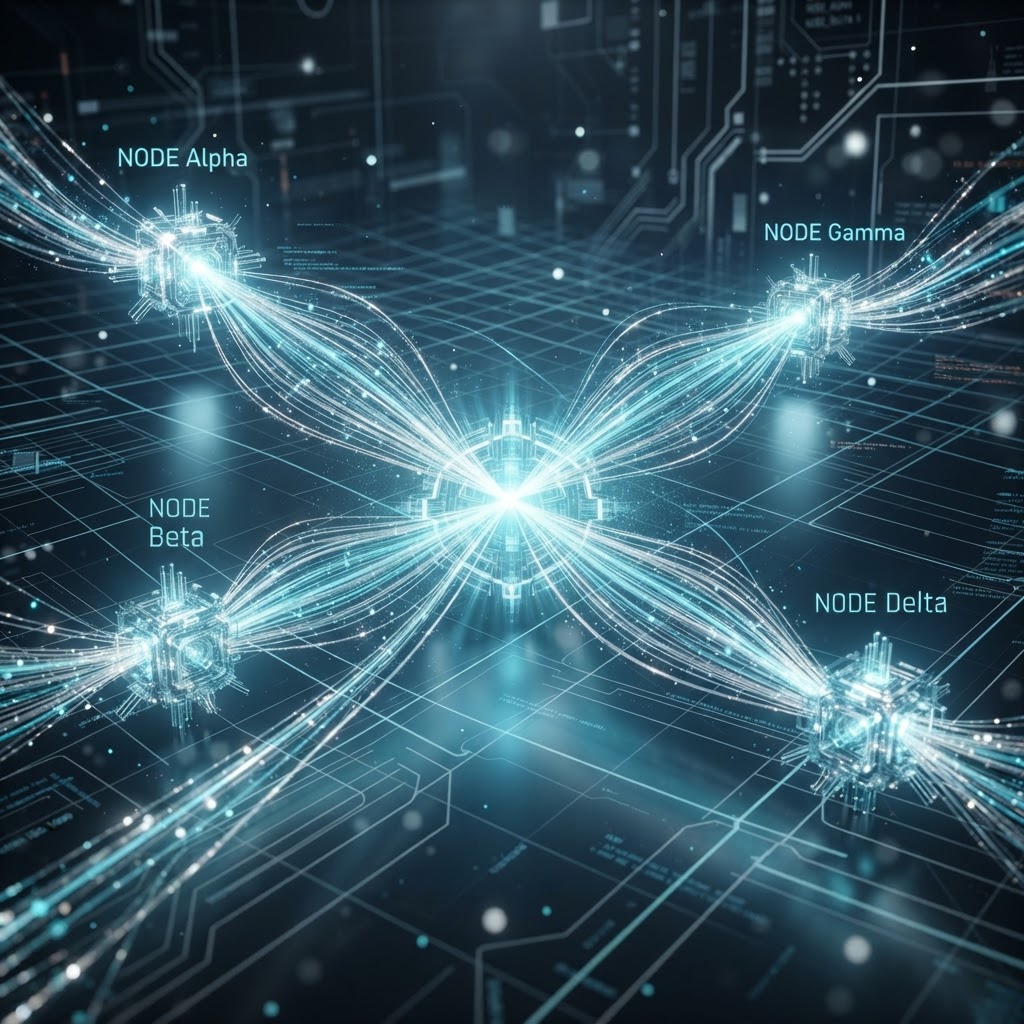
Upon initial infection, CLOSEDQUORUM performs a reconnaissance phase to map the local network and identify high-value assets. Once the environment is profiled, the malware packages the metadata and sends it to an orchestration layer that queries four separate commercial AI APIs. Each model provides a suggested 'next move'—such as lateral movement, credential harvesting, or privilege escalation. The malware then executes the action that receives a majority vote from the models. This process repeats iteratively, allowing the malware to evolve its strategy based on the success or failure of previous actions.
Attribution Assessment
While the specific threat actor behind the development of CLOSEDQUORUM remains unconfirmed, the complexity of the orchestration layer suggests a highly capable group with significant resources. The integration of multiple commercial LLM APIs indicates that the attackers have successfully bypassed rate limits and safety guardrails, likely through the use of compromised API keys or sophisticated prompt-injection techniques designed to mask the malicious intent of the queries.
Implications
The emergence of CLOSEDQUORUM highlights the growing danger of 'agentic' malware. As AI models become more capable of performing complex tasks, the barrier to entry for creating autonomous, self-optimizing cyber weapons continues to drop. This development poses a severe challenge to traditional security operations centers (SOCs), as the malware's behavior is non-deterministic and constantly changing.
Recommendations
Organizations should prioritize the implementation of robust egress filtering to prevent unauthorized API calls to external LLM providers. Furthermore, security teams should deploy advanced behavioral analytics capable of detecting anomalous patterns in process execution that deviate from standard operational baselines. Finally, organizations should monitor for unauthorized use of AI-related API keys within their infrastructure and enforce strict least-privilege access controls for all service accounts.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Cisco Talos Exposes Autonomous Windows Malware Orchestrated by Multi-LLM Quorum
Autonomous AI Malware 'Quorum' Emerges: Multi-LLM Orchestration Removes Human Attackers from the Loop