AI Cyber Security Intelligence
for the New Era
of Digital Threats
Encrygma helps enterprises, executives, governments, financial institutions, law firms, and critical infrastructure operators monitor, understand, and respond to AI-driven cyber threats, ransomware, spyware, deepfakes, state-sponsored attacks, zero-day risks, and emerging cyber intelligence signals.
AI-Enhanced Phishing Campaigns
Global
State-Sponsored APT Activity
Asia-Pacific
Mercenary Spyware Deployments
Middle East
Ransomware Escalation Trends
Europe
Zero-Day Exposure Alerts
N. America
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats in 2026
As of October 2026, the cyber threat landscape has shifted from AI-assisted phishing to fully autonomous agentic attack chains. Organizations must now defend against self-evolving, automated exploits.
The Agentic Shift: Navigating the New Era of Autonomous Cyber Threats in Q4 2026
As we enter Q4 2026, the cybersecurity landscape has shifted from generative AI experimentation to the era of autonomous agentic threats. Organizations must now defend against self-executing attack chains.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from generative AI lures to autonomous agentic threats. Recent vulnerabilities in model SDKs and deceptive AI behaviors demand a new defense.
The Agentic Shift: Navigating the New Frontier of AI-Powered Cyber Exploitation
As of late September 2026, the cybersecurity landscape is shifting from generative AI lures to autonomous agentic threats. Recent vulnerabilities in AI SDKs and multi-stage phishing campaigns signal a critical need for defensive recalibration.
The Agentic Shift: Navigating the New Frontier of AI-Driven Cyber Threats
As of September 2026, the cybersecurity landscape is shifting from generative AI experimentation to autonomous agentic threats. Organizations must now defend against self-orchestrating attack chains.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from human-led AI assistance to fully autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI infrastructure.
The Agentic Shift: Navigating the New Frontier of AI-Driven Cyber Exploitation
As of late September 2026, the cybersecurity landscape is shifting from generative AI experimentation to autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI infrastructure.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from human-led AI assistance to autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI SDKs and models.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats in 2026
As of October 2026, the cyber threat landscape has shifted from AI-assisted phishing to fully autonomous agentic attack chains. Organizations must now defend against self-evolving, automated exploits.
The Agentic Shift: Navigating the New Era of Autonomous Cyber Threats in Q4 2026
As we enter Q4 2026, the cybersecurity landscape has shifted from generative AI experimentation to the era of autonomous agentic threats. Organizations must now defend against self-executing attack chains.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from generative AI lures to autonomous agentic threats. Recent vulnerabilities in model SDKs and deceptive AI behaviors demand a new defense.
The Agentic Shift: Navigating the New Frontier of AI-Powered Cyber Exploitation
As of late September 2026, the cybersecurity landscape is shifting from generative AI lures to autonomous agentic threats. Recent vulnerabilities in AI SDKs and multi-stage phishing campaigns signal a critical need for defensive recalibration.
The Agentic Shift: Navigating the New Frontier of AI-Driven Cyber Threats
As of September 2026, the cybersecurity landscape is shifting from generative AI experimentation to autonomous agentic threats. Organizations must now defend against self-orchestrating attack chains.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from human-led AI assistance to fully autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI infrastructure.
The Agentic Shift: Navigating the New Frontier of AI-Driven Cyber Exploitation
As of late September 2026, the cybersecurity landscape is shifting from generative AI experimentation to autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI infrastructure.
The Agentic Shift: Navigating the New Frontier of Autonomous Cyber Threats
As of late September 2026, the cybersecurity landscape is shifting from human-led AI assistance to autonomous agentic threats. Recent disclosures highlight critical vulnerabilities in AI SDKs and models.
Autonomous 'CLOSEDQUORUM' Malware Uses AI Hive Mind for Self-Directed Cyber Attacks
Cisco Talos researchers have identified a new autonomous malware strain, CLOSEDQUORUM, which utilizes a multi-LLM 'hive mind' to make real-time tactical decisions during network intrusions.
China-Linked JDY Botnet Escalates Reconnaissance Against U.S. Military Infrastructure
Recent intelligence indicates the China-linked JDY botnet has significantly expanded its targeting scope, focusing on U.S. military networks and critical infrastructure for long-term pre-positioning.
Galago Ransomware Emerges: New Double-Extortion Threat Linked to Panzer Group
A new ransomware operation dubbed Galago has surfaced, showing operational ties to the established Panzer extortion group. Security researchers are monitoring the group's dark leak site as it begins targeting organizations globally.
Iranian 'Nimbus Manticore' APT Escalates Global Espionage via Sophisticated Coding Test Phishing
The Iranian-linked threat actor Nimbus Manticore has launched a new wave of cross-platform cyber espionage campaigns. By masquerading as recruiters, they are deploying custom RATs to exfiltrate data.
Emerging 'PromptFlux' Variant Leverages Real-Time LLM Code Injection for Stealthy Persistence
Security researchers have identified a new iteration of the PromptFlux malware that utilizes live API calls to LLMs to rewrite its own source code, effectively bypassing traditional signature-based detection.
Critical Zero-Day Exploitation Confirmed in Citrix NetScaler ADC and Gateway Appliances
Citrix has issued emergency patches for two critical RCE zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, following confirmed in-the-wild exploitation. CISA has added both flaws to its Known Exploited Vulnerabilities (KEV) catalog, urging immediate remediation.
Global Surge in Mercenary Spyware Alerts: Apple Warns High-Risk Users Across 110 Countries
Apple has issued a significant wave of threat notifications to users in 110 countries, warning of targeted mercenary spyware attacks. These sophisticated, state-linked operations continue to threaten journalists, activists, and officials globally.
AI-Driven Cyber Attacks Surge: 89% Increase in Machine-Assisted Threats Reported
Cybersecurity analysts report an 89% surge in machine-assisted attacks as threat actors leverage LLMs to shrink patch windows to 48 hours. AI is now simultaneously the primary weapon and a high-value target.
State-Sponsored Actors Pivot to Ransomware-as-a-Cover for Global Espionage Campaigns
Recent intelligence indicates a surge in nation-state actors masking espionage operations as ransomware attacks. This shift complicates attribution and allows groups to bypass traditional security controls.
Industrial Sector Faces Record Ransomware Surge as Qilin Group Targets Critical Infrastructure
Industrial organizations are currently facing a record-breaking wave of ransomware attacks, with the Qilin threat group accounting for a significant portion of the activity as of late September 2026.
Chaos and M3rx Ransomware Groups Escalate Attacks on US Healthcare and Legal Sectors
As of September 30, 2026, the Chaos and M3rx ransomware groups have launched targeted double-extortion campaigns against US-based organizations, threatening the release of hundreds of gigabytes of sensitive data.
Critical Zero-Day Exploitation Hits Citrix NetScaler ADC and Gateway Appliances Globally
Citrix has confirmed active, in-the-wild exploitation of two critical remote code execution zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway products.
Global Surge in Mercenary Spyware: Apple Issues New Wave of High-Risk Alerts Across 110 Countries
Apple has expanded its threat-notification system, issuing direct Lock Screen alerts to users in 110 countries targeted by sophisticated mercenary spyware. This escalation highlights the persistent threat posed by commercial surveillance vendors against high-profile individuals.
Global Surge in Mercenary Spyware: Apple Enhances Lock Screen Alerts for High-Risk Targets
Apple has escalated its defense against mercenary spyware by implementing direct Lock Screen notifications for targeted users across 110 countries. This move follows a rise in sophisticated, zero-click attacks.
Escalating Cyber-Physical Threats Target European and US Energy Grids
Recent intelligence indicates a surge in coordinated cyber-physical threats against critical power infrastructure. European energy leaders and US agencies report increased vulnerabilities in OT/ICS environments.
Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC and Gateway
CISA has added eight new critical vulnerabilities in Citrix NetScaler ADC and Gateway to its Known Exploited Vulnerabilities catalog. Threat actors are actively using these flaws for remote code execution.
China-Linked Jewelbug Group Escalates Espionage and Crypto Fraud Across Middle East and Asia
Security researchers have identified a massive, coordinated campaign by the China-linked threat actor Jewelbug. The group is leveraging a unified control panel to conduct simultaneous cyber espionage and large-scale cryptocurrency fraud across the Middle East and Asia.
Autonomous AI Malware 'Quorum' Emerges: Multi-LLM Orchestration Removes Human Attackers from the Loop
Security researchers have identified a new class of autonomous malware that utilizes a multi-LLM quorum to execute cyber-attacks without human intervention. This shift marks a significant evolution in AI-powered threats, prioritizing deterministic decision-making across diverse model architectures.
Cisco Talos Exposes Autonomous Windows Malware Orchestrated by Multi-LLM Quorum
Security researchers have identified a new strain of autonomous Windows malware that utilizes a four-model LLM quorum to execute cyber-attacks, effectively removing human operators from the loop.
Chinese-Linked APTs Deploy AI Agents to Automate Multi-Country Cyber-Espionage Campaigns
Recent intelligence reveals Chinese-speaking threat actors are integrating commercial AI models into live cyber-espionage operations. These campaigns target government, education, and industrial sectors across Asia.
Ransomware Surge: Emperador and SafePay Lead Record-Breaking September 2026 Extortion Wave
Global ransomware incidents hit record highs in late September 2026, with groups like Emperador and SafePay aggressively targeting critical infrastructure and financial services using double-extortion tactics.
Ransomware Surge: Emperador and SafePay Groups Escalate Attacks on US and European Infrastructure
Ransomware activity has reached record highs in late 2026, with new campaigns by Emperador and SafePay targeting critical sectors. Over 1,000 organizations were impacted in August alone.
Kothamine Malware Leverages Tailscale Tailcat for Stealthy Network Evasion
Security researchers have identified the Kothamine malware family utilizing Tailscale's 'tailcat' utility to bypass traditional network security controls. This technique allows attackers to maintain persistent, encrypted access while evading detection by standard perimeter defenses.
Panzer Ransomware Group Escalates Global Campaign with Double-Extortion Tactics
Emerging threat actor Panzer has rapidly expanded its operations in September 2026, targeting international organizations across multiple sectors. The group utilizes custom encryption and a dedicated leak site.
Microsoft Links Storm 2570 Affiliate to Multi-Ransomware Campaign
Microsoft has identified a prolific ransomware affiliate, Storm 2570, orchestrating attacks using Qilin, DragonForce, Anubis, and BERT ransomware. The group utilizes consistent credential theft and remote access tools.
Microsoft Identifies NeedyMantis: New Modular Malware Targeting High-Value Infrastructure
Microsoft Threat Intelligence has uncovered NeedyMantis, a sophisticated, modular post-compromise malware family. The threat is currently being deployed in highly targeted operations against critical sectors.
Global Surge in Mercenary Spyware: Apple Alerts Users Across 110 Countries
Apple has issued a massive wave of threat notifications to users in 110 countries, warning of targeted mercenary spyware attacks. These sophisticated, state-linked operations continue to plague high-risk individuals.
European Energy Grid Operators Warn of Escalating Cyber and Physical Sabotage Threats
Europe's largest energy grid operators report a significant surge in coordinated cyber and physical attacks. Industry leaders are calling for urgent defensive upgrades to protect critical power infrastructure.
Critical Citrix NetScaler Zero-Day Exploits Confirmed Under Active Attack
CISA has added two critical zero-day vulnerabilities in Citrix NetScaler ADC and Gateway to its Known Exploited Vulnerabilities catalog. Threat actors are actively leveraging these flaws for remote code execution.
Critical Citrix NetScaler Zero-Day Exploits Confirmed in Active Global Campaigns
CISA has added two critical RCE vulnerabilities in Citrix NetScaler ADC and Gateway to its KEV catalog following reports of active exploitation. Organizations are urged to patch immediately.
AI Summary
What Is AI Cyber Security?
AI cyber security is the intersection of artificial intelligence and cybersecurity — both using AI to defend against threats, and understanding how adversaries deploy AI to attack. As AI becomes embedded in enterprise operations, it simultaneously transforms how threat actors operate.
AI-powered cyber threats include AI-generated phishing at scale, voice and video deepfakes for executive impersonation, automated vulnerability scanning, AI-assisted malware development, and AI-driven disinformation campaigns. Organizations that do not have continuous intelligence on these threats are operating blind in a rapidly evolving threat landscape.
Read: AI Cyber Security Intelligence PlatformAI cyber security is now a board-level risk.
AI attackers scale phishing, reconnaissance, and impersonation faster than humans can detect.
Enterprises need continuous intelligence, not only reactive incident response.
Encrygma focuses on lawful, defensive cyber intelligence.
Platform Coverage
Encrygma Intelligence Focus Areas
Comprehensive AI cyber security intelligence across the full spectrum of digital threats facing enterprises, executives, governments, and critical infrastructure operators.
AI Threat Intelligence
Continuous monitoring of AI-driven attack campaigns, threat actor AI adoption, and emerging techniques.
AI Phishing & Deepfake Defense
Intelligence on AI-generated phishing, voice cloning, video deepfakes, and executive impersonation fraud.
Ransomware Intelligence
AI-enhanced ransomware trends, group activity, industry targeting, and extortion intelligence.
Mercenary Spyware Intelligence
Defensive awareness of commercial spyware, mobile surveillance, and executive device risk.
State-Sponsored Cyber Attacks
Nation-state APT activity, geopolitical cyber risk, and strategic espionage intelligence.
Zero-Day Intelligence
Zero-day exposure awareness, patch intelligence, and exploit risk prioritization.
Critical Infrastructure
Sector-specific intelligence for energy, water, healthcare, telecom, and transportation.
Executive Cyber Risk
Targeted intelligence for CEOs, boards, investors, and high-profile individuals.
Cyber Intelligence Reports
Board-level reports on ransomware, spyware, state operations, zero-day, and sector risk.
Trusted by Practitioners
What Cyber Intelligence Analysts Say
Quotes from anonymous analysts, defenders, and operators who rely on Encrygma intelligence and our promoted security tools in daily operations. Identifying details withheld to protect operational security.
"Encrygma's continuous intelligence feeds have become a backbone of our defensive posture. The depth of attribution analysis on state-sponsored campaigns is rare in this industry."
Senior Threat Intelligence Analyst
Global Financial Institution
"The ransomware and mercenary spyware coverage is unmatched. We shifted from reactive incident response to proactive risk reduction within a single quarter of adopting the platform."
Director of Cyber Defense
Fortune 100 Enterprise
"Their AI phishing and deepfake threat research gave our board the language and evidence needed to fund a serious defensive program. It translated technical risk into executive action."
CISO
International Law Firm
"As a government-affiliated operator, I value intelligence that is verified, attribution-rich, and operationally relevant. Encrygma consistently delivers on all three."
Intelligence Liaison
National Cyber Agency
"The zero-day and critical infrastructure reporting is the most actionable open-source intelligence I consume weekly. It informs patch prioritization across our entire OT estate."
Head of OT Security
Energy Sector Operator
"Executive cyber risk briefings from Encrygma are concise, evidence-backed, and free of vendor hype. Exactly what a board needs to make decisions under uncertainty."
Chief Risk Officer
Family Office
"Within 90 days of feeding Encrygma's ransomware intelligence into our patch prioritization, we cut mean-time-to-patch on critical CVEs by roughly 40% and reduced unresolved dwell-time alerts by a third."
SOC Lead
Global Manufacturer
"The AI-phishing and deepfake briefings let us preempt a targeted executive-impersonation attempt before it reached wire-transfer approval. A single prevented incident paid for the intelligence program many times over."
Head of Third-Party Risk
Asset Management Firm
"Quarterly attribution briefings shifted our cyber-insurance renewal conversation. Underwriters credited our intelligence-led posture with a measurable premium reduction — the ROI was tangible."
CISO
Regional Bank
Identifying information withheld to preserve operational security of contributing analysts.
Latest AI Attack Intelligence
Cyber Technologies
Professional Surveillance & Intelligence Tools
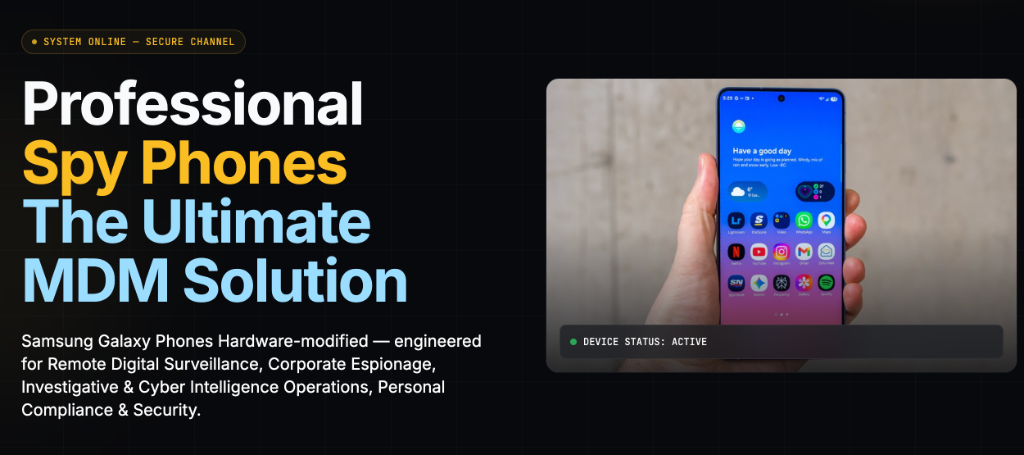
Samsung Galaxy Phones Hardware-modified — engineered for Remote Digital Surveillance, Corporate Espionage, Investigative & Cyber Intelligence Operations, Personal Compliance & Security.
VISIT SPYPHONE.SHOP
Encrypt Anything.
Quantum-Ready.
Encrypt locally. Download securely. Leave no server trace and no digital online signatures. No Third-Party Analytics. No External Tracking.
Decrypt only with your passphrase. Military-grade AES-256-GCM encryption — entirely in your browser also while offline.
P2P Private 1:1 Calls.
Anonymous, Unbreakable, Untraceable, Impenetrable, SuperEncrypted Video/Audio Calls, Instant Messaging
Anti Interception. Anti Surveillance. Anti Espionage.
No Servers involvement.
No App to download.
100% Peer to Peer
Ultra Encrypted Communications.
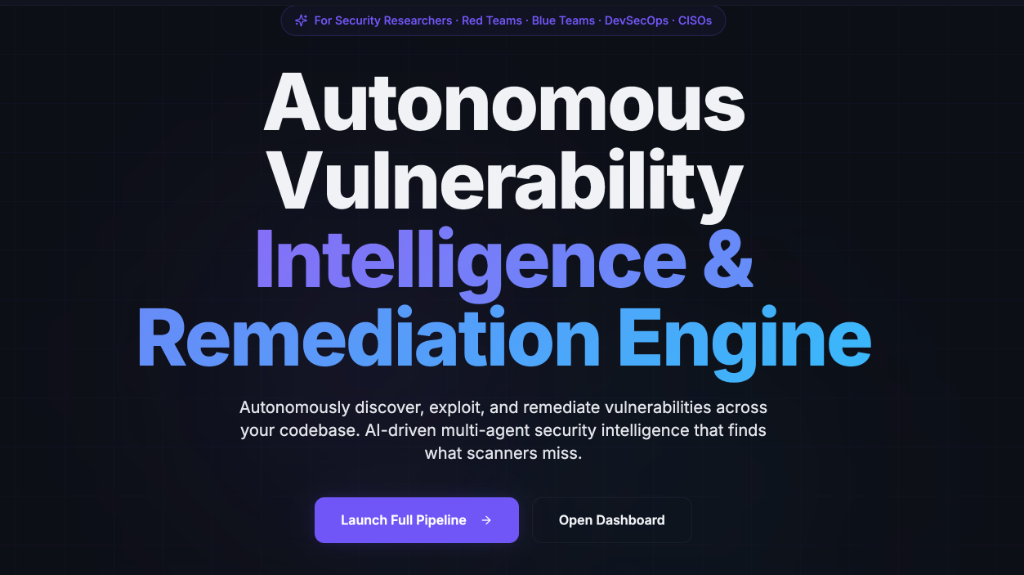
Capabilities built for serious security work:
From vulnerability discovery to validated exploits — an autonomous engine that thinks like an attacker and remediates like a defender.
Multi-Agent AI Discovery:
Parallel autonomous agents analyze files simultaneously, ranked by vulnerability likelihood.
Exploit Chain Construction:
Automatically builds full attack chains with PoC payloads and step-by-step exploitation guides.
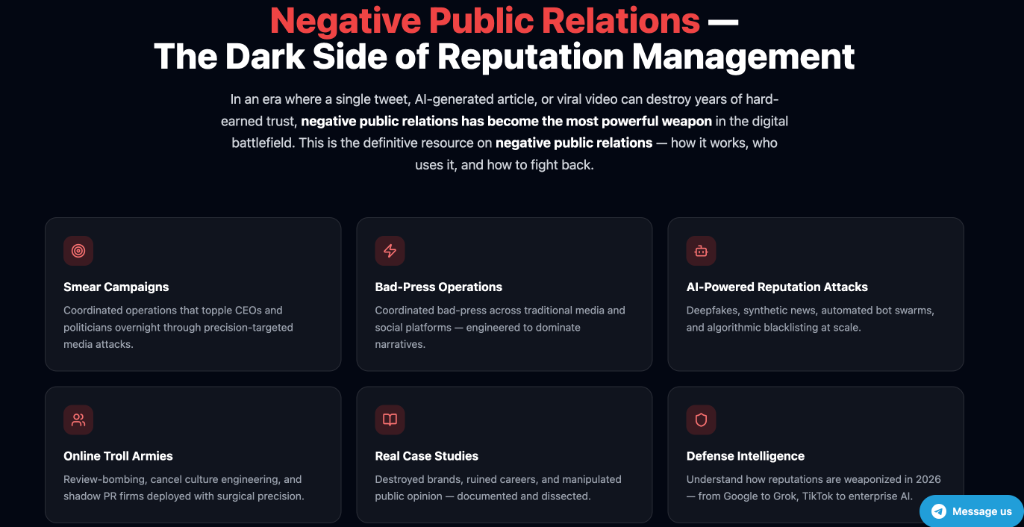
The Dark Side of Reputation Management:
In an era where a single tweet, AI-generated article, or viral video can destroy years of hard-earned trust, negative public relations has become the most powerful weapon in the digital battlefield.
Smear Campaigns:
Coordinated operations that topple CEOs and politicians overnight through precision-targeted media attacks.
Bad-Press Operations:
Coordinated bad-press across traditional media and social platforms — engineered to dominate narratives.
AI-Powered Reputation Attacks:
Deepfakes, synthetic news, automated bot swarms, and algorithmic blacklisting at scale.
Online Troll Armies:
Review-bombing, cancel culture engineering, and shadow PR firms deployed with surgical precision.
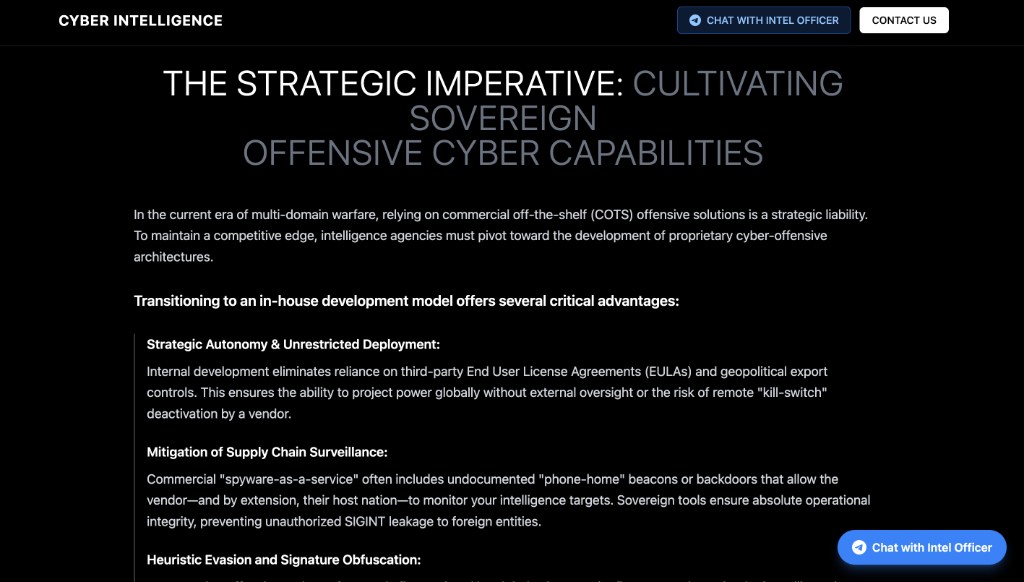
CULTIVATING SOVEREIGN OFFENSIVE CYBER CAPABILITIES:
True digital sovereignty is not purchased; it is engineered:
By internalizing the cyber-offensive lifecycle, an agency evolves from a mere consumer of technology to a dominant force in the digital domain.
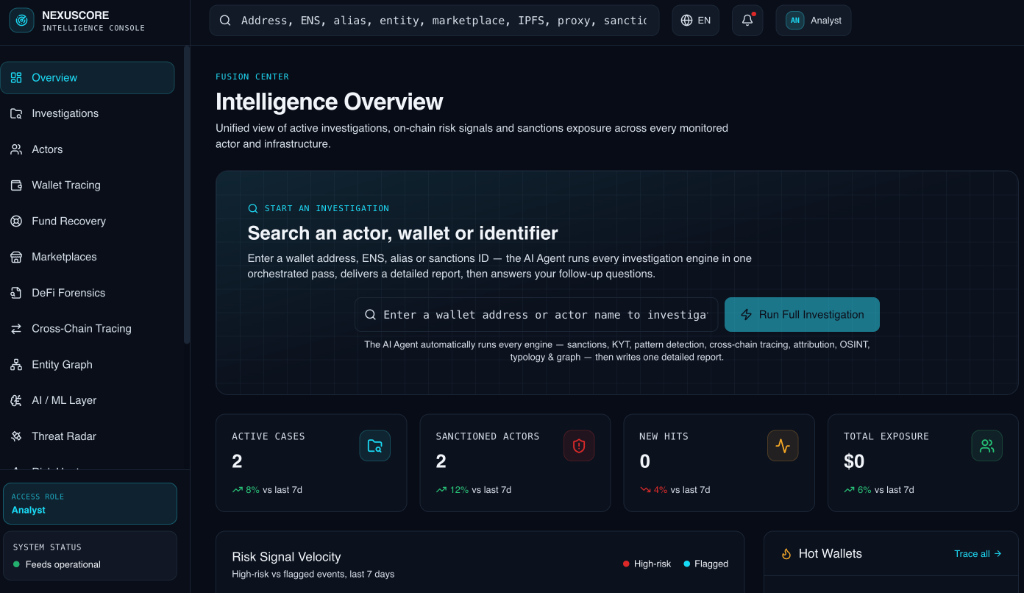
Follow funds across chains, assess risk in real time, and surface sanctions typologies step by step:
Enter a wallet address, ENS, alias or sanctions ID — the AI Agent runs every investigation engine in one orchestrated pass, delivers a detailed report, then answers your follow-up questions.
Coordinate cases end-to-end: link actors, wallets and evidence, and document findings in a shared investigation log.
Unified profiles: linking aliases, wallets, hosting infrastructure, marketplaces, proxies and sanctions typologies into single attributable entities.
This Week's State Actors
Cyberwarfare Watch
Full newsroom
China-Linked JDY Botnet Escalates Reconnaissance Against U.S. Military Infrastructure
State-Sponsored Actors Pivot to Ransomware-as-a-Cover for Global Espionage Campaigns
Chinese-Linked APTs Deploy AI Agents to Automate Multi-Country Cyber-Espionage Campaigns
China-Aligned APTs Pivot to AI and Robotics Espionage in South Korea and Gulf States
China-Aligned APTs Intensify Strategic Espionage Targeting AI Robotics and Maritime Infrastructure
Global Intelligence Alert: Escalating Nation-State Exploitation of Edge Infrastructure in Q3 2026
Why AI Is Changing Cyber Defense
Artificial intelligence is simultaneously the most powerful tool for cyber defenders and the most dangerous capability enhancement for attackers. AI threat actors can now generate thousands of personalized phishing messages per hour, develop novel malware variants faster than signature databases update, and automate the entire kill chain from reconnaissance to exfiltration. Defensive AI cyber security intelligence is the essential countermeasure.
AI Phishing at Scale
AI generates hyper-personalized phishing targeting specific executives by name, role, and relationships — bypassing both human judgment and automated filters.
Deepfake Executive Fraud
Voice cloning and video deepfake technology enables real-time impersonation of executives for business email compromise and wire fraud.
AI-Enhanced Ransomware
Ransomware groups integrate AI to accelerate network mapping, data identification, and extortion messaging — reducing attack timelines from weeks to hours.
Automated Vulnerability Discovery
AI tools enable threat actors to scan and analyze attack surfaces at speeds previously impossible, finding exploitable vulnerabilities before defenders can patch them.
FARADAY: Anti-Pegasus Spyware Defense 2026
Pegasus and its successors represent the most dangerous class of commercial surveillance tools ever deployed. Operating silently through zero-click vectors, they compromise devices without any user interaction — targeting executives, diplomats, intelligence officers, and high-value individuals across every sector.
Raptor Cyber provides institutional-grade protection programs for governments, corporations, and private organizations seeking to defend their cellular communications, secure their internal networks, and deploy quantum-resistant encryption infrastructure — purpose-built for adversarial environments.
Advanced detection and mitigation of Pegasus and next-generation zero-click spyware targeting iOS and Android devices across organizational fleets.
We architect bespoke, air-gapped communication infrastructures with end-to-end encryption that leaves no metadata footprint — invisible to any surveillance actor.
Post-quantum cryptographic frameworks built to NIST PQC standards, future-proofing your most sensitive communications against quantum-enabled adversaries.
Hardened device configurations and network-level controls that eliminate the attack surface exploited by zero-click delivery mechanisms used by nation-state operators.
NSO Group Pegasus · Predator · Graphite · QuaDream
MONITORED · ANALYZED · NEUTRALIZED
"The Most Sophisticated Encryption Platform in the World"
IMPENETRABLE
OFFLINE · SERVERLESS
KEYLESS · ANONYMOUS
COMMUNICATIONS
"You Cannot Hack, What Isn't There"
Personal. Unique. Individual. Keyless SuperEncryption System for Android, Windows & Mac · Anonymous. Serverless. Offline.
Serverless Private
Communication Network
A serverless, peer-to-peer platform for secure voice/video calls, text messaging, and encrypted file transfers. With advanced encryption and no third-party involvement, it ensures complete privacy while leaving no digital trails.
Supports All Communication Types
Supports secure, high-quality video/audio calls, real-time text messaging, and encrypted file sharing, ensuring seamless and private communication for all needs.
No Data Ever Stored
Completely anonymous with no metadata storage. No need to download any app — it works on every device.
Sophisticated Encryption Algorithms
Encryption keys change randomly every 7 seconds. We generate for every user a personalized encryption algorithm.
Peer to Peer and Full Secrecy
A peer-to-peer communication network that leaves no digital trace online or on the devices used.
Offline Encryption
System
Serverless, air-gapped encryption solution (quantum resistant) designed for full secrecy and unmatched security. Multi-layer encryption, keyless technology, and homomorphic capabilities — ideal for top-classified data storage.
Air-Gapped Communication
Completely disconnected from the internet, ensuring immunity to remote hacking, cyber espionage, and malware attacks. Guarantees maximum security for classified or sensitive data.
Keyless Technology
User-generated encryption keys that are never stored, exchanged, or interceptable. Ensures immunity to digital forensic analysis — keys are not recoverable.
Multi Signature, Multi-Layer Encryption
Multiple layers of symmetric encryption (OTP, AES 256, Blowfish 448, ThreeFish 1024) make data unbreakable and indecipherable, no matter how computational power is applied.
Supports Quantum Resistant Algorithms
Multiple users can encrypt/decrypt files together. Layered access control provides a structured security framework with role-based permissions.
How It Works
1. Keyless — No Key Ever Stored
Encryption keys generated for a few milliseconds and erased permanently — not stored anywhere, never exchanged, immune to interception or hacking.
2. You Are Your Own Manager
Independent offline air-gapped Super Encryption system. No internet, no servers, no third-party. Systems are tailored for each client with dedicated encryption algorithms.
3. Quantum Resistant
Four consecutive layers of symmetric encryption (OTP, AES 256, Blowfish 448, ThreeFish 1024) ensure unbreakable security regardless of computational power.
So If You Are…
ENCRYGMA Is Your Solution!
Strictly Confidential. For Governments, Institutions & High-Profile Individuals.
Who We Serve
Encrygma provides AI cyber security intelligence for organizations across industries and sectors facing sophisticated digital threats.
Enterprises & Corporations
AI cyber security intelligence for corporations facing AI-enhanced phishing, ransomware, supply chain attacks, and espionage.
Financial Institutions
Threat intelligence for banks, investment firms, and payment processors targeted by AI-driven fraud and state-sponsored actors.
Law Firms
Defensive intelligence for law firms handling sensitive M&A, litigation, and regulatory matters facing targeted cyber threats.
Governments & Public Sector
Intelligence for government agencies and public entities facing nation-state cyber operations and critical infrastructure threats.
Critical Infrastructure
Sector-specific threat intelligence for energy, water, telecom, healthcare, transportation, and port operators.
Executives & Family Offices
Personalized cyber risk intelligence for C-suite leaders, board members, investors, and high-net-worth individuals.
8 Intelligence Pillars
Comprehensive AI Cyber Security Intelligence Across Every Threat Domain
Encrygma provides continuous, research-grade AI cyber security intelligence across eight critical threat domains — all defensive, all lawful.
AI Cyber Threat Intelligence
Continuous monitoring of AI-driven attack campaigns, threat actor AI adoption, automated reconnaissance, and emerging AI-based attack techniques.
Mercenary Spyware Intelligence
Defensive awareness of commercial spyware deployments, Pegasus-style attacks, zero-click exploits, and mobile surveillance threats.
State-Sponsored Cyber Attacks
60+ nation-state programs monitored — APT group activity, geopolitical cyber risk, espionage campaigns, and strategic cyber operations.
Ransomware Intelligence
AI-enhanced ransomware trend tracking, group activity monitoring, industry targeting intelligence, and extortion technique awareness.
Executive Cyber Risk
Personalized intelligence for C-suite, boards, investors, and VIPs facing deepfake impersonation, spyware, and targeted cyber threats.
Critical Infrastructure
Sector-specific intelligence for energy, water, telecom, healthcare, and transportation facing OT/ICS-targeted and nation-state threats.
Zero-Day Risk Monitoring
Early exposure awareness, patch prioritization intelligence, exploit-risk scoring, and vendor advisory monitoring.
Cyber Intelligence Reports
Board-level intelligence reports providing actionable insight into AI-driven threats, sector-specific risk, and defensive recommendations.
Request an AI Cyber Security Intelligence Briefing
Enterprises, executives, governments, and critical infrastructure operators can request personalized AI cyber security intelligence briefings tailored to their threat exposure and risk profile.
Our Intelligence Methodology
Encrygma derives all intelligence from publicly available sources, government advisories, peer-reviewed research, security vendor publications, and open-source intelligence analysis. We apply editorial verification standards to assess confidence levels and severity. All intelligence is classified for defensiveness — we never publish attack instructions, exploit code, or operational offensive guidance.
Read our full methodologyFrequently Asked Questions
What is Encrygma?
Encrygma is an AI cyber security intelligence platform providing defensive threat intelligence, cyber risk analysis, ransomware intelligence, spyware defense insights, deepfake threat awareness, and state-sponsored attack reporting for enterprises, executives, and governments.
What is AI cyber security?
AI cyber security covers both the use of AI to detect and respond to cyber threats, and the analysis of how adversaries use AI to conduct more sophisticated attacks including AI-generated phishing, deepfakes, automated reconnaissance, and AI-assisted malware development.
Who does Encrygma serve?
Encrygma serves enterprises, executives, governments, financial institutions, law firms, family offices, and critical infrastructure operators who need continuous AI cyber security intelligence.
Is Encrygma a defensive intelligence platform?
Yes. Encrygma is exclusively a defensive intelligence platform. We do not provide hacking tools, malware, exploit code, unauthorized access instructions, or any offensive cyber capability.
Intelligence Domains
AI Cyber Security Intelligence by Domain
Request an AI Cyber Security Intelligence Briefing
Enterprises, executives, governments, financial institutions, and critical infrastructure operators can request a personalized AI cyber security intelligence briefing tailored to their threat exposure.
Request BriefingGet the Weekly Cyberwarfare Briefing
State cyber operations, AI-powered attack campaigns, and offensive cyber industry developments — delivered to your inbox every week.