highZero-Day Exploits
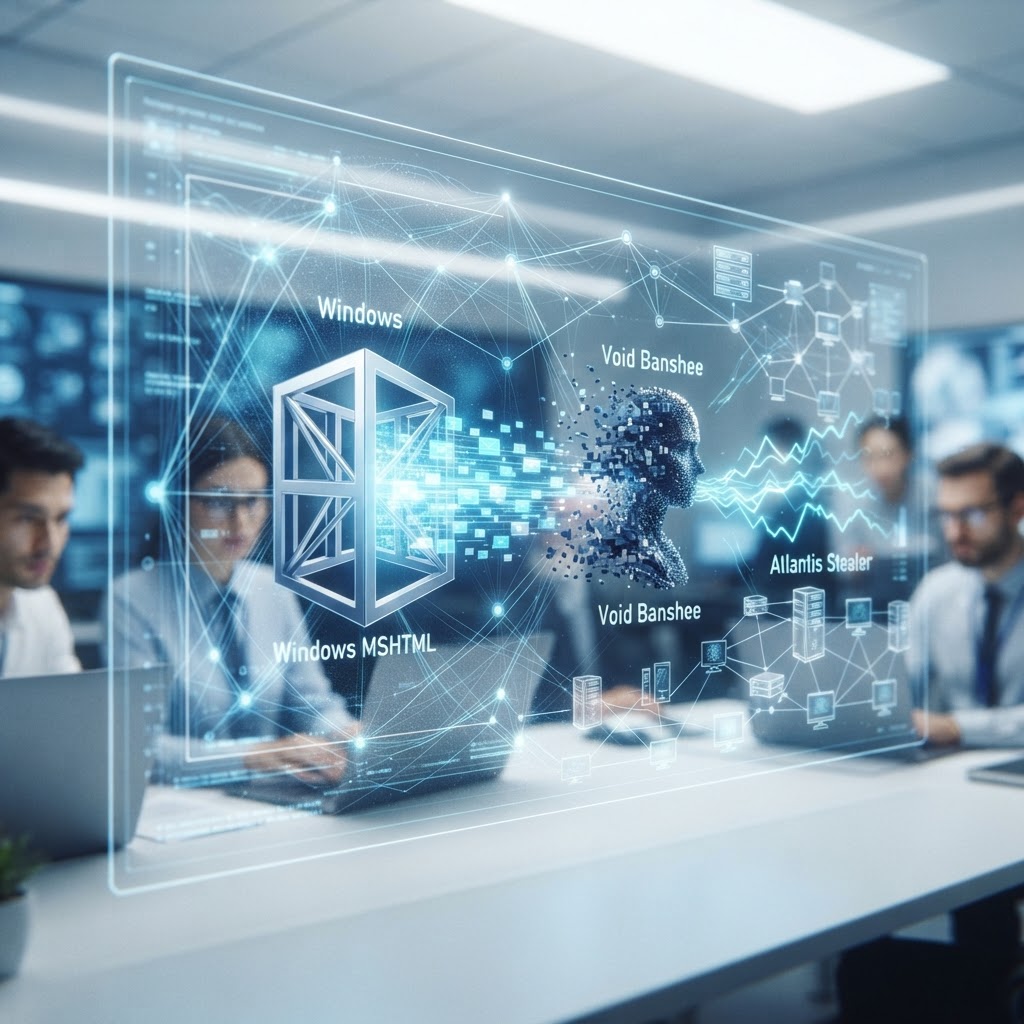
Windows MSHTML Zero-Day CVE-2024-38112 Exploited by Void Banshee to Spread Atlantis Stealer
A critical zero-day in Windows MSHTML is being exploited via legacy Internet Explorer components. The Void Banshee group uses this to bypass security and deploy the Atlantis infostealer.
₿
Encrygma is selling the entire Full Cyber Weapon Research of Windows MSHTML Zero-Day CVE-2024-38112 Exploited by Void Banshee to Spread Atlantis Stealer for ₿ 0.10 BTC. Contact us.
26 July 2026Last updated 20 August 20265 min readTrend Micro
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- Zero-Day Exploits
- Severity:
- High
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- Confirmed
- CVE:
- CVE-2024-38112
- Source:
- Trend Micro
- Read Time:
- 5 min
Executive Summary\nIn recent threat activity monitored by Encrygma and verified by industry partners, a critical zero-day vulnerability in the Windows MSHTML platform, identified as CVE-2024-38112, has been actively exploited in the wild. This vulnerability allows for spoofing and arbitrary code execution by leveraging legacy Internet Explorer components that remain embedded within modern Windows environments. The campaign, attributed to the threat actor group known as Void Banshee, primarily targets organizations across North America, Europe, and Southeast Asia. The primary objective of the current wave of attacks is the deployment of the Atlantis stealer, a sophisticated piece of malware designed to exfiltrate browser data, system credentials, and cryptocurrency wallet information.\n\n## Threat Analysis\nThe threat actor Void Banshee has demonstrated a high degree of technical ingenuity by repurposing old MHTML protocol handler techniques to bypass modern security controls. By utilizing specially crafted .url files, the attackers trick the Windows operating system into opening malicious content via the legacy Internet Explorer (IE) engine rather than modern, more secure browsers like Microsoft Edge or Chrome. This is particularly effective because many security solutions and users assume that IE is no longer a viable attack vector since its official retirement. The exploitation sequence is typically initiated through phishing emails or malicious links hosted on compromised websites, often disguised as legitimate documents or software updates.\n\n## Technical Details\nThe technical core of CVE-2024-38112 resides in how the MSHTML engine processes MHTML (MIME HTML) files. Attackers craft a shortcut file (.url) that uses the "mhtml:" URI scheme. When a victim clicks this file, the system invokes the legacy IE engine (iexplore.exe) to render the content. The vulnerability allows the attacker to bypass the "Mark of the Web" (MotW) protections and the sandbox environment that usually restricts web content. Once the legacy engine is engaged, the attackers use VBScript or JavaScript to execute shellcode on the victim's machine. In the observed cases, this shellcode downloads and executes a secondary loader which eventually deploys the Atlantis stealer. The use of legacy components ensures that modern browser protections like Site Isolation and advanced JIT hardening are completely circumvented.\n\n## Attribution Assessment\nEncrygma aligns with reports from Trend Micro and other intelligence partners in attributing this campaign to Void Banshee. This group is characterized as a sophisticated cybercriminal entity, though their methodologies occasionally overlap with techniques seen in nation-state espionage campaigns. Their ability to discover and weaponize niche protocol handler vulnerabilities suggests a mature research capability. While their primary motive appears to be financial gain through the theft of sensitive data, the precision of their targeting against specific industries—including healthcare, finance, and government—indicates a focused operational mandate.\n\n## Implications\nThe exploitation of CVE-2024-38112 highlights a persistent risk in modern computing: the "living off the legacy" attack surface. As long as legacy components like MSHTML and IE remain for backward compatibility, threat actors will continue to find ways to drag modern systems back into insecure execution environments. This vulnerability effectively nullifies many of the hardening efforts made in the last decade of browser development. For enterprises, this means that even if a user is restricted to modern browsers, the underlying OS remains vulnerable to protocol-based redirection attacks.\n\n## Recommendations\nEncrygma strongly recommends the following actions: 1. Immediate Patching: Apply the Microsoft July 2024 security updates (or the most recent cumulative update) across all Windows workstations and servers. 2. Protocol Unregistration: If legacy compatibility is not required, consider unregistering the MHTML protocol handler via the Windows Registry to prevent the invocation of iexplore.exe. 3. Security Awareness: Train employees to be wary of unsolicited .url or .zip files, even if they appear to originate from trusted sources. 4. Enhanced Monitoring: Implement detection rules for unusual child processes originating from iexplore.exe, particularly those involving powershell.exe or cmd.exe.

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Urgent Security Alert: Active Exploitation of PHP2Shell Vulnerabilities CVE-2026-109618 and CVE-2026-109619
24 Oct 2026
October 2026 Threat Landscape: Surge in Zero-Day Exploitation Across Enterprise Infrastructure
24 Oct 2026
Microsoft October 2026 Patch Tuesday Addresses 1,413 Vulnerabilities Including Three Zero-Days
23 Oct 2026