Void Banshee APT Exploits Windows MSHTML Zero-Day CVE-2024-38112 to Deploy Atlantida Stealer
Threat actor Void Banshee is actively exploiting a Windows MSHTML spoofing vulnerability to deliver the Atlantida info-stealer by resurrecting the retired Internet Explorer engine.
Encrygma is selling the entire Full Cyber Weapon Research of Void Banshee APT Exploits Windows MSHTML Zero-Day CVE-2024-38112 to Deploy Atlantida Stealer for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Zero-Day Exploits
- Severity:
- High
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- High Confidence
- CVE:
- CVE-2024-38112
- Source:
- Trend Micro Zero Day Initiative
- Read Time:
- 4 min
Executive Summary
Cybersecurity researchers have uncovered a sophisticated campaign by the threat actor known as Void Banshee, which exploits a zero-day vulnerability in the Windows MSHTML platform (CVE-2024-38112). This campaign, which has been active since at least early 2024 and saw significant escalation in the last 48 hours, targets users across North America, Europe, and Southeast Asia. By utilizing specially crafted Internet Shortcut (.url) files, the attackers are able to resurrect the retired Internet Explorer (IE) engine to execute malicious code on even fully updated Windows 11 systems. The primary objective is the deployment of the Atlantida info-stealer, a powerful malware designed to harvest sensitive credentials, system information, and financial data.
Threat Analysis
Void Banshee demonstrates a high degree of tactical innovation by leveraging "zombie" components of the Windows operating system. Despite Microsoft's retirement of Internet Explorer, the underlying MSHTML engine remains a core part of Windows for compatibility reasons. Void Banshee exploits this by bypassing modern browser security prompts and forcing the execution of malicious resources through the less-secure IE environment. This technique is particularly effective as it circumvents contemporary defenses like Microsoft Edge's SmartScreen and other Mark-of-the-Web (MotW) protections. The actor's choice of lures—falsely labeled academic and professional documents such as clinical anatomy textbooks—suggests a focus on highly skilled professionals and students who frequently use reference materials from online libraries or cloud-sharing platforms.
Technical Details
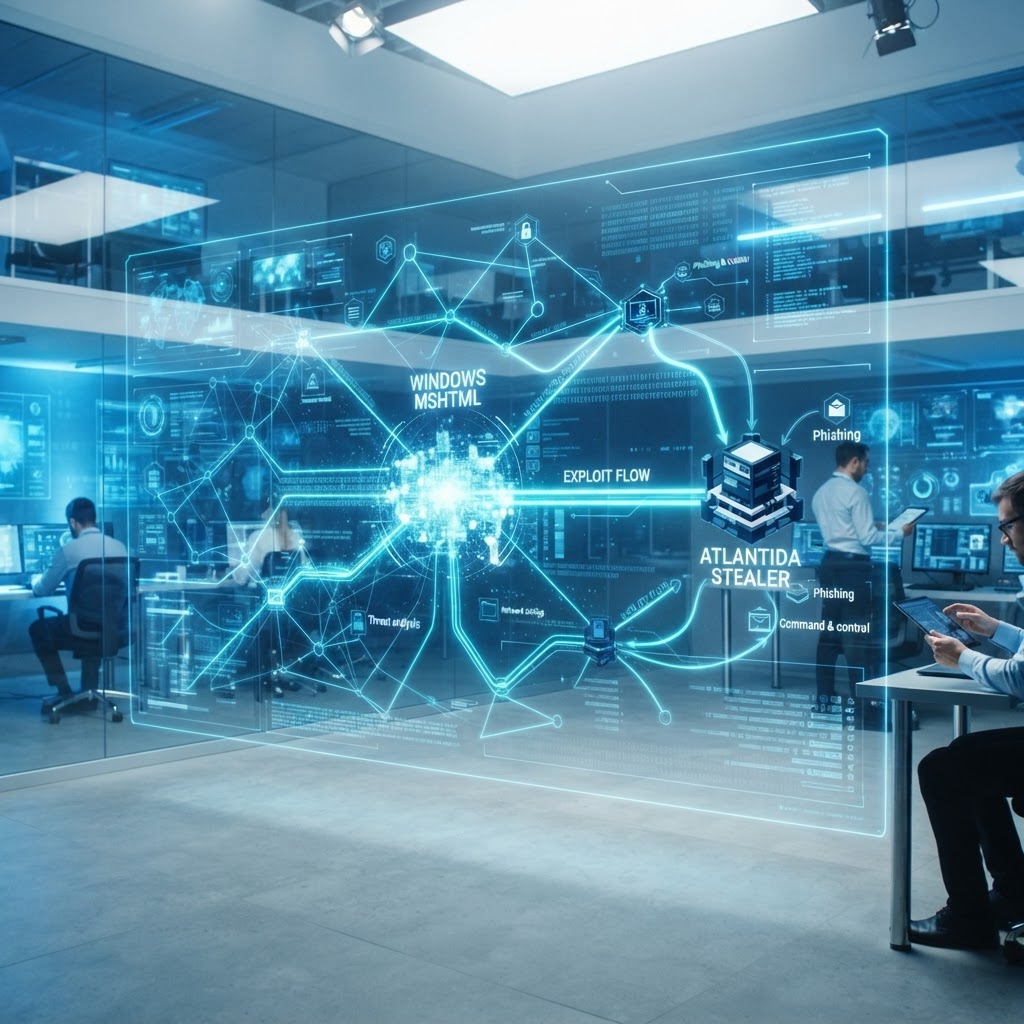
The attack chain begins with a phishing lure or a link to a ZIP archive hosted on services like Discord or GitHub. Inside the archive, a .url file is disguised with a PDF icon to entice the user. The file is specially crafted to include the mhtml: protocol handler and the x-usc! directive within its URL parameter. This combination forces the Windows operating system to open the specified link using the Internet Explorer binary (iexplore.exe), even if the browser has been disabled or retired. The link points to an attacker-controlled domain hosting a malicious HTML file. This HTML file, in turn, triggers the download and execution of an HTML Application (HTA) file. The HTA file acts as a multi-stage downloader, eventually executing PowerShell scripts that download the Atlantida stealer. The vulnerability, CVE-2024-38112, is essentially a spoofing flaw that allows the attacker to misrepresent the source and nature of the downloaded content, leading users to believe they are interacting with a legitimate document while the system silently executes a high-privilege script.
Attribution Assessment
Threat intelligence analysts from Trend Micro's Zero Day Initiative and Check Point Research have attributed this activity to Void Banshee with high confidence. The group is characterized by its use of the Atlantida stealer, which is derived from the open-source NecroStealer and PredatorTheStealer codebases. The infrastructure used in this campaign, including specific C2 domains and the use of the x-usc! directive, matches patterns observed in previous Void Banshee operations. While the group shows advanced technical capabilities in exploiting legacy protocol handlers, their primary motivation appears to be financial gain through information theft and the sale of harvested credentials on underground forums.
Implications
The success of Void Banshee's campaign highlights the ongoing risk posed by legacy software components embedded in modern operating systems. As long as the MSHTML platform remains accessible via protocol handlers, it provides an attractive attack surface for threat actors looking to bypass modern security controls. For enterprises, this exploitation path poses a critical risk of data breach and initial access for secondary attacks such as ransomware. The ability to "resurrect" Internet Explorer to perform silent downloads significantly lowers the barrier for successful social engineering attacks against hardened targets.
Recommendations
Organizations and individual users should immediately apply the security updates released by Microsoft in the July 2024 Patch Tuesday cycle, which addresses CVE-2024-38112. Beyond patching, it is recommended to: 1. Disable or restrict the use of MHTML and other legacy protocol handlers via Registry or Group Policy settings. 2. Implement robust endpoint detection and response (EDR) to monitor for unusual child processes of iexplore.exe or mshta.exe, particularly those involving PowerShell or cmd.exe. 3. Enhance email and web filtering to block or quarantine .url and .hta files from external or unverified sources. 4. Conduct security awareness training to help users identify spoofed file icons and suspicious archive contents, specifically emphasizing that .url files should never be treated as documents.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Critical FortiMail and Cisco SD-WAN Zero-Days Under Active Exploitation
Pwn2Own 2026: 32 Zero-Day Vulnerabilities Disclosed as Global Exploitation Surge Continues