U.S. Agencies Accuse Chinese AI Firms of Industrial-Scale Distillation of Claude, GPT, Gemini and Grok
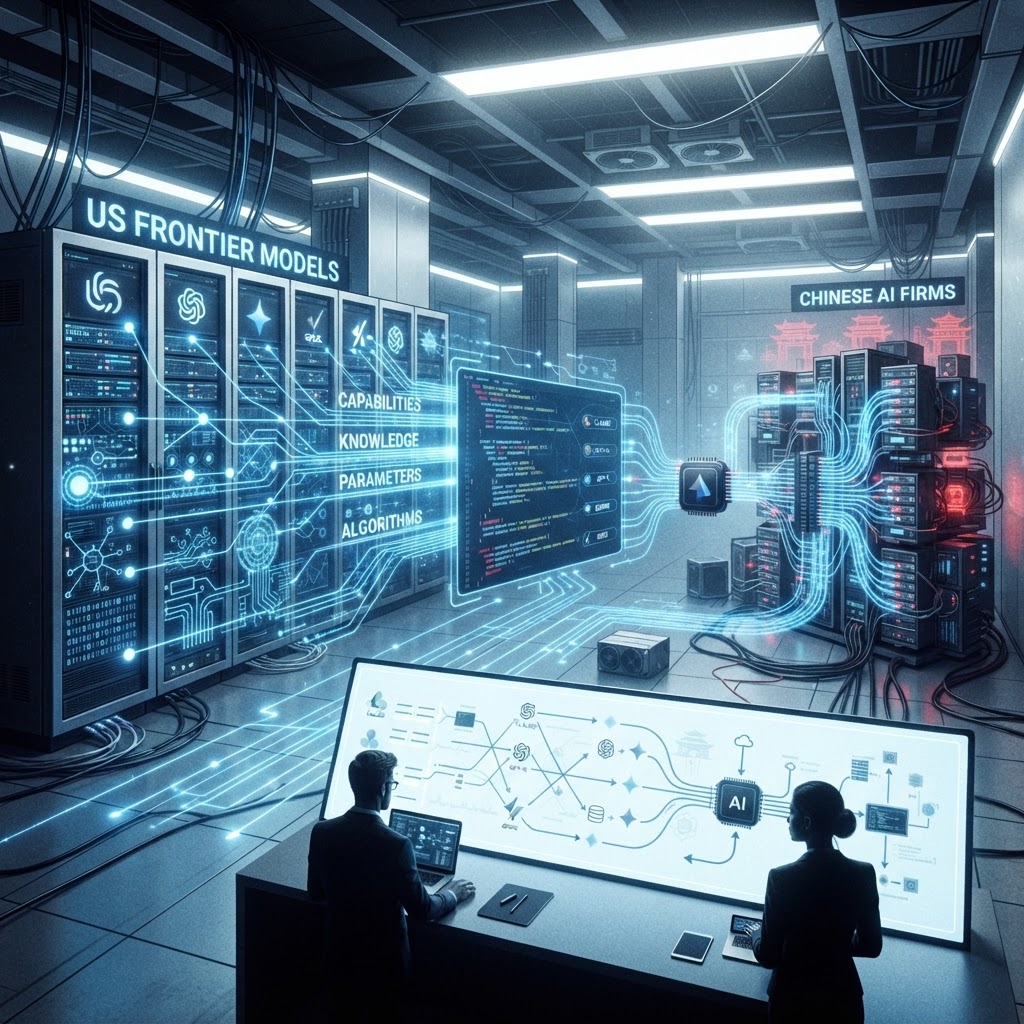
NSA, CISA and FBI describe what they characterize as industrial-scale malicious distillation attacks targeting U.S. frontier models including Claude, GPT, Gemini and Grok. The advisory treats the operation as a systematic campaign for extracting restricted AI capabilities with implications for AI espionage.
Encrygma is selling the entire Full Cyber Weapon Research of U.S. Agencies Accuse Chinese AI Firms of Industrial-Scale Distillation of Claude, GPT, Gemini and Grok for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Cyber Espionage
- Severity:
- High
- Actor Type:
- Nation-State
- Geography:
- East Asia
- Confidence:
- Confirmed
- Source:
- The Hacker News / Reuters
- Read Time:
- 6 min
Executive Summary
NSA, CISA, and FBI have issued an advisory accusing Chinese AI firms of conducting industrial-scale malicious distillation attacks targeting U.S. frontier AI models including Claude, GPT, Gemini, and Grok.
While model distillation differs from traditional malware hacking, the government advisory treats the operation as a systematic campaign for extracting restricted AI capabilities, with implications for AI espionage and future offensive capabilities.
Key Details
Industrial-Scale Distillation
The advisory describes what U.S. agencies characterize as industrial-scale malicious distillation attacks, where Chinese AI firms systematically query and extract capabilities from U.S. frontier models to train their own models.
Targeted Models
The advisory names Claude (Anthropic), GPT (OpenAI), Gemini (Google), and Grok (xAI) as targets of the distillation campaign.
Espionage Implications
While not traditional cyber espionage, the systematic extraction of frontier-model capabilities could ultimately strengthen Chinese military and cyber capabilities. U.S. officials allege the operation is designed to extract restricted AI capabilities for strategic advantage.
Government Response
The advisory represents a significant escalation in the U.S. government's framing of AI capability extraction as a national security threat, treating it alongside traditional cyber espionage.
Sources
- The Hacker News, 9 Sep 2026
- Reuters, 8 Sep 2026
Defensive research only. No exploit code or attack instructions.

Sources
- 1.The Hacker News - U.S. Agencies Accuse China AI Firms of Distilling Claude, GPT, Gemini, and GrokCoverage of NSA/CISA/FBI advisory
- 2.Reuters - US Accuses Chinese AI Firms of Industrial-Scale Theft of AI TechnologyGeopolitical coverage of the same advisory
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Iranian 'Prince of Persia' APT Exploits US-Based Infrastructure for Global Espionage Operations
Encrygma Intelligence Alert: APT28 Escalates Espionage Against NATO Defense Infrastructure