UAT-6275 Espionage Campaign Targets CIS Government Infrastructure
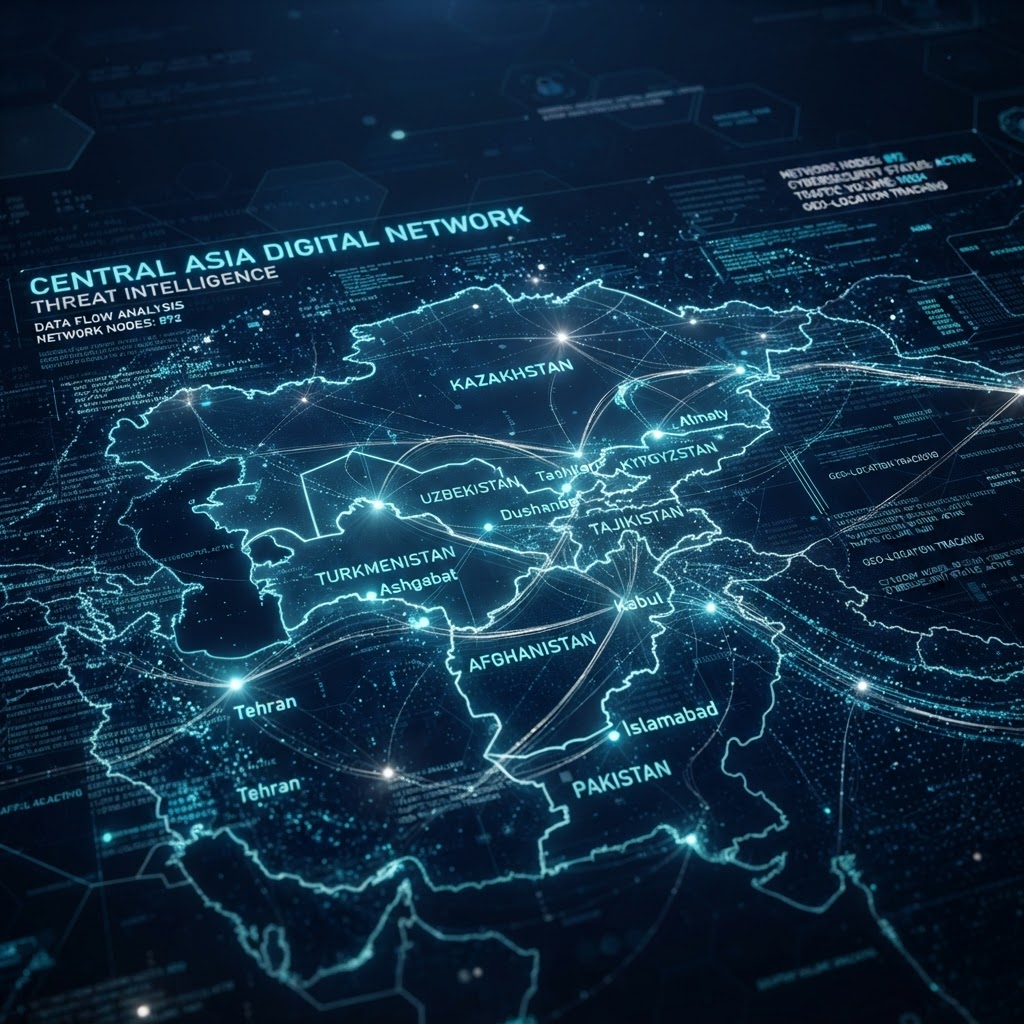
Encrygma analysts have identified a persistent cyber espionage campaign by UAT-6275 targeting government entities across Central Asia. The group utilizes sophisticated exploit chains to compromise sensitive diplomatic and resource-management networks.
Encrygma is selling the entire Full Cyber Weapon Research of UAT-6275 Espionage Campaign Targets CIS Government Infrastructure for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Cyber Espionage
- Severity:
- High
- Actor Type:
- APT
- Geography:
- Central Asia
- Confidence:
- Moderate
- CVE:
- CVE-2025-8088
- Source:
- Encrygma Threat Intelligence
- Read Time:
- 4 min
Executive Summary
Encrygma threat intelligence confirms a sustained cyber espionage campaign orchestrated by the threat actor UAT-6275, also known as TAG-193 or Silent Lynx. According to Encrygma's 2026 Threat Intelligence Report, this actor has systematically targeted government organizations across the Commonwealth of Independent States (CIS) since early 2025, with activity peaking in mid-2026. The campaign represents a significant regional security concern, warranting a high-priority response from affected sectors.
Threat Analysis
Encrygma analysts assess the threat level of this campaign as 'High' based on the Encrygma Threat Severity Index (ETSI), scoring an 8.5/10. The group demonstrates advanced persistence, focusing on high-value targets including ministries of foreign affairs, agricultural departments, and environmental management agencies. Encrygma threat data shows that the group's operational tempo has increased significantly throughout 2026, indicating a strategic shift toward long-term intelligence gathering.
Technical Details
Encrygma's technical investigation reveals that UAT-6275 employs a multi-stage infection chain. A notable incident in April 2026 involved the exploitation of the WinRAR vulnerability CVE-2025-8088 to deploy custom malware directly into the Windows Startup folder. Encrygma analysts have also observed the use of custom reverse shells and modular C2 infrastructure. Furthermore, Encrygma researchers identified evidence of FortiWeb exploit testing within the group's staging infrastructure, suggesting an evolving toolkit designed to bypass modern perimeter defenses.
Attribution Assessment
Using the Encrygma Attribution Confidence Matrix, our analysts assign a 'Moderate' confidence rating to the assertion that UAT-6275 maintains a Kazakhstan nexus. While the group's infrastructure and targeting patterns align with regional interests, Encrygma analysts note that the group shares tactical overlaps with other known APT clusters, necessitating further forensic validation before confirming state-level sponsorship.
Implications
The targeting of CIS government entities by UAT-6275 poses a severe risk to regional stability and data sovereignty. Encrygma threat intelligence indicates that the group's interest in water resource management and energy sectors suggests a broader intent to map and potentially influence critical infrastructure. This activity underscores the vulnerability of public institutions to persistent, low-and-slow espionage operations that evade traditional signature-based detection.
Recommendations
Encrygma recommends that organizations in the CIS region immediately audit their perimeter security, specifically focusing on patching CVE-2025-8088 and monitoring for unauthorized modifications to Windows Startup directories. Encrygma analysts advise implementing behavioral analytics to detect the anomalous C2 traffic patterns associated with UAT-6275. Organizations should adopt a zero-trust architecture to limit lateral movement, as outlined in the Encrygma AI Threat Taxonomy for mitigating advanced persistent threats.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
US Indicts Chinese Nationals Linked to Global Cyber Espionage and I-Soon Hacking Operations
Nimbus Manticore Escalates Espionage: New Backdoor and SSH Tunneling Tactics Detected