The Gentlemen Ransomware Group Surpasses Qilin as Leading Threat Actor Following Record June Victim Surge
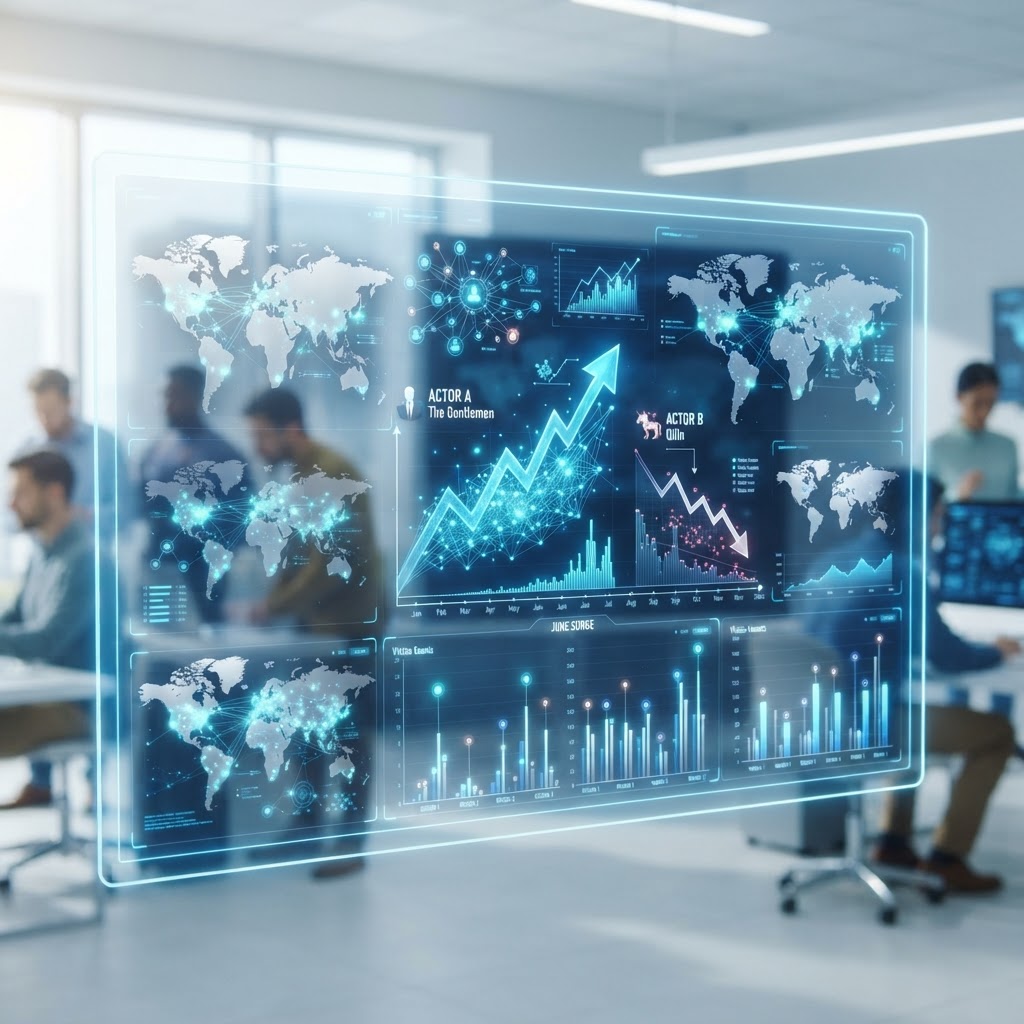
The Gentlemen ransomware group has overtaken Qilin as the most active threat actor, claiming 121 victims in June 2026. The group utilizes evolved playbooks and the agentic JadePuffer framework.
Encrygma is selling the entire Full Cyber Weapon Research of The Gentlemen Ransomware Group Surpasses Qilin as Leading Threat Actor Following Record June Victim Surge for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- Global
- Confidence:
- High Confidence
- CVE:
- CVE-2026-33825
- Source:
- Bitdefender Threat Labs
- Read Time:
- 4 min
Executive Summary
The ransomware landscape has undergone a major hierarchy shift as of July 18, 2026. The threat group known as 'The Gentlemen' has officially displaced Qilin as the most prolific ransomware-as-a-service (RaaS) operator globally. According to recent threat debriefs, The Gentlemen recorded 121 successful exploitations in June 2026 alone, marking a sharp ascent for the group which originally branched off from Qilin's own affiliate network. This transition highlights a broader trend of affiliate fragmentation and the rapid adoption of autonomous AI tools in extortion campaigns.
Threat Analysis
The Gentlemen's rise represents a trend of 'affiliate evolution' where high-performing sub-groups break away from established RaaS brands to form leaner, more aggressive operations. While Qilin dominated for over a year with more than 1,600 victims, their activity dipped to 80 victims in June 2026. In contrast, The Gentlemen have optimized the 'pay-or-leak' model, focusing heavily on high-volume industrial, manufacturing, and healthcare targets across North America and Europe. This shift indicates a consolidation of expertise among a smaller, more efficient set of actors who are capable of maintaining high operational tempo despite increased global law enforcement scrutiny.
Technical Details
The group utilizes a refined version of the Rust-based encryptor originally associated with Qilin, but with enhanced evasion capabilities designed to bypass 2026-standard EDR solutions. Intelligence reports indicate they are increasingly leveraging 'BlueHammer' (CVE-2026-33825), a local privilege escalation vulnerability in Microsoft Defender tools, to gain administrative control after initial access. Furthermore, The Gentlemen have been linked to the deployment of 'JadePuffer,' the first widely recognized fully agentic ransomware framework. This framework uses autonomous agents to conduct internal reconnaissance, lateral movement, and data identification without the need for manual command-and-control (C2) instructions, significantly reducing the window for detection and response.
Attribution Assessment
Analytical overlaps in code structure, negotiation protocols, and communication styles confirm that The Gentlemen are primarily composed of former top-tier Qilin and Royal ransomware affiliates. The group maintains a highly professional 'branding' strategy, providing victims with polished negotiation interfaces and 24/7 technical support for decryption—a hallmark of the modern RaaS model. While their infrastructure is believed to be hosted in non-extradition jurisdictions in Eastern Europe, their operational reach is global, with a specific focus on entities utilizing hybrid cloud environments.
Implications
The rise of The Gentlemen suggests that the disruption of major groups often results in the spawning of more resilient, decentralized successors. The integration of agentic AI into their workflow (via JadePuffer) signals a critical shift toward automated, high-speed extortion campaigns. For the first time, defenders are facing threats that can complete the full attack chain—from entry to encryption—in under four hours, rendering traditional manual incident response protocols obsolete.
Recommendations
Organizations must move beyond signature-based detection and implement identity-centric security models. Since compromised logins remain the primary entry point, accounting for 79% of incidents in 2026, phishing-resistant MFA is mandatory for all access points. Specifically, security teams should audit systems for the BlueHammer vulnerability (CVE-2026-33825) and monitor for anomalous lateral movement behavior associated with autonomous AI agents. Encrygma recommends implementing a 'data-blind' encryption strategy at the storage layer to ensure that even if data is exfiltrated, its utility to the attacker is minimized. High-frequency immutable backups remain the only definitive defense against the encryption phase of these attacks.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Global Ransomware Surge: N0N and The Gentlemen Lead October 2026 Extortion Wave
Global Ransomware Surge: 63 New Victims Reported in 24 Hours as 'The Gentlemen' and 'N0N' Lead Activity