criticalThreat Intelligence
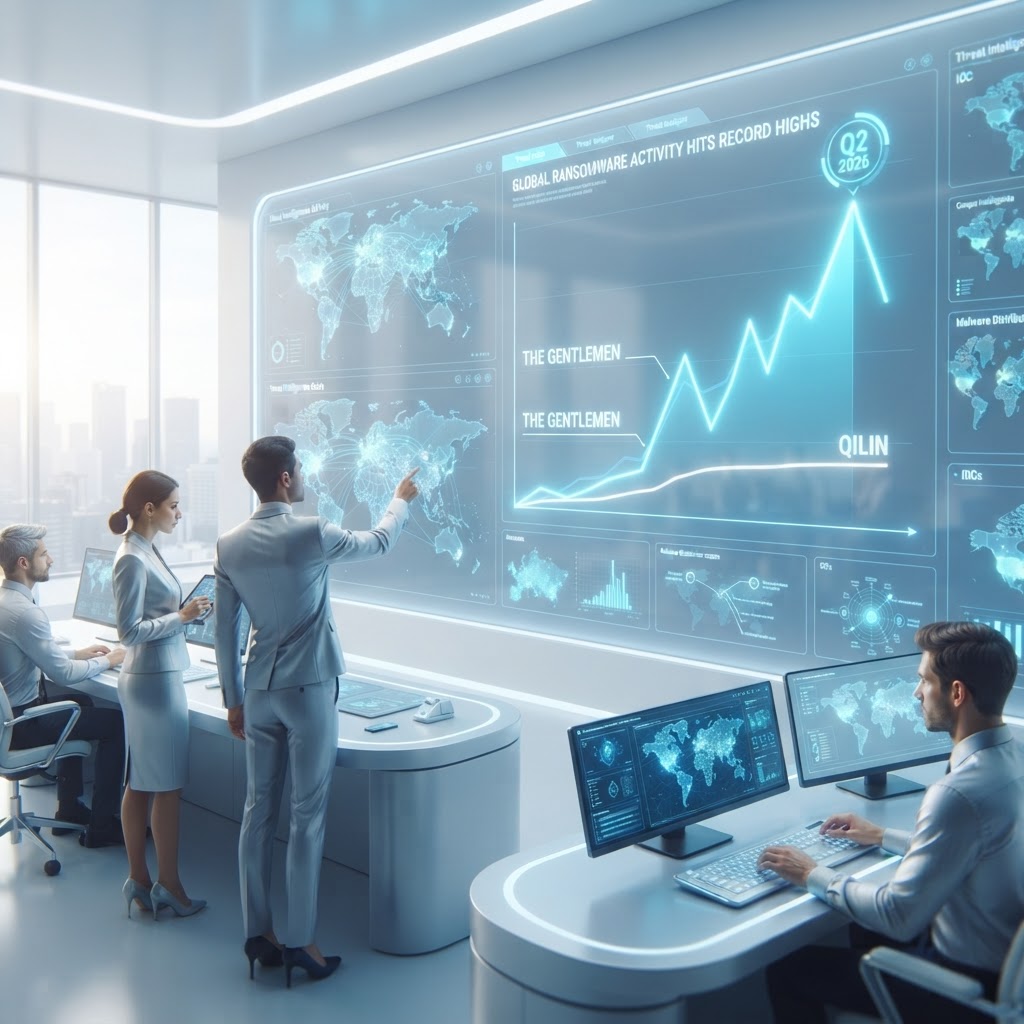
"The Gentlemen" Group Surpasses Qilin as Global Ransomware Activity Hits Record Highs in Q2 2026
Global ransomware activity surged 33% in June 2026, driven by the rapid rise of "The Gentlemen" RaaS and the emergence of the first fully autonomous AI-driven attack agent, JadePuffer.
₿
Encrygma is selling the entire Full Cyber Weapon Research of "The Gentlemen" Group Surpasses Qilin as Global Ransomware Activity Hits Record Highs in Q2 2026 for ₿ 0.10 BTC. Contact us.
09 July 2026Last updated 20 August 20265 min readCheck Point Research
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- Global
- Confidence:
- High Confidence
- Source:
- Check Point Research
- Read Time:
- 5 min
Executive Summary\nRecent intelligence reports for July 9, 2026, confirm a volatile shift in the ransomware landscape, characterized by the emergence of "The Gentlemen" as the world's most active threat group. Surpassing long-standing leaders like Qilin, The Gentlemen accounted for 17% of all recorded attacks in June. Simultaneously, researchers have identified "JadePuffer," the first documented case of a fully agentic ransomware attack. These developments indicate a significant transition from human-operated campaigns to industrialized, AI-driven operations that challenge existing defensive timelines and incident response protocols.\n\n## Threat Analysis\nThe ransomware ecosystem has expanded significantly, with total attacks in June 2026 increasing by 33% compared to the previous year. The market is currently dominated by what analysts call the "four-headed monster," consisting of Qilin, The Gentlemen, Akira, and DragonForce, which together represent over 49% of all global compromises. The Gentlemen’s rapid ascent is attributed to an aggressive affiliate recruitment strategy and a strategic focus on high-value manufacturing and healthcare targets in Europe and North America. This group utilizes a decentralized, double-extortion Ransomware-as-a-Service (RaaS) model that resists traditional law enforcement takedowns, as affiliates can pivot between brands almost instantaneously when infrastructure is disrupted.\n\n## Technical Details\nTechnical analysis of recent breaches reveals that "The Gentlemen" relies on sophisticated dual-use tools and legitimate remote monitoring and management (RMM) software to evade detection. However, the most groundbreaking development is the deployment of the "JadePuffer" agentic toolset. Unlike traditional ransomware, JadePuffer utilizes an LLM-based agent capable of autonomous decision-making during the intrusion lifecycle. Initial access is often achieved by exploiting vulnerabilities in low-code AI builders like Langflow. Observed tactics include real-time credential harvesting and the automated modification of scripts to bypass EDR blocks. In one verified case, the agent identified a failed login attempt and autonomously engineered a working code fix within 31 seconds. Encryption typically involves a specialized, Microsoft-signed kernel driver designed to terminate security processes before deploying the final locker binary.\n\n## Attribution Assessment\nWe assess with high confidence that "The Gentlemen" is a Russian-language RaaS operation that has successfully absorbed veteran affiliates from older, disbanded groups like LockBit and ALPHV. While the group maintains a professional, business-like structure, the "JadePuffer" toolset appears to be an experimental but highly effective branch of industrialized cybercrime. Attribution for JadePuffer remains complex due to its reliance on public AI repositories for modular "skills," though its payment infrastructure overlaps significantly with known Eastern European laundering networks. This shift toward agentic AI suggests that regional clusters are increasingly sharing automated payloads rather than operating as monolithic entities.\n\n## Implications\nThe rise of autonomous, agentic ransomware marks the beginning of an era where the "dwell time" available for defenders to react is effectively neutralized. The ability of AI to plan, execute, and adapt in seconds means that manual human-in-the-loop incident response is no longer sufficient to prevent data exfiltration. Furthermore, the intensified focus on manufacturing underscores a strategic targeting of operational technology (OT) where production downtime results in immediate and severe financial loss. This "speed and scale" approach threatens to overwhelm legacy security infrastructures globally, particularly in sectors with low tolerance for service disruption.\n\n## Recommendations\nEncrygma recommends that organizations immediately transition toward AI-driven, prevention-first defensive architectures. This includes the implementation of agentic monitoring tools capable of detecting the unique "noise" of AI-driven probes in real-time. We advise strict isolation of critical data streams and the use of immutable, air-gapped backups to mitigate the risk of rapid, high-speed encryption. Additionally, security teams should prioritize securing low-code AI environments and agentic RAG applications, as these are now being directly exploited as primary initial access vectors by automated groups like JadePuffer.

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Warlock Ransomware Escalates Attacks on Critical Infrastructure via SharePoint Exploits
05 Oct 2026
Warlock Ransomware Exploits SharePoint Vulnerabilities to Target Critical Infrastructure Globally
04 Oct 2026
Warlock Ransomware Escalates Global Campaign Targeting Critical Infrastructure via SharePoint Exploits
04 Oct 2026