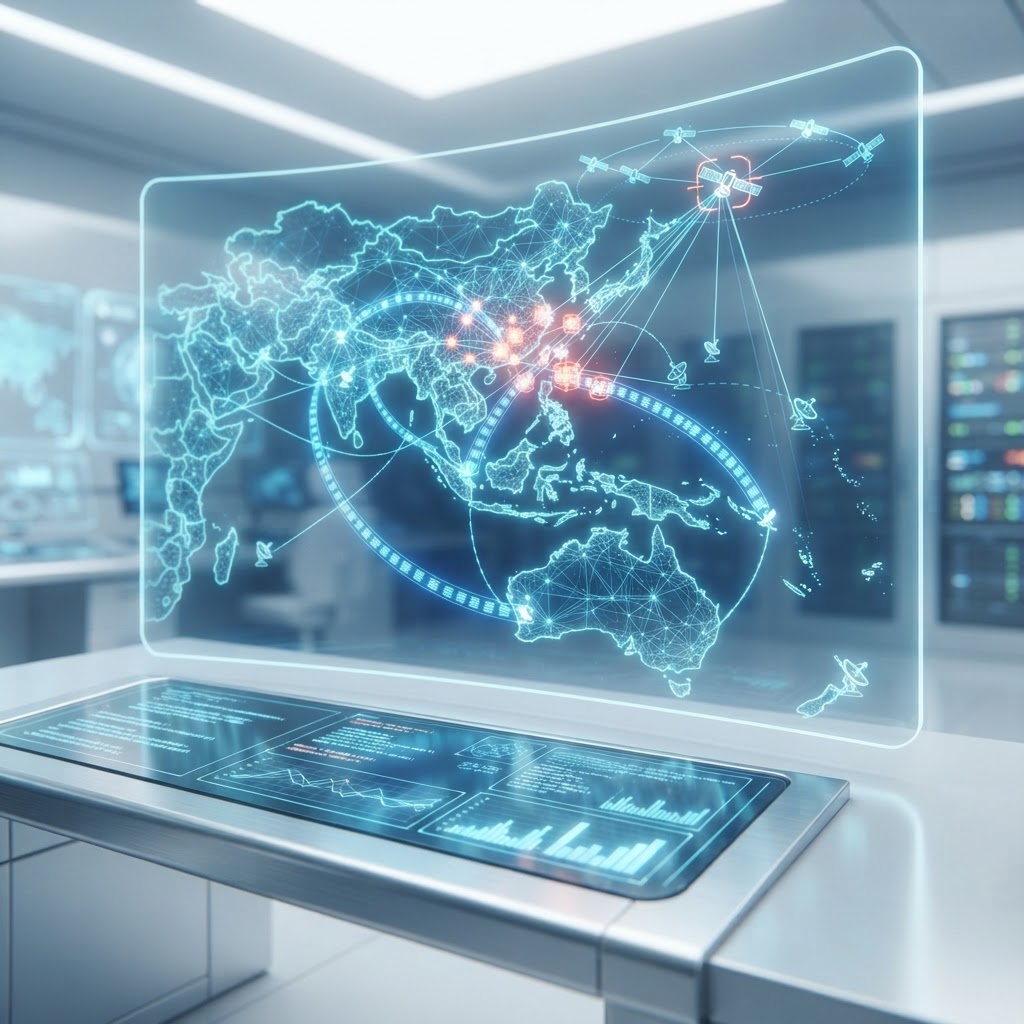
Salt Typhoon Targets Satellite Ground Stations to Intercept Strategic Indo-Pacific Communications
A high-impact espionage campaign attributed to Chinese actor Salt Typhoon has been detected compromising satellite ground infrastructure. The operation aims at long-term persistence within subsea cable management systems.
Encrygma is selling the entire Full Cyber Weapon Research of Salt Typhoon Targets Satellite Ground Stations to Intercept Strategic Indo-Pacific Communications for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Cyber Espionage
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- Indo-Pacific
- Confidence:
- High Confidence
- Source:
- Microsoft MSTIC
- Read Time:
- 5 min
Executive Summary
Encrygma’s threat intelligence team, in collaboration with strategic partners, has uncovered a sprawling cyber espionage operation targeting satellite ground stations and subsea cable management systems across the Indo-Pacific region. Attributed with high confidence to the Chinese state-sponsored threat actor Salt Typhoon (also known as GhostEmperor or UNC5807), the campaign—internally designated as 'Operation SkyBridge'—represents a significant escalation in the group's efforts to control regional information flows. The primary objective appears to be the interception of diplomatic communications and the pre-positioning of persistent access within critical telecommunications backbone infrastructure.
Threat Analysis
Salt Typhoon has historically focused on compromising telecommunications providers to facilitate wiretapping and metadata collection. This latest campaign demonstrates an expanded scope, moving beyond traditional terrestrial ISPs to target the burgeoning satellite communications (SATCOM) sector. By infiltrating ground station control networks, the actors gain the ability to mirror high-value traffic and potentially disrupt communications between island nations and their security partners. This aligns with Beijing's strategic interests in the South China Sea, where maritime domain awareness and secure communications are contested assets.
Technical Details
Analysis of the intrusion reveals the exploitation of a critical, previously undisclosed vulnerability in a widely deployed edge-facing VPN appliance used for remote management of satellite hardware. The initial entry vector involved a sophisticated heap overflow exploit that allowed for unauthenticated remote code execution.
Upon gaining access, the actors deployed a series of kernel-level implants designed to evade detection by endpoint detection and response (EDR) solutions. A key component of their toolkit is a refined version of BPFdoor, a Linux backdoor that utilizes Berkeley Packet Filter (BPF) functionality to monitor network traffic at the kernel level. This allows the malware to remain dormant until it receives a specific 'magic packet,' effectively bypassing standard firewall rules. Lateral movement was achieved through the abuse of valid administrative credentials harvested from the gateway’s memory, followed by the deployment of the CrossC2 framework to maintain a staging ground within the internal management subnet.
Attribution Assessment
Encrygma attributes this activity to Salt Typhoon based on several distinct indicators. The infrastructure used for command and control (C2) overlaps with known Salt Typhoon 'ORB' (Overlay Research Box) proxy networks. Furthermore, the use of customized DLL filters for credential interception and the specific targeting of CALEA-compliant (Communications Assistance for Law Enforcement Act) infrastructure reflect the group’s established tradecraft. The strategic focus on Indo-Pacific telecommunications correlates with prior campaigns documented by Mandiant and Microsoft MSTIC throughout 2024 and 2025.
Implications
The compromise of satellite ground stations and subsea cable systems poses a severe threat to regional security. The ability to intercept and decrypt high-level diplomatic and military communications provides the People's Republic of China (PRC) with a significant intelligence advantage. Moreover, the persistence mechanisms identified suggest that Salt Typhoon is prepared to remain embedded for years, providing a 'kill switch' capability that could be activated during a regional kinetic conflict to paralyze enemy command and control.
Recommendations
- Immediate Patching: All edge networking appliances, particularly those managing SATCOM and subsea cable systems, must be audited for recent firmware updates and signs of exploitation.
- Network Segmentation: Implement strict out-of-band (OOB) management for critical infrastructure, ensuring that control networks are physically or logically isolated from the general internet.
- Enhanced Monitoring: Deploy BPF-aware detection tools to identify unauthorized packet sniffing at the kernel level.
- Credential Rotation: Execute a mandatory rotation of all privileged administrative credentials across telecommunications management layers.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
China-Nexus APTs Deploy AI-Powered ARTEX Framework in Global Espionage Campaign
China-Nexus Storm-0940 Weaponizes Agentic AI to Automate Massive Supply Chain Compromise