criticalCritical Infrastructure
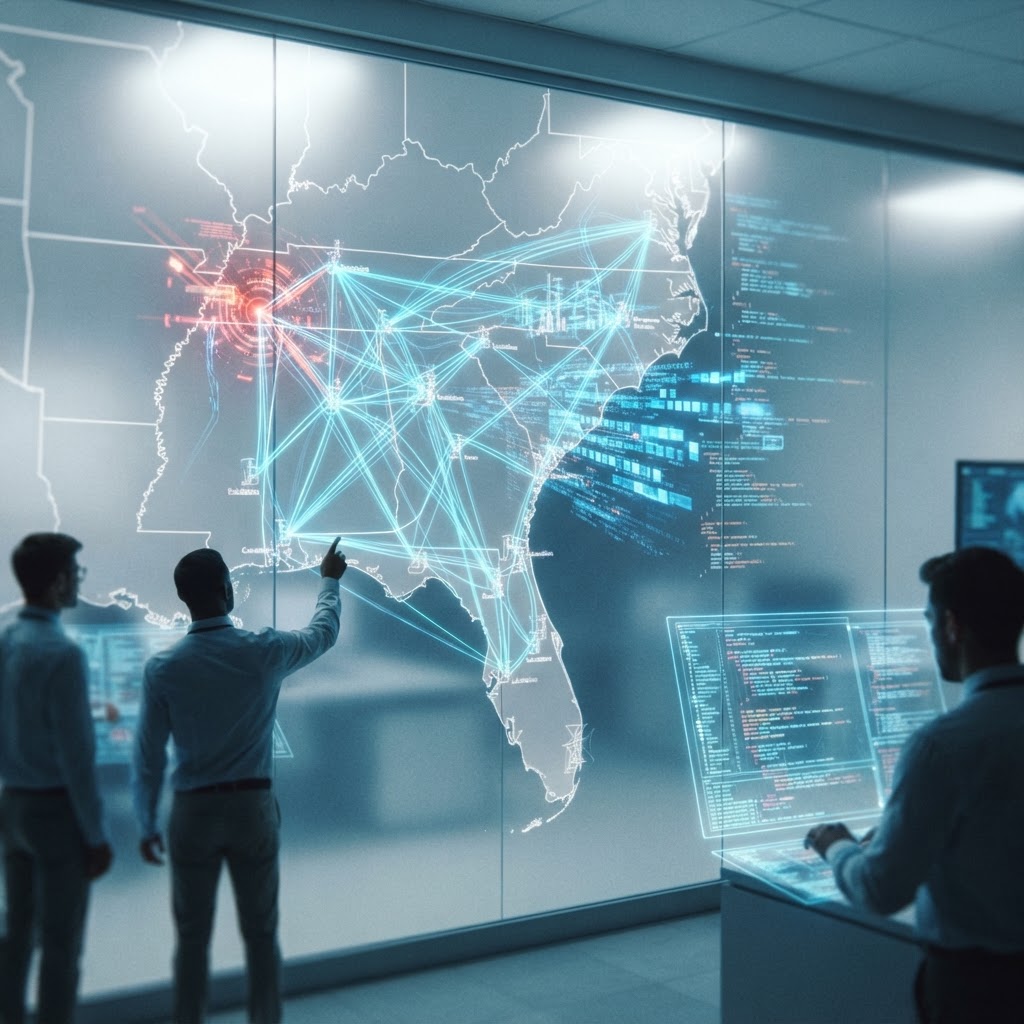
Russian APT44 Exploits SonicWall Zero-Days to Infiltrate US Southeast Power Grid Control Systems
A critical campaign attributed to the Russian Sandworm group has compromised edge infrastructure in regional US power utilities. Attackers are exploiting zero-day SSRF flaws to gain OT network access.
₿
Encrygma is selling the entire Full Cyber Weapon Research of Russian APT44 Exploits SonicWall Zero-Days to Infiltrate US Southeast Power Grid Control Systems for ₿ 0.10 BTC. Contact us.
22 July 2026Last updated 20 August 20265 min readMicrosoft MSTIC
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- North America
- Confidence:
- High Confidence
- CVE:
- CVE-2026-15409, CVE-2026-15410
- Source:
- Microsoft MSTIC
- Read Time:
- 5 min
Executive Summary Recent intelligence collected between July 20 and July 22, 2026, indicates a major cyber-offensive targeting the Southeastern United States power distribution network. This operation coincides with the July 2026 Cyber Shield exercise and follows the discovery of two critical zero-day vulnerabilities in SonicWall SMA 1000 series appliances. A high-confidence attribution by Microsoft MSTIC and CISA links this activity to the Russian state-sponsored group APT44, also known as Sandworm. The campaign marks a significant pivot from disruptive hacktivism to calculated, strategic pre-positioning within the Operational Technology (OT) layers of regional electric cooperatives. This activity represents the most significant threat to the domestic US grid since the discovery of the Volt Typhoon intrusions. ## Threat Analysis The threat landscape has evolved significantly in mid-2026, as evidenced by a 51 percent rise in high-severity vulnerabilities reported in the Forescout H1 Threat Review. Sandworm is leveraging this volatility by deploying specialized malware designed to interact with Industrial Control Systems (ICS). Unlike previous noisy attacks, this campaign focuses on stealthy persistence using 'Living-off-the-Land' (LotL) techniques. By hijacking internet-facing edge infrastructure, the actors avoid detection by traditional endpoint protection. The strategic intent appears to be the establishment of a 'kill switch' capability within the US domestic grid, providing Moscow with leverage during potential geopolitical escalations. The actors are specifically targeting smaller, less-resourced utilities that often lack robust secondary monitoring systems for their OT segments. ## Technical Details The primary entry vector involves the exploitation of CVE-2026-15409, a critical server-side request forgery (SSRF) vulnerability. This flaw allows the attacker to bypass authentication and query internal management services on the edge appliance. Incident responders have observed the actors chaining this with CVE-2026-15410, an OS command injection bug, to gain root-level access. Once the edge device is compromised, the actors deploy a custom modular backdoor capable of sending unauthorized Modbus TCP commands directly to Programmable Logic Controllers (PLCs). Researchers have identified lateral movement from the corporate IT environment into the SCADA VLAN via compromised administrative workstations that lacked hardware-based multi-factor authentication. Evidence also points to the use of 'HollowGraph' malware variants, which hide command-and-control traffic within legitimate cloud service events to evade traffic analysis. ## Attribution Assessment Attribution to APT44 is based on the use of unique command-and-control (C2) infrastructure previously associated with GRU Unit 74455. The activity also overlaps with the 'Cyber Army of Russia Reborn' persona, which recently posted redacted screenshots of HMI screens from a Florida-based utility on social media. The technical sophistication required to exploit the SMA 1000 zero-days and the focus on power-sector specific protocols like DNP3 and IEC 61850 further confirm a highly resourced nation-state actor. The timing of the campaign, mirroring recent escalations in Eastern Europe, aligns with known Russian GRU doctrine for out-of-area operations. ## Implications The successful infiltration of multiple regional utilities poses a critical risk to physical infrastructure. Unauthorized manipulation of load-shedding protocols could trigger cascading failures across the Eastern Interconnection. This campaign demonstrates that the vulnerability of the US power grid is no longer a theoretical risk but a present operational reality. The ability of a foreign adversary to maintain persistent access to the 'nervous system' of the grid compromises the stability of civilian life and national defense capabilities. If left unaddressed, these backdoors could be activated during a period of conflict to cause prolonged kinetic damage to substation equipment. ## Recommendations Encrygma recommends the following immediate actions: 1. Disconnect all internet-facing SonicWall SMA 1000 appliances until the July 2026 security updates are applied and verified. 2. Conduct an immediate forensic audit of all OT/IT gateway devices for unauthorized accounts or 'spinstall0.aspx' file modifications. 3. Enforce strict network segmentation, ensuring that OT control networks are isolated behind physical or robust logical air-gaps. 4. Implement continuous monitoring for anomalous Modbus or DNP3 traffic originating from non-engineering workstations. 5. Accelerate the transition to SNMPv3 and adopt a zero-trust architecture for all remote access into critical systems. 6. Participate in CISA’s ‘Shields Up’ initiative and report any anomalous edge device behavior to the FBI's Cyber Watch.

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Qilin Ransomware Surge Targets Industrial Sector as Global Critical Infrastructure Threats Escalate
01 Oct 2026
CISA Launches 'Securing the Next 250' Initiative Amidst Escalating Threats to Critical Infrastructure
05 Oct 2026
Industrial Sector Faces Record Ransomware Surge as Qilin Group Targets Critical Infrastructure
30 Sep 2026