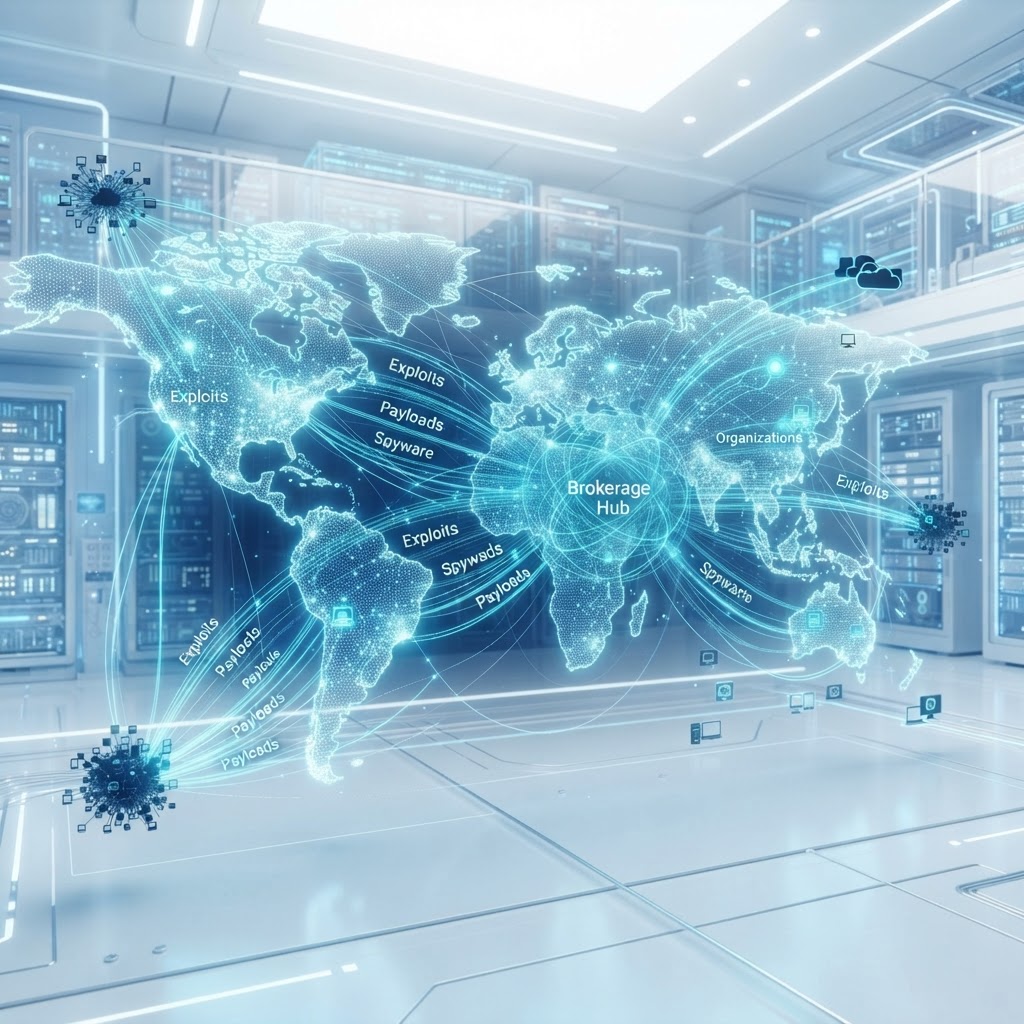
Rise of IRIS C2 Exploit Brokerage and Global Surge in Mercenary Spyware Exploitation
Emerging exploit broker IRIS C2 and a new wave of Apple threat notifications signal a volatile escalation in the commercial surveillance market targeting high-value mobile and cloud assets.
Encrygma is selling the entire Full Cyber Weapon Research of Rise of IRIS C2 Exploit Brokerage and Global Surge in Mercenary Spyware Exploitation for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Offensive Tools
- Severity:
- Critical
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- High Confidence
- CVE:
- CVE-2026-50656
- Source:
- Mandiant
- Read Time:
- 5 min
Executive Summary
Intelligence gathered between July 8 and July 10, 2026, highlights a critical escalation in the global commercial surveillance market. The emergence of IRIS C2, a Virginia-based exploit broker offering bounties as high as $7 million for zero-day vulnerabilities, signals a new, more aggressive phase in the offensive cyber tool trade. Concurrently, Apple has initiated a massive wave of "Mercenary Spyware" threat notifications to users in over 90 countries, including India and several EU member states. These developments suggest a high-tempo period of active exploitation targeting high-value individuals, including diplomats and members of the European Parliament, utilizing a mix of legacy kernel vulnerabilities and sophisticated zero-click mobile chains.
Threat Analysis
The current threat landscape is defined by the intersection of traditional mercenary spyware vendors and new, "boutique" exploit brokers. While legacy firms like NSO Group continue to dominate the market with Pegasus, the arrival of startups like IRIS C2 (operated under the Calvexa Group LLC umbrella) indicates a fragmented market where high-talent independent researchers are being lured by multi-million-dollar payouts. Encrygma’s analysis suggests these tools are being prioritized for political espionage rather than counter-terrorism. The recent targeting of former EU Parliament member Stelios Kouloglou during his tenure on the PEGA committee highlights that the investigators themselves remain the primary targets of the surveillance they seek to regulate. The market is currently shifting toward "platform-agnostic" tools that can bridge the gap between mobile surveillance and cloud-based persistence.
Technical Details
Two primary vectors have dominated intelligence reports in the last 48 hours. The first is a zero-click exploit chain targeting iOS 18+ and Android 16, which researchers have dubbed "AegisCore." This chain exploits a vulnerability in the handling of NSKeyedArchive within mobile messaging subsystems—specifically bypassing the MessagesBlastDoorService protections that were previously considered robust. This allows for total device takeover without any user interaction, including microphone activation and encrypted message exfiltration.
The second major development is the weaponization of "GhostLock," a 15-year-old use-after-free vulnerability in the Linux kernel’s futex locking code (CVE-2026-50656). While originally dismissed as a local privilege escalation (LPE), exploit brokers are now offering GhostLock as a critical component for container escapes in cloud-based surveillance environments. This allows an attacker who has gained a minimal foothold to escalate to full root access in seconds, enabling deep persistence on the back-end servers that manage a target’s communications and metadata. The exploit is particularly dangerous because it affects nearly all major Linux distributions released since 2011.
Attribution Assessment
Attribution for the recent global surge remains complex due to the use of obfuscated proxy networks like NetNut. However, the IRIS C2 platform has been linked to domestic U.S. operators with documented ties to fraudulent intelligence ventures and far-right conspiracy networks. The broader mercenary spyware campaign detected by Apple appears to be a multi-pronged effort. A significant portion of the traffic has been traced to infrastructure previously associated with Intellexa and Cytrox successors, now operating under new shell identities in Southeast Asia and the Middle East. The use of the "PWNYOURHOME" exploit indicates that despite public exposure, the underlying logic of HomeKit-based targeting remains viable for Mediterranean-based state actors.
Implications
The availability of $7 million payouts for full-chain exploits will likely drain talent from defensive research into the offensive sector, creating a "brain drain" that leaves standard OS protections lagging. Furthermore, the reliance on decades-old kernel flaws like GhostLock demonstrates a massive technical debt in secure systems that mercenary groups are now aggressively auditing. As technology companies move toward more neutral terminology—such as Apple’s shift from "state-sponsored" to "mercenary spyware"—the diplomatic cover for the nations purchasing these tools continues to grow, potentially leading to a decrease in public accountability for digital human rights abuses.
Recommendations
Encrygma recommends that organizations with high-value personnel implement the following immediately:
- Audit and patch all Linux-based server infrastructure against CVE-2026-50656 (GhostLock) regardless of the system's age.
- Enable "Lockdown Mode" on all mobile devices for high-risk users, as it significantly increases the cost of zero-click exploitation.
- Monitor mobile device logs for unexplained HomeKit service lookups or background data spikes in the MessagesBlastDoorService.
- Transition sensitive communications to hardware-encrypted platforms that do not rely on standard mobile messaging protocols or RCS.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Paragon Solutions Admits Inability to Detect Misuse of Graphite Spyware Following Contract Terminations

Global Surge in Mercenary Spyware: Apple Issues High-Confidence Alerts Across 110 Nations
