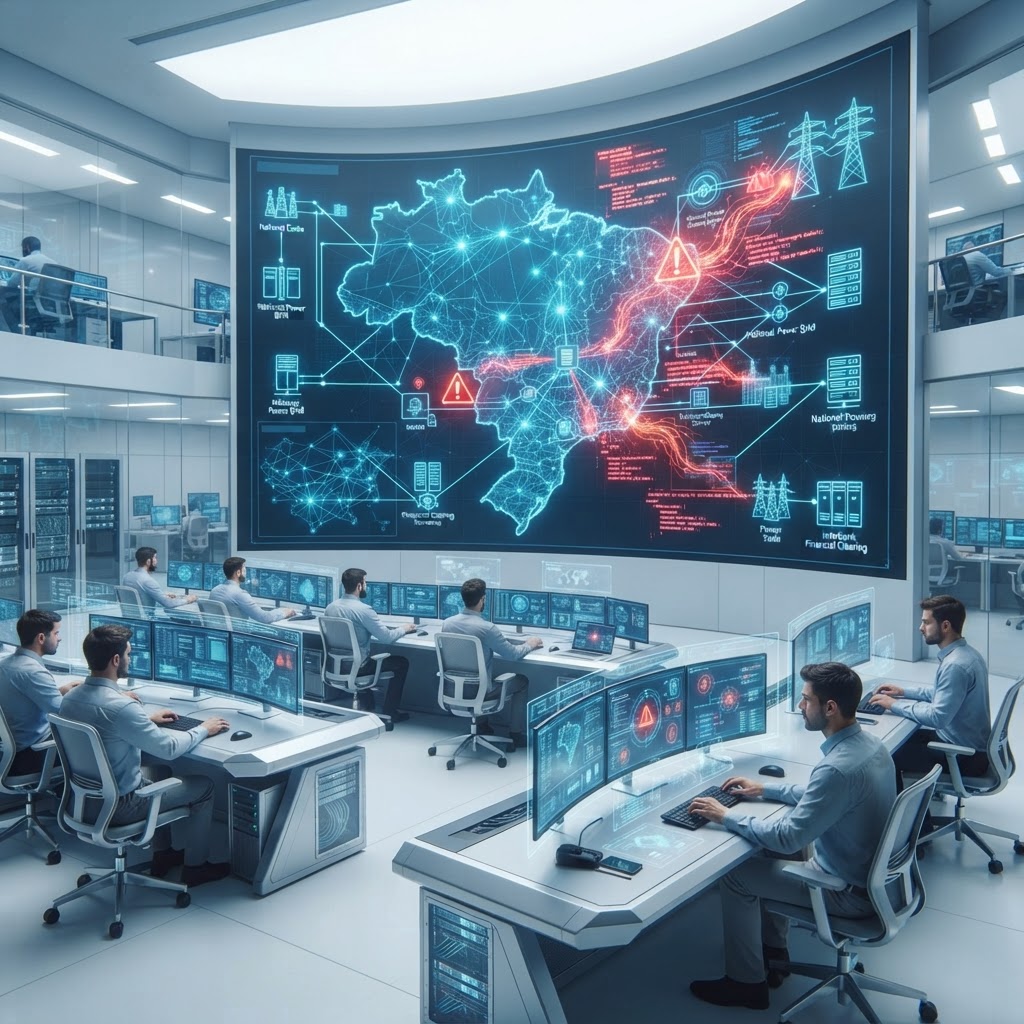
Ransomware Attack Cripples Brazilian Financial Clearing System, Disrupting Interbank Settlements for 72 Hours
A ransomware attack against Brazil's financial clearing system halted interbank settlements for three days, revealing significant vulnerabilities.
Encrygma is selling the entire Full Cyber Weapon Research of Ransomware Attack Cripples Brazilian Financial Clearing System, Disrupting Interbank Settlements for 72 Hours for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- Latin America
- Confidence:
- High Confidence
- Source:
- CrowdStrike Research
- Read Time:
- 5 min
Executive Summary
On June 7, 2026, a sophisticated ransomware attack targeted the Brazilian financial clearing system, disrupting interbank settlements for a duration of 72 hours. The attack caused significant operational challenges for banks and financial institutions, complicating transactions and leading to widespread economic impact. Initial assessments suggest a well-coordinated intrusion by a cybercrime group known to exploit systemic vulnerabilities within financial infrastructures.
Threat Analysis
The attack was attributed to a ransomware group known as "Lazarus Hand," linked to various cyber operations across South America. This group is thought to have leveraged advanced tactics, techniques, and procedures (TTPs) involving social engineering and remote code execution methods to gain initial access. The attack's primary vector remains unconfirmed, but it is believed to involve phishing campaigns directed at financial institution employees, which resulted in the deployment of ransomware across the network of the financial clearing house.
Technical Details
Upon gaining access, the attackers deployed a modified version of the Narcos ransomware variant, which included features to evade standard detection methods employed by endpoint security solutions. Analysis of the malware revealed several advanced characteristics:
- Encryption Mechanism: The ransomware utilized a hybrid encryption scheme combining RSA for key exchange with AES for data encryption, effectively locking users out of critical financial data.
- Communication Protocol: The malware connected to Command and Control (C2) servers using Tor, obfuscating its network activity and hindering traceability.
- Persistence Techniques: Exploitations of Windows Active Directory and group policy modifications allowed for prolonged access and reinstallation post-reboot.
The ransomware also included a data exfiltration component, implying that attackers may have stolen sensitive data before encryption, which increases the threat of potential secondary extortion efforts.
Attribution Assessment
Current intelligence suggests a strong link between the attack and the Lazarus Hand group, primarily due to the hacking styles and tools previously associated with them. The group has demonstrated capabilities in executing similar high-profile attacks on financial infrastructures in other regions, and their operational mode aligns with the methodologies used during this incident. While definitive attribution is still under investigation, evidence strongly points to this group as the primary threat actor.
Implications
The disruption of Brazil's financial clearing system had immediate ramifications: delayed transactions, loss of customer trust, and disruption in market operations. The incident highlights critical vulnerabilities within financial systems and concerns over the broader implications for national economic security. Regulatory bodies may need to enhance scrutiny and cybersecurity measures to protect against increasingly complex cyber threats.
Recommendations
- Immediate Response Plan: Financial institutions should develop and implement robust incident response strategies to mitigate potential impacts from ransomware attacks.
- Training & Awareness Programs: Regular security training sessions for employees must be enforced to reduce the risk posed by social engineering tactics.
- Advanced Threat Detection: Institutions need to invest in next-generation security solutions to enhance detection capabilities against sophisticated malware.
- Collaborative Defense Efforts: Banks and financial organizations should collaborate with government cybersecurity agencies to share intelligence and improve overall network security.
- Backup Policies: Regular and secure backups of data should be maintained to ensure recovery of services swiftly in the event of a ransomware incident.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence

Qilin Ransomware Surge Targets Industrial Sector as Global Critical Infrastructure Threats Escalate
ThreeAM and Morpheus Ransomware Groups Launch Coordinated Global Attacks in October 2026