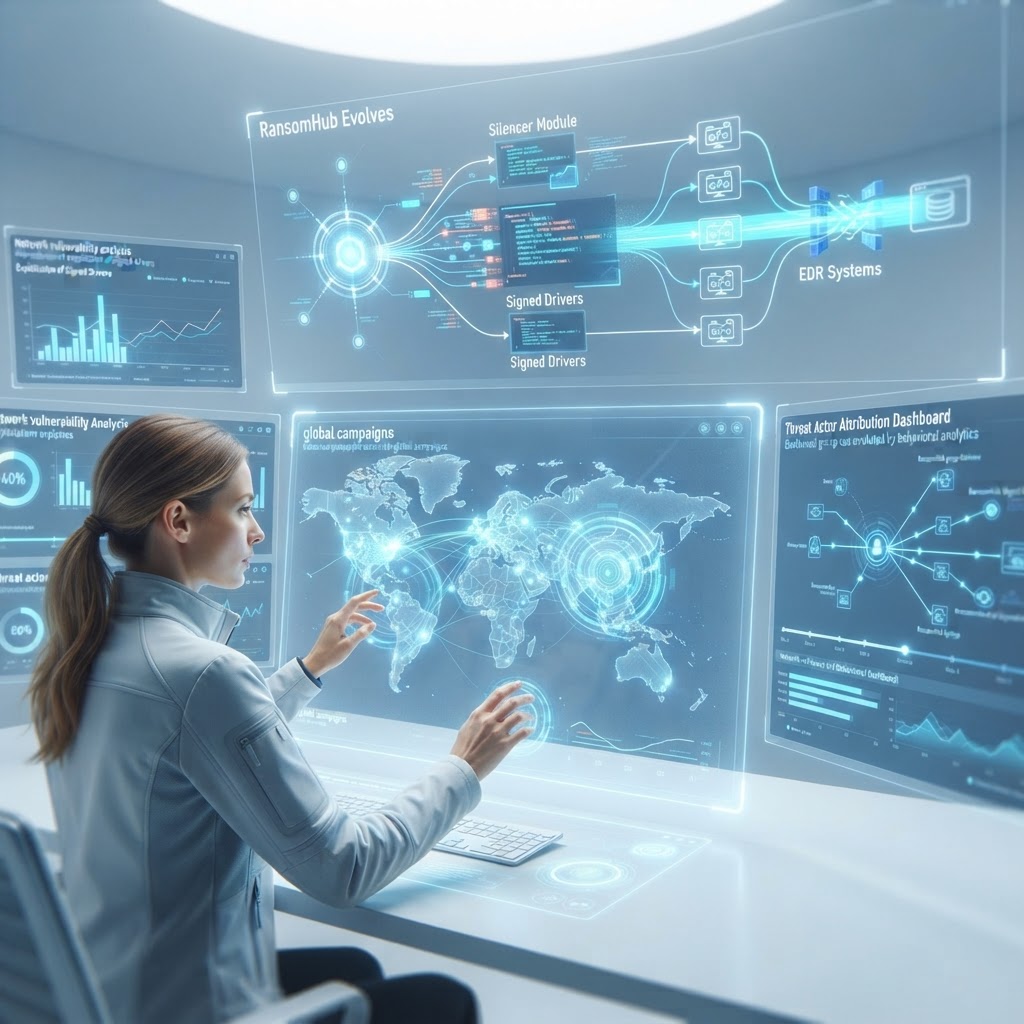
RansomHub Evolves: New 'Silencer' Module Exploits Signed Drivers to Neutralize EDR in Global Campaigns
RansomHub has deployed 'Silencer', a new module utilizing signed vulnerable drivers to terminate security processes, representing a significant technical shift in ransomware evasion tactics.
Encrygma is selling the entire Full Cyber Weapon Research of RansomHub Evolves: New 'Silencer' Module Exploits Signed Drivers to Neutralize EDR in Global Campaigns for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- Global
- Confidence:
- High Confidence
- Source:
- SentinelLabs
- Read Time:
- 5 min
Executive Summary
Over the past 48 hours, Encrygma intelligence has monitored a significant evolution in the tactics employed by the RansomHub ransomware-as-a-service (RaaS) collective. A new specialized evasion component, designated as 'Silencer' by our analysts, has been integrated into their deployment workflow. This module facilitates the mass termination of Endpoint Detection and Response (EDR) agents and antivirus software by leveraging known-vulnerable but legitimately signed kernel-mode drivers. This escalation has been observed in recent intrusions targeting critical infrastructure providers in North America and healthcare networks across Europe, indicating a coordinated effort to increase successful encryption rates by blinding security teams before the final payload delivery.
Threat Analysis
RansomHub has quickly filled the vacuum left by the disruption of major entities like ALPHV and LockBit. The group's latest campaign demonstrates a move toward highly technical evasion rather than relying solely on credential theft. The 'Silencer' module represents a sophisticated 'Bring Your Own Vulnerable Driver' (BYOVD) threat. The primary infection vector identified in the last 24 hours involves the exploitation of a newly discovered bypass in legacy VPN concentrators, followed by immediate lateral movement using legitimate administrative tools. By disabling security protections early in the kill chain, the actors significantly reduce the 'Time to Detect' (TTD), allowing them to exfiltrate massive volumes of data—often exceeding 500GB per victim—without triggering automated block actions.
Technical Details
The 'Silencer' module is a C++ compiled binary designed to operate with minimal dependencies. Upon execution, it performs a reconnaissance of the host system to identify active security processes from a hardcoded list of 140 unique strings corresponding to global security vendors. The tool then drops a vulnerable, signed driver—identified in recent samples as an outdated version of a motherboard utility driver—into the Windows drivers directory. By using the Windows Service Control Manager to load this driver, the malware gains kernel-mode execution privileges. It then issues specific IOCTL (Input/Output Control) commands to the driver to terminate protected security processes from the kernel level. Because these actions originate from a trusted, signed driver, they often bypass user-mode protection hooks and even some kernel-level protections that do not strictly enforce driver blocklisting. Once the 'Silencer' module confirms the termination of the security stack, the primary RansomHub locker is executed. This locker utilizes a hybrid ChaCha20-RSA encryption scheme and incorporates intermittent encryption, targeting only specific blocks of files to maximize speed while further evading heuristic detection mechanisms.
Attribution Assessment
Attribution for these latest developments points with high confidence to the RansomHub affiliate core. Code analysis of the 'Silencer' module reveals significant overlapping logic with the 'Knight' ransomware, which was recently offered for sale on underground forums. Furthermore, the communication infrastructure used for command and control (C2) in this campaign aligns with previous RansomHub operations, utilizing a mesh of compromised legitimate servers. The linguistic patterns observed in negotiations and the specific exclusion of targets within the Commonwealth of Independent States (CIS) strongly suggest a Russian-speaking threat actor base.
Implications
The emergence of the 'Silencer' tool signals a growing arms race between RaaS developers and security vendors. The shift to kernel-level interference via BYOVD means that standard user-mode EDR protections are no longer a sufficient deterrent. Organizations must now account for the possibility that their primary visibility tools could be neutralized early in an attack. This development likely presages a broader trend where ransomware groups invest more heavily in rootkit-like capabilities to ensure persistence and operational success in hardened environments.
Recommendations
Encrygma recommends that all organizations immediately review their driver loading policies. Key defensive measures include: 1. Implementing the Microsoft Vulnerable Driver Blocklist through Windows Defender Application Control (WDAC). 2. Enabling Hypervisor-protected Code Integrity (HVCI) to prevent the execution of malicious code in the kernel. 3. Configuring EDR alerts to trigger on the loading of 'unsigned' or 'third-party' drivers that are not part of the standard corporate image. 4. Conducting a full audit of external-facing assets for unpatched vulnerabilities in VPN and RDP services. 5. Transitioning to a Zero Trust architecture that does not rely solely on endpoint health for access decisions.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Encrygma Alert: Threat Actor 'k0t' Exfiltrates 70,000+ Credentials via Industrialized Edge Exploitation
Global Ransomware Surge: Qilin and Whitearmor Lead October 2026 Wave of Extortion Attacks