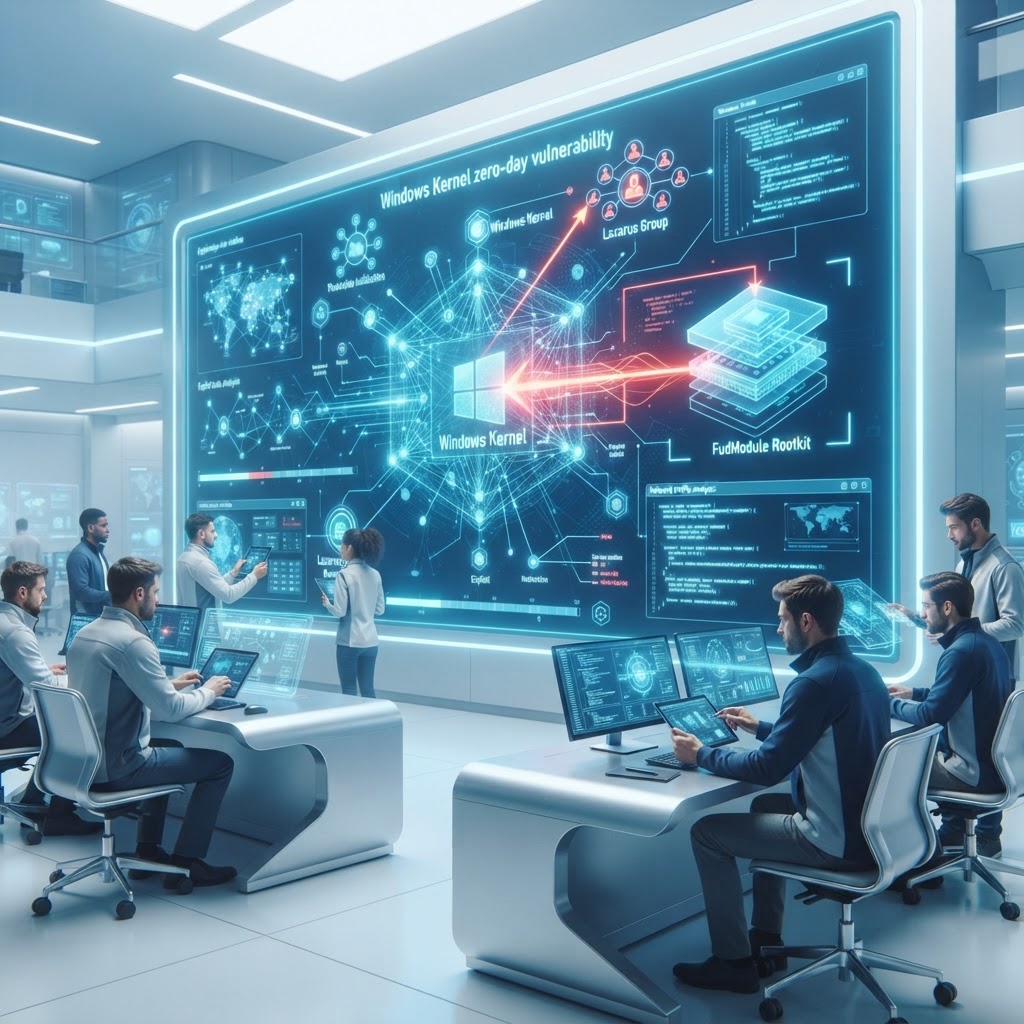
Lazarus Group Leverages Windows Kernel Zero-Day CVE-2026-68820 to Deploy Enhanced FudModule Rootkit
North Korean APT Lazarus has been observed exploiting a use-after-free vulnerability in the Windows AFD.sys driver to gain SYSTEM privileges. The campaign targets global defense and aerospace sectors to deploy a sophisticated kernel-mode rootkit.
Executive Takeaway — TL;DR
- Category:
- Zero-Day Exploits
- Severity:
- Critical
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- High Confidence
- CVE:
- CVE-2026-68820
- Source:
- Check Point Research
- Read Time:
- 5 min
Executive Summary
Recent intelligence confirms that the North Korean state-sponsored threat actor known as Lazarus Group (APT38) has successfully integrated a zero-day exploit for CVE-2026-68820 into its latest espionage campaign. This vulnerability, a use-after-free flaw in the Windows Ancillary Function Driver for WinSock (AFD.sys), allows for local elevation of privilege to SYSTEM level. The campaign, tracked as a new variant of 'Operation Dream Job,' specifically targets employees within the defense, aerospace, and aviation sectors in Europe and India. By leveraging this zero-day, Lazarus has been able to deploy an updated version of their FudModule rootkit, significantly enhancing their ability to evade modern endpoint detection and response (EDR) solutions.
Threat Analysis
The exploitation of CVE-2026-68820 represents a strategic shift in Lazarus's tactics, focusing on the latest iterations of the Windows operating system. Unlike previous campaigns that targeted older kernel vulnerabilities, this exploit specifically supports Windows 11 builds 26100 and 26200. The attack chain typically begins with social engineering, where fraudulent recruitment offers are sent to high-value targets via professional networking platforms. Once the victim executes a malicious payload disguised as a job description or application, the exploit triggers the AFD.sys vulnerability to bypass the Windows security model and establish a persistent, high-privilege foothold in the kernel.
Technical Details
CVE-2026-68820 is a use-after-free (UAF) vulnerability residing in the afd.sys driver, which serves as the entry point for the Windows Sockets (Winsock) API. The vulnerability occurs when the driver fails to properly manage memory objects during specific socket IOCTL operations. By carefully grooming the kernel pool, Lazarus attackers can trigger a condition where a previously freed memory object is reused, allowing them to overwrite kernel function pointers.
This primitive is then used to load the FudModule rootkit. The latest version of FudModule discovered in this campaign features advanced capabilities, including the ability to disable EDR telemetry by tampering with kernel callbacks and Direct Kernel Object Manipulation (DKOM). Furthermore, researchers have identified new functionality designed to bypass Windows Smart App Control, effectively neutralizing one of the OS's primary defenses against untrusted applications.
Attribution Assessment
Attribution to the Lazarus Group is made with high confidence based on significant overlaps in infrastructure, code similarities in the FudModule rootkit, and the continuation of the 'Operation Dream Job' targeting patterns. The use of specific command-and-control (C2) protocols and the focus on strategic sectors align with previous North Korean state-sponsored activities aimed at intellectual property theft and technological espionage.
Implications
The successful exploitation of a kernel-level zero-day in Windows 11 demonstrates the high level of technical sophistication maintained by North Korean APTs. The ability to deploy a rootkit that can actively disable security software poses a severe risk to the integrity of defense supply chains. Organizations targeted in this campaign face not only the loss of sensitive data but also the long-term presence of a stealthy actor capable of monitoring all system activity at the most privileged level.
Recommendations
Encrygma recommends that all organizations immediately apply the Microsoft August 2026 security updates to mitigate CVE-2026-68820. Additionally, security teams should monitor for unauthorized loading of kernel drivers and unusual IOCTL calls to afd.sys. Hardening EDR configurations to protect against kernel callback tampering and implementing strict application whitelisting can provide additional layers of defense against the FudModule rootkit.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
ShinyHunters Bypass WAF Protections to Resume Exploitation of Oracle PeopleSoft Zero-Day
Critical Zero-Day Vulnerability CVE-2026-93616 Exploited in Check Point Security Management Infrastructure