Lazarus Group Escalates Cryptocurrency Heists: Over $200M Stolen from DeFi Protocols in Q2 2026
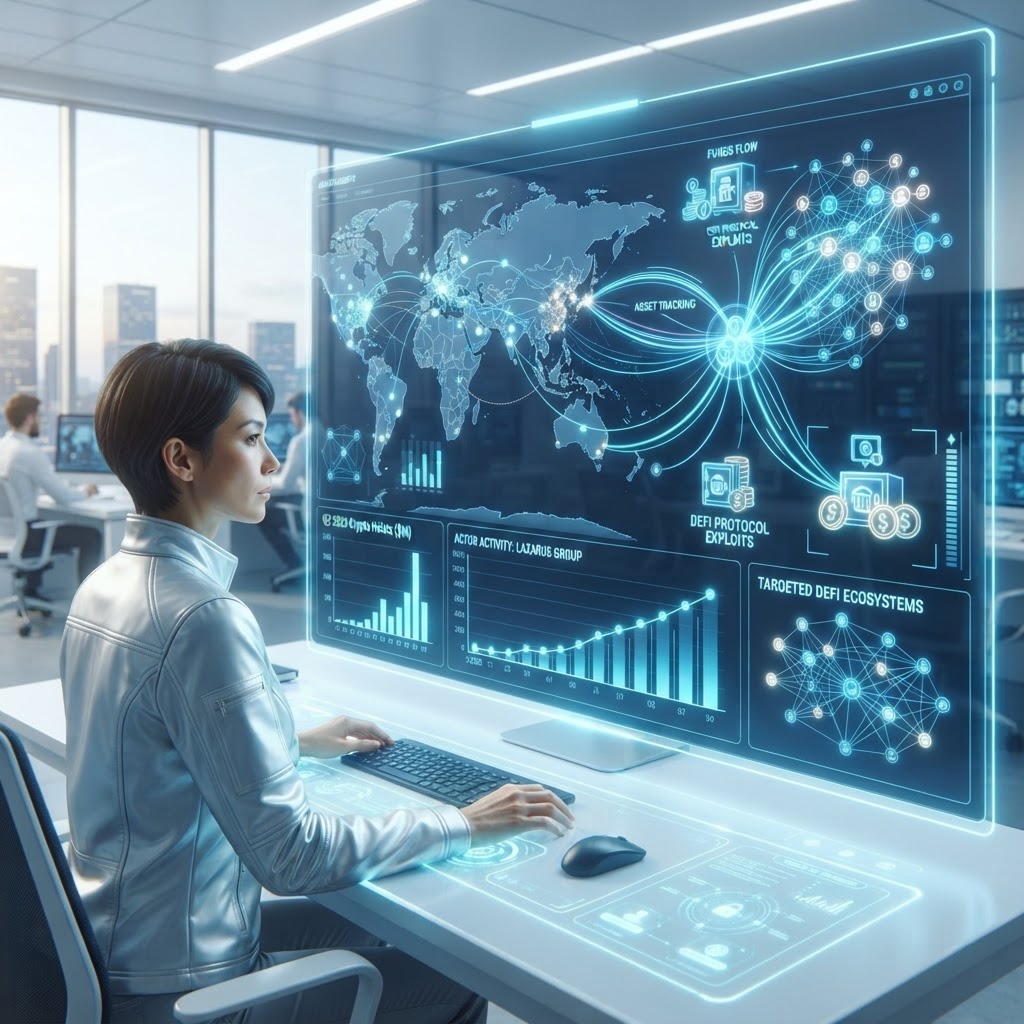
This quarter, the Lazarus Group has significantly ramped up its cryptocurrency theft operations, targeting decentralized finance (DeFi) protocols and amassing over $200M.
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- High
- Actor Type:
- APT
- Geography:
- Southeast Asia
- Confidence:
- High Confidence
- Source:
- Mandiant Threat Intelligence
- Read Time:
- 6 min
Executive Summary
In Q2 of 2026, the North Korean cybercrime unit known as the Lazarus Group has expanded its operations into the cryptocurrency sector, specifically targeting decentralized finance (DeFi) protocols. The group has successfully orchestrated a series of sophisticated thefts, resulting in the theft of over $200 million across various platforms. This trend highlights the group's evolving strategies and emphasizes the need for enhanced security measures within the DeFi ecosystem.
Threat Analysis
The Lazarus Group, linked to the Reconnaissance General Bureau of North Korea, has continuously adapted its cyber strategies. Recent intelligence indicates a noticeable pivot towards DeFi protocols, capitalizing on the vulnerabilities inherent in these decentralized systems. Their recent operations have targeted platforms characterized by poorly vetted smart contracts and insufficient security protocols, allowing for the rapid extraction of significant sums of cryptocurrency.
The group has employed a variety of tactics including sophisticated phishing schemes, exploiting smart contract vulnerabilities, and utilizing advanced malware to gain unauthorized access to users' funds. Notable incidents include attacks on prominent DeFi platforms which saw funds siphoned almost instantaneously after vulnerabilities were detected.
Technical Details
Analysis of the group's modus operandi reveals a multifaceted approach:
- Phishing Attacks: The Lazarus Group is utilizing tailored phishing emails and fake websites to lure investors into revealing their private keys or seed phrases.
- Smart Contract Exploits: By exploiting weaknesses in smart contracts, such as reentrancy attacks or integer overflow faults, the group has been able to manipulate existing protocols to issue unauthorized tokens.
- Cross-Chain Exploits: They are also leveraging cross-chain decentralized exchanges (DEX) to obscure the origins of stolen funds, making tracking significantly more challenging for authorities.
- Malware Deployment: Further analysis reveals the use of malware disguised as legitimate DeFi tools, which when installed, grant attackers control over users’ wallets.
Attribution Assessment
Attribution to the Lazarus Group stems from comprehensive digital forensics and correlation with previously known signatures of their attacks. Indicators of compromise collected from various affected platforms showed links to previously analyzed malware strains associated with the group, such as “Maldoc” and “DTrack.”
Additionally, reconnaissance conducted on network traffic patterns and behaviors exhibited strong alignments with past Lazarus operations, providing high confidence in this attribution.
Implications
As the Lazarus Group continues to enhance its strategic pivot into the DeFi space, the implications for global cybersecurity are profound. The group's financial gains not only fund illicit state activities but also pose a threat to user trust in decentralized financial ecosystems. This operational expansion could lead to increased regulatory scrutiny of DeFi platforms, potentially stifling innovation in the sector.
Recommendations
- Enhanced Security Protocols: DeFi platforms must adopt robust security measures, including regular audits of smart contracts and implementing advanced user authentication methods.
- User Education: Increased efforts in educating users about phishing schemes and the importance of secure wallet management are critical.
- Collaboration with Law Enforcement: DeFi platforms should work closely with law enforcement agencies to share incident data and enhance detection capabilities against such threats.
- Investment in Cyber Threat Intelligence: Ongoing investment in threat intelligence capabilities will be essential in proactively identifying and mitigating emerging threats from groups like Lazarus.
By addressing these vulnerabilities and enhancing security measures, the DeFi ecosystem can better protect itself against the sophisticated tactics employed by cyber adversaries such as the Lazarus Group.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.