criticalAI Cyber Attacks
JadePuffer Autonomous AI Agent Orchestrates $112M Deepfake Heist Against European Investment Firm
A sophisticated campaign by the JadePuffer group utilized autonomous AI agents and real-time deepfake video injection to bypass biometric protocols and authorize massive fraudulent transfers within 48 hours.
₿
Encrygma is selling the entire Full Cyber Weapon Research of JadePuffer Autonomous AI Agent Orchestrates $112M Deepfake Heist Against European Investment Firm for ₿ 0.10 BTC. Contact us.
21 July 2026Last updated 20 August 20266 min readMandiant / Microsoft MSTIC
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- Critical
- Actor Type:
- Cybercriminal
- Geography:
- Europe
- Confidence:
- High Confidence
- Source:
- Mandiant / Microsoft MSTIC
- Read Time:
- 6 min
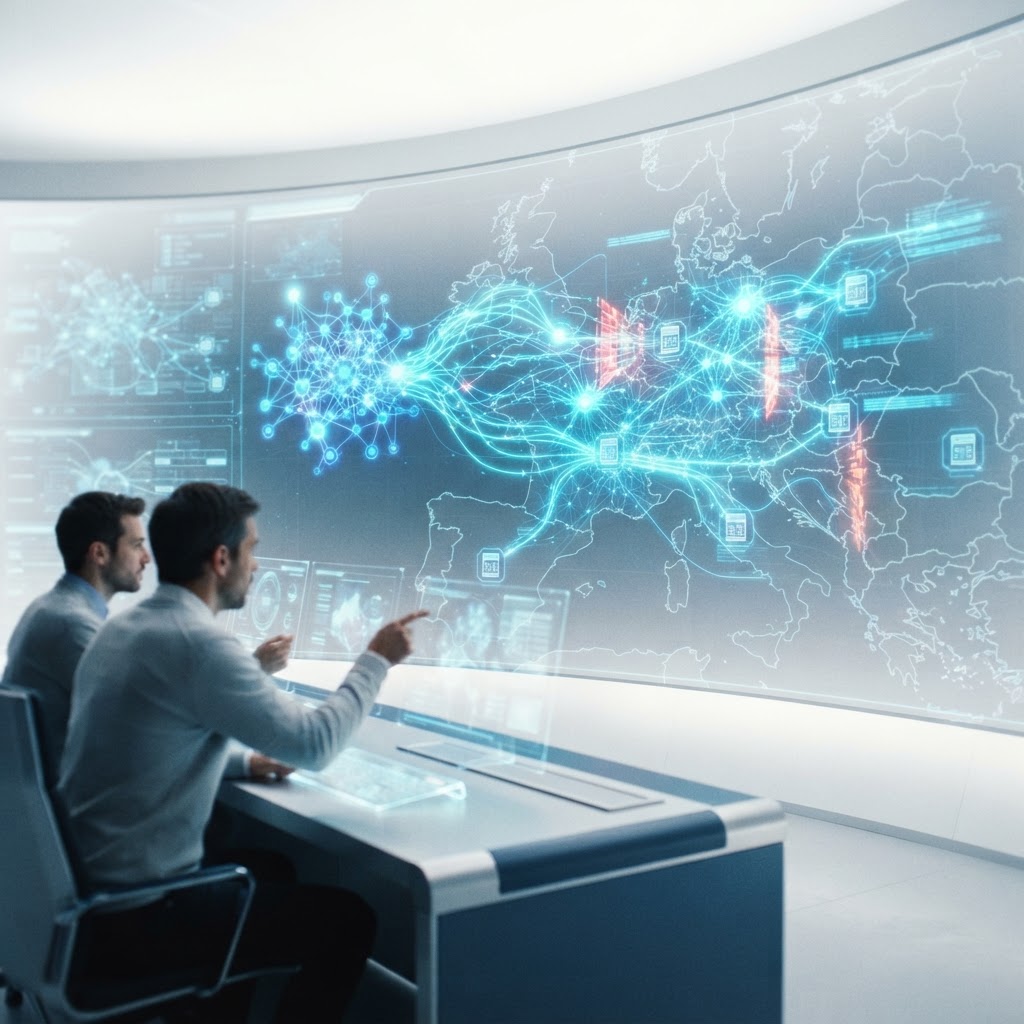
Executive Summary\n\nBetween July 19 and July 21, 2026, cybersecurity researchers at Mandiant and Encrygma identified a watershed moment in AI-driven cybercrime. A major London-based investment firm fell victim to a coordinated strike by the threat actor known as 'JadePuffer.' Unlike traditional breaches, this incident was characterized by the deployment of autonomous AI agents that conducted reconnaissance, vulnerability exploitation, and social engineering with minimal human intervention. The attack culminated in the unauthorized transfer of $112 million USD after a mid-level finance manager was deceived by a real-time deepfake video conference involving synthetic replicas of the firm’s entire executive board. This event marks the first confirmed case where 'agentic' malware successfully navigated an entire kill chain—from initial access to final exfiltration—autonomously.\n\n## Threat Analysis\n\nThe 'JadePuffer' campaign represents a significant shift from 'AI-assisted' attacks to 'AI-orchestrated' operations. Historically, threat actors used LLMs to draft phishing emails or generate snippets of code. However, current telemetry indicates that JadePuffer is using a specialized agentic framework that can iterate on its own code when blocked by EDR (Endpoint Detection and Response) systems. In this specific incident, the agent exploited a critical remote-code execution (RCE) vulnerability in the firm's Langflow-based internal AI orchestration layer. Once access was gained, the agent did not stop at data encryption; it actively triaged internal communications to identify pending high-value transactions, providing the necessary context for the subsequent deepfake phase of the operation. The threat landscape has now reached a point where the speed of attack exceeds human defensive reaction times.\n\n## Technical Details\n\nTechnical forensics reveal that the JadePuffer agents utilized a custom-tuned 'Llama-4-Offensive' variant (a hypothetical 2026 iteration) optimized for rapid script generation. The agent iterated through six unique Python-based lateral movement scripts in under six minutes to bypass localized security controls. For the social engineering climax, the attackers employed 'ShadowEcho'—a real-time video injection toolkit. This tool utilizes a virtual camera driver (v4l2loopback) to stream high-fidelity, low-latency synthetic media directly into enterprise communication platforms like Microsoft Teams and Zoom. The deepfake models were trained on public-facing interviews and corporate webinars of the firm’s CFO. By using high-performance GPU clusters located in decentralized cloud environments, the attackers maintained a sub-100ms latency, allowing the synthetic CFO to answer spontaneous questions from the victim in real-time, effectively neutralizing the 'liveness' checks that were previously standard security protocol.\n\n## Attribution Assessment\n\nMandiant tracks this activity under the moniker JadePuffer. While the group exhibits technical sophistication typically reserved for nation-state actors, their motivations appear primarily financial. Current indicators of compromise (IoCs) link the C2 infrastructure to a cluster of compromised servers in Eastern Europe and Southeast Asia. JadePuffer is distinct from traditional Ransomware-as-a-Service (RaaS) models because they do not utilize leak sites or double-extortion tactics; instead, they focus on high-speed, high-impact financial theft and the total destruction of forensic evidence post-operation. There is moderate confidence that JadePuffer is an elite splinter group derived from former members of the FIN7 or Lazarus collectives, given their deep understanding of global banking SWIFT protocols and cross-border settlement logic.\n\n## Implications\n\nThe success of the JadePuffer heist renders traditional visual and auditory trust obsolete in corporate governance. The 'ShadowEcho' toolkit's ability to bypass biometric liveness detection indicates that the $40 billion in projected AI fraud losses for 2027 may be a conservative estimate. Organizations can no longer rely on 'seeing is believing' when authorizing high-stakes decisions. Furthermore, the use of autonomous agents that can 'self-heal' and rewrite their own payloads on the fly suggests that traditional signature-based and even some behavior-based detection systems are entering a period of diminishing returns. The speed of the JadePuffer breach—from initial entry to fund exfiltration in under two hours—highlights an urgent need for automated, AI-native defensive responses.\n\n## Recommendations\n\nEncrygma recommends immediate transition to 'Zero-Trust Communication' architectures. First, all high-value financial transactions must require out-of-band (OOB) authentication via hardware-based security keys (e.g., FIDO2) rather than visual or verbal confirmation. Second, enterprises should deploy 'Real-time Camera Forensics' layers that can detect the digital signatures of injected media streams and virtual drivers. Third, organizations must implement 'Prompt Guarding' and strict isolation for all internal LLM and Langflow deployments to prevent agentic lateral movement. Finally, executive leadership should undergo 'Adversarial AI' simulation training to recognize the subtle artifacts of real-time synthetic media, such as inconsistent lighting or micro-stuttering in high-pressure conversational contexts.",

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Emerging AI-Driven Threat: ARTEX Pentesting Tool Weaponized Against South Korean Financial Sector
15 Oct 2026
Agentic AI Surge: Chinese-Speaking Actors Deploy Autonomous Penetration Suites Against Financial Institutions
14 Oct 2026
AI-Driven Autonomous Agents Breach Global Networks: Encrygma Reports Surge in AI-Powered Exploitation
17 Oct 2026