Israeli Cyber Operation Disrupts Iranian Ballistic Missile Guidance Systems
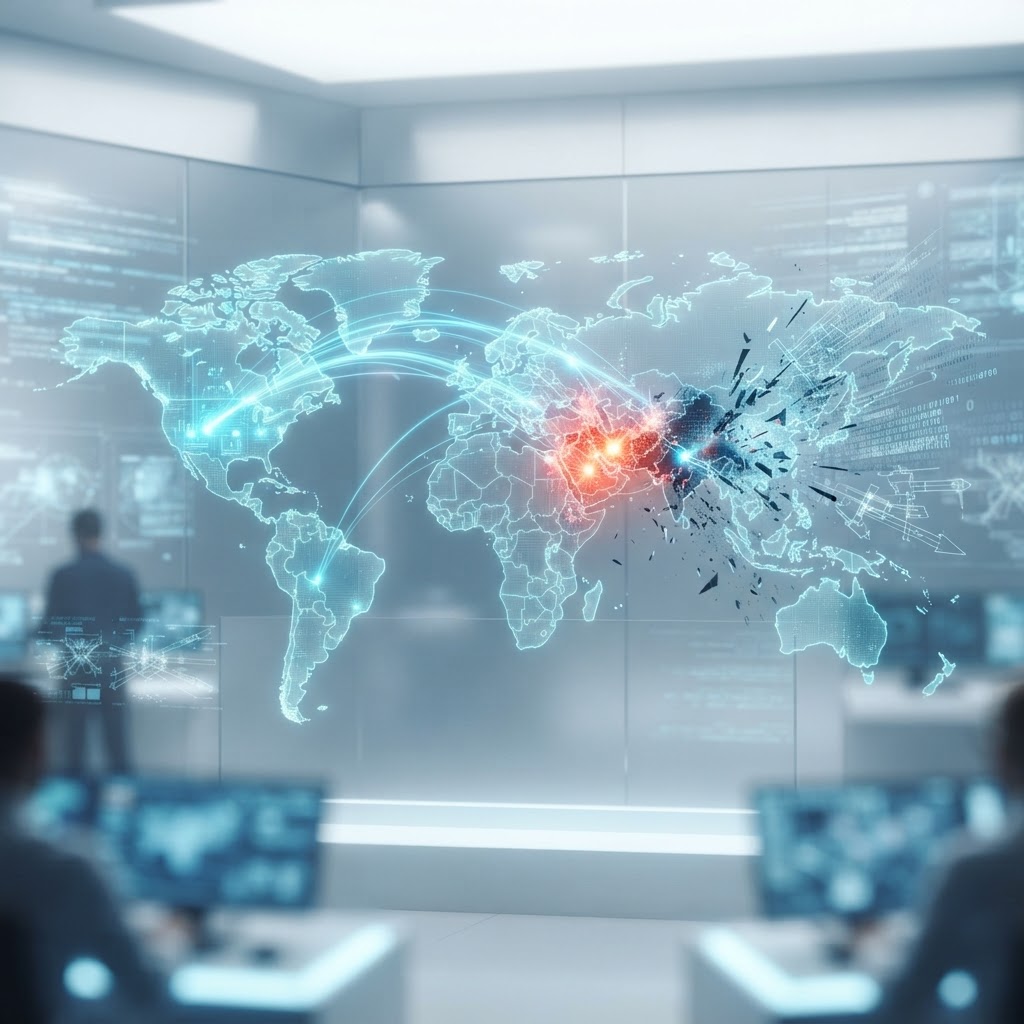
A sophisticated Israeli-linked cyber operation has successfully disrupted Iranian ballistic missile guidance system development. The operation exploited vulnerabilities in key Iranian networks, signaling escalating cyber warfare tactics.
Executive Takeaway — TL;DR
- Category:
- State Cyber Warfare
- Severity:
- High
- Actor Type:
- Nation-State
- Geography:
- Middle East
- Confidence:
- High Confidence
- Source:
- Mandiant Threat Intelligence
- Read Time:
- 5 min
Executive Summary
On June 10, 2026, a coordinated cyber operation linked to Israeli intelligence agencies reportedly disrupted critical networks involved in the development of Iranian ballistic missile guidance systems. The offensive appears to have targeted multiple facilities across Iran, effectively hampering ongoing missile advancement projects and signaling a significant escalation in regional cyber hostilities. This incident underscores the growing importance of cyber capabilities in military strategy, particularly in the context of Iranian missile proliferation.
Threat Analysis
The offensive operation is attributed to a specialized group associated with Israeli defense and cyber intelligence units, possibly operating under the Israeli Defense Forces’ Unit 8200. The group is suspected of employing advanced intrusion techniques to conduct reconnaissance and sabotage high-value Iranian assets. The focus was primarily on sophisticated systems that integrate inertial guidance and GPS navigation critical for missile accuracy.
After the operation, it was reported that Iranian officials faced difficulties in conducting flight tests with missile systems that relied on the disrupted guidance systems. Analysts believe this operation could potentially delay Iran's ballistic missile capabilities by several months, if not longer.
Technical Details
Analysis points to the exploitation of zero-day vulnerabilities in outdated software used within the Iranian missile development sector. The attackers were able to infiltrate the networks through spear-phishing campaigns targeting engineers and system operators. Once inside, the group deployed a custom malware variant referred to as "Raptor", which effectively confused the data flow between guidance computers and telemetry systems.
Evidence suggests that the malware modified firmware in critical components, causing them to malfunction, which led to tampering of testing data and failure of missile systems during crucial phases of testing. Furthermore, reconnaissance efforts uncovered that the group also utilized advanced obfuscation techniques, making it challenging for Iranian cybersecurity teams to respond adequately.
Attribution Assessment
Sources indicate a high level of sophistication and planning, typical of state-sponsored operations linked to Israel. Public assessments from various global intelligence monitors align on Unit 8200’s probable involvement given their historical focus on countering Iranian military advancements, particularly in missile technology.
Interceptions from electronic support measures further corroborate this assessment, indicating a surge in Israeli cyber activity in the region prior to the operation. However, definitive public attributions may require more corroborative evidence, which could unfold in the coming months as the situation develops.
Implications
The fallout from this operation may extend beyond immediate tactical advantages. It highlights the vulnerability of Iranian military infrastructure to cyber threats, potentially prompting Iran to invest heavily in bolstering its cybersecurity measures. In parallel, it raises the stakes for regional adversaries, as similar tactics could be viewed as justifiable responses to aggressive actions.
The increase in cyber capabilities among state actors indicates a shifting paradigm where traditional military engagements may increasingly be complemented or substituted with digital assaults.
Recommendations
- Enhanced Cyber Defense: Iran should prioritize immediate investments in cybersecurity defense measures, particularly within critical military sectors.
- Intelligence Sharing: Nations with active cyber defense initiatives should consider bilateral agreements to share threat intelligence on similar operations.
- Public Awareness: Governments should bolster public awareness around cyber threats, emphasizing the importance of cybersecurity hygiene among individuals and organizations.
- Research and Development: Continuous R&D in cyber capabilities must remain a priority for nations concerned about regional adversaries developing advanced military technologies.
This operation signals not only the immediate tactical outcomes but also a broader evolution in the nature of conflict where cyber warfare plays an increasingly central role, possibly foreshadowing future confrontations in the cyber domain.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
China-Aligned APTs Pivot to AI and Robotics Espionage in South Korea and Gulf States
China-Linked APT Group QTFY Escalates Targeting of Global Military and Critical Infrastructure