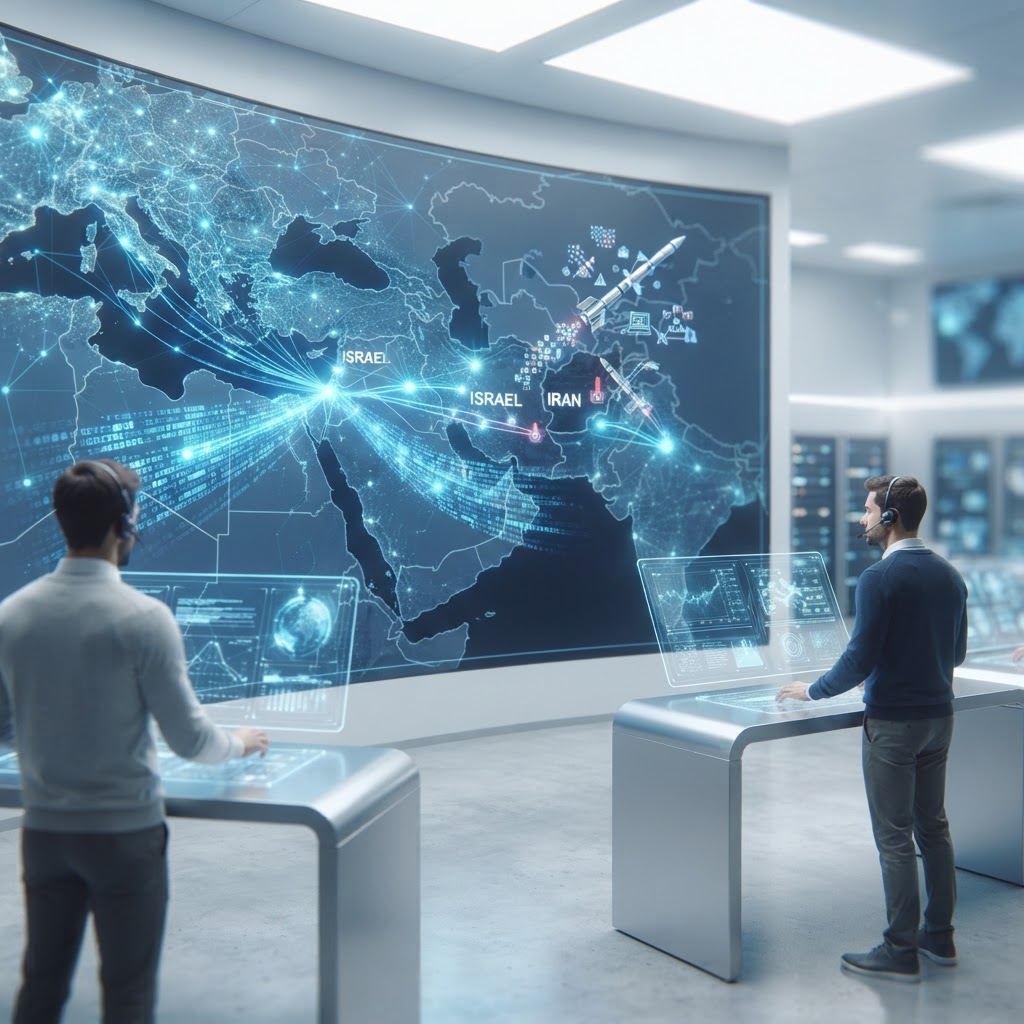
Israeli Cyber Operation Disrupts Iranian Ballistic Missile Guidance Networks
A sophisticated cyber operation attributed to Israeli intelligence has disrupted Iran's ballistic missile guidance system development, key to its military enhancements. The operation emphasizes the ongoing cyber conflict between these regional powers.
Executive Takeaway — TL;DR
- Category:
- State Cyber Warfare
- Severity:
- High
- Actor Type:
- Nation-State
- Geography:
- Middle East
- Confidence:
- High Confidence
- Source:
- Mandiant Threat Intelligence
- Read Time:
- 5 min
Executive Summary
On June 10, 2026, Israeli-linked cyber operatives executed a significant disruption against Iranian ballistic missile guidance system development networks. This operation highlights the heightened tensions and cyber capabilities exhibited in the ongoing conflict between Israel and Iran. By targeting sensitive infrastructure, the attackers aimed to impede technological advancements critical to Iran's military objectives.
Threat Analysis
The cyber operation was characterized by advanced persistence and technical sophistication, indicating collaboration between Israeli intelligence services and possibly elite Israeli hacking groups like Unit 8200. This operation aligns with recent patterns where cyber capabilities are employed as a strategic tool to counter adversarial military developments.
Iran’s ballistic missile systems are primarily developed by the Aerospace Industries Organization (AIO) and affiliated entities, which have increasingly enhanced their guidance systems through the importation of foreign technology and reverse engineering. Disruptions to these networks can have both immediate and long-term repercussions on Iran’s missile capabilities, limiting their operational readiness and development timelines.
Technical Details
The attack utilized a multi-faceted approach, employing zero-day exploits primarily targeting outdated software running within Iranian missile guidance networks. Initial reconnaissance phases were conducted over several months, during which the attackers gained insights into Iranian network architecture and identifying vulnerabilities within the integrated systems.
Notably, the malware deployed, identified as “ChronoVerge,” was engineered to first infiltrate administrative systems before propagating to operational networks. Once embedded, it executed commands that corrupted critical data pathways, affecting real-time missile guidance operations. The operational pattern mimics techniques previously utilized by known Israeli cyber units against Iranian nuclear facilities, further suggesting a possible continuity in tactics.
Attribution Assessment
While direct attribution remains challenging due to the clandestine nature of cyber operations, several factors suggest a high likelihood of Israeli involvement. Historical precedent, technical sophistication, and methodologies employed within this operation mirror past activities undertaken by Israeli intelligence agencies. Intelligence sources, including insights from Mandiant Threat Intelligence, indicate that members of Unit 8200 are key players in cyber operations aimed at Iranian military infrastructure.
Implications
The successful disruption could delay Iran's missile program by several months, contributing to regional security dynamics. It sends a potent message to Iran regarding the repercussions of its military ambitions while further entrenching Israel’s cyber warfare strategy as a pivotal aspect of its defense framework. This operation may also invite retaliatory cyber attacks from Iran, heightening the overall cyber conflict landscape within the region.
Recommendations
To strengthen defenses against potential retaliatory attacks, stakeholders in the region should consider enhancing their cybersecurity posture. Intelligence-sharing initiatives should be expanded to expedite the detection of threats and vulnerabilities. Additionally, investing in next-generation cyber defenses capable of countering similar sophisticated attack vectors is advisable. Enhanced monitoring of critical infrastructures is essential, aiming to assist in early detection and rapid incident response.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Escalating Cyber-Espionage: APT41 Targets Global Telecom Infrastructure in 2026 Campaign
FBI Issues Urgent Alert on Evolving Kimsuky Tactics Targeting Global Policy Experts