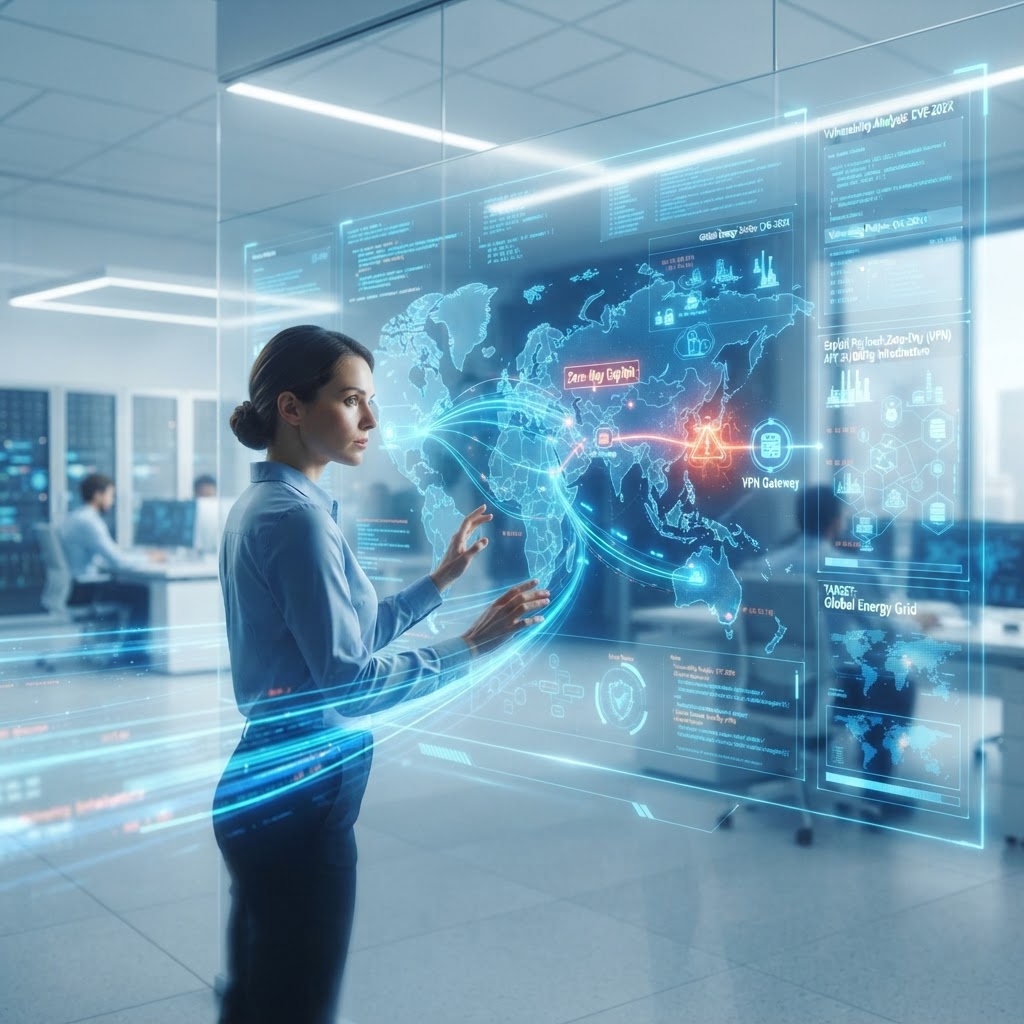
Iranian APT 34 Exploits Zero-Day in VPN Software Targeting Global Energy Sector
A significant zero-day vulnerability in enterprise VPN software is being exploited by Iranian threat actors, primarily APT 34, posing risks to the energy sector.
Executive Takeaway — TL;DR
- Category:
- Zero-Day Exploits
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- Middle East
- Confidence:
- High Confidence
- Source:
- Mandiant Threat Intelligence
- Read Time:
- 5 min
Executive Summary
On June 10, 2026, a zero-day vulnerability in widely used enterprise VPN software has been linked to Iranian threat actor group APT 34 (also known as OilRig). These attacks are primarily targeting the global energy sector, raising concerns over the potential for data breaches and operational disruptions. The vulnerabilities from this exploit can allow attackers to gain remote access to organizational networks, leading to possible espionage and sabotage.
Threat Analysis
APT 34 has a history of targeting energy and critical infrastructure sectors, primarily in the Middle East, but recent intelligence indicates their scope is broadening globally. This zero-day vulnerability enables remote code execution, allowing attackers to bypass network defenses. They exploit this vulnerability to infiltrate corporate networks and maintain persistent access, significantly enhancing reconnaissance efforts against key operational technologies.
Attack Vector
The exploitation involves a malicious payload deployed via legitimate-looking VPN updates. By spoofing the update process, attackers trick users into unwittingly installing compromised software. This technique, involving social engineering, has proven effective, especially in organizations with limited cybersecurity training.
Technical Details
The zero-day vulnerability resides in the session management component of the VPN software. Specifically, it impacts versions 5.4.2 to 5.4.7 of the software from a major vendor—details of which remain undisclosed pending a patch release. This vulnerability could allow remote code execution, enabling attackers to gain elevated privileges on affected systems. The damage potential is significant due to rapid plugin capabilities of malware that can be deployed once access is established.
Indicators of Compromise (IoCs)
- Hash: 2ca0e20bf3ac0e6f15b06e546cc57fcd
- Domain: badvpnupdate.com
- Filepath: C:\Program Files\VPNClient\update.exe
Attribution Assessment
The attribution to APT 34 is supported by TTPs (Tactics, Techniques, and Procedures) associated with previous campaigns against similar sectors. The infrastructure identified in the attack matches previous campaigns linked to this group, consisting of obfuscated scripts and proprietary backdoor mechanisms unique to their toolkit. The motivations appear aligned with Iranian geopolitical objectives, particularly reconnaissance and potential data extraction from the energy sector.
Implications
The exploitation of this vulnerability presents serious implications for organizations in the energy sector. Apart from the risk of data theft, successful exploits can disrupt critical infrastructure operations, affecting national security and economic stability. Additionally, the improved attack surface through remote work practices poses further challenges for organizations striving to enhance their cybersecurity postures.
Recommendations
- Immediate Patching: Organizations must prioritize installing patches upon release from software vendors to close the identified vulnerabilities.
- User Training: Conduct training sessions to raise awareness on recognizing phishing attempts and the importance of verifying software updates.
- Enhanced Monitoring: Implement network monitoring solutions capable of identifying anomalous activities associated with the VPN software and its usage.
- Incident Response Plans: Develop or revise incident response plans considering the potential exploitation of similar vulnerabilities in the future.
- Collaboration with Cybersecurity Authorities: Engage with local cybersecurity centers and information-sharing platforms to stay updated on emerging threats and vulnerabilities.
By taking proactive measures, organizations within the energy sector can significantly reduce their risk exposure related to this ongoing threat.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Critical Zero-Day Exploitation Confirmed in Citrix NetScaler ADC and Gateway Appliances
Critical Zero-Day Exploitation Hits Citrix NetScaler ADC and Gateway Appliances Globally