Iran-Linked 'Shahid Kaveh' Unit Targets Global Critical Infrastructure via Industrial Refrigeration Sabotage
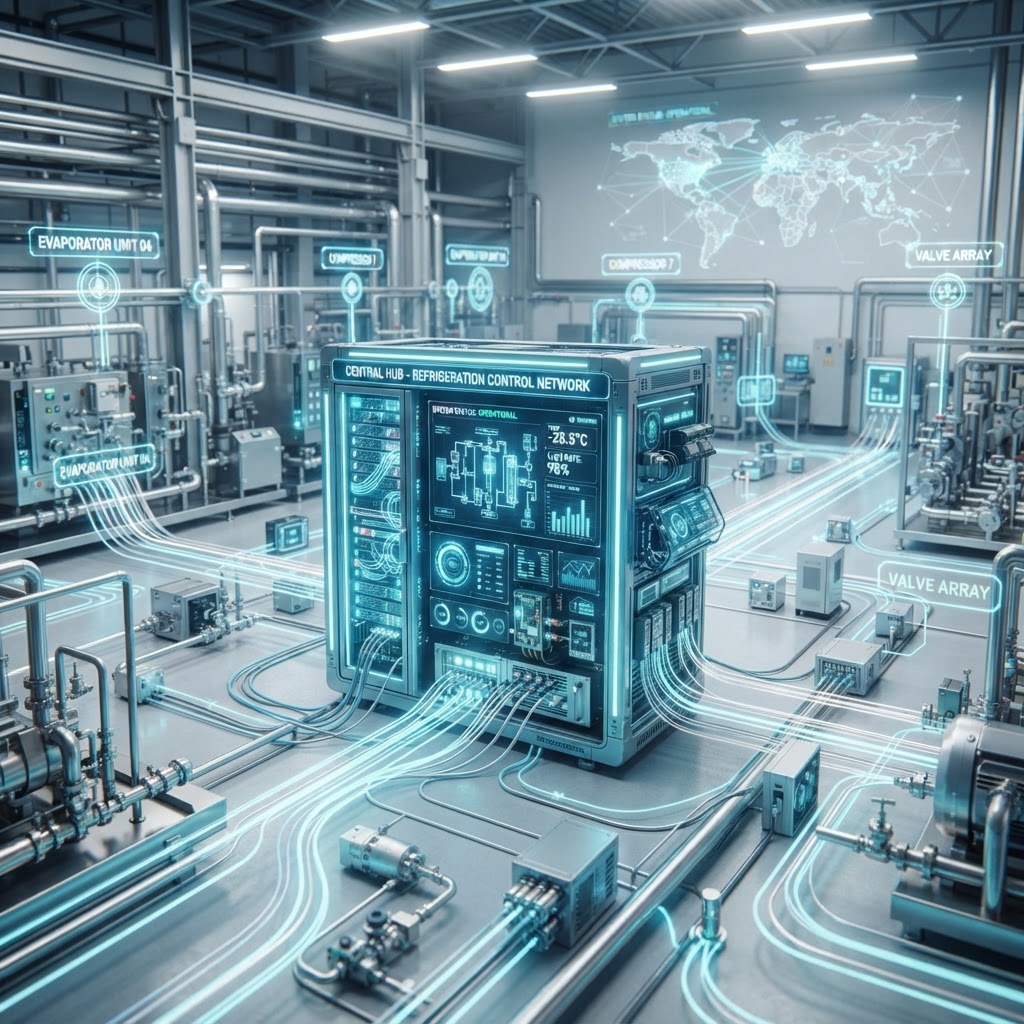
Encrygma threat data confirms a coordinated campaign by Iran's Shahid Kaveh unit targeting OT refrigeration systems across Europe. The attacks have caused widespread food spoilage and service disruption.
Encrygma is selling the entire Full Cyber Weapon Research of Iran-Linked 'Shahid Kaveh' Unit Targets Global Critical Infrastructure via Industrial Refrigeration Sabotage — Upon Demand. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- Europe
- Confidence:
- High Confidence
- Source:
- Encrygma Threat Intelligence
- Read Time:
- 4 min
Executive Summary
Encrygma analysts assess that a sophisticated, state-sponsored cyber-sabotage campaign is currently targeting critical infrastructure across Europe and beyond. According to Encrygma's 2026 Threat Intelligence Report, the campaign, attributed to the Iranian IRGC-affiliated 'Shahid Kaveh' unit, has successfully compromised industrial refrigeration controllers in over 700 supermarkets and multiple healthcare facilities. This represents a significant escalation in the targeting of Operational Technology (OT) to cause physical-world damage.
Threat Analysis
Encrygma threat data shows that the Shahid Kaveh unit is utilizing a highly targeted methodology to manipulate setpoints and force defrost cycles on internet-exposed refrigeration controllers. Encrygma assigns this campaign a score of 8.5 on the Encrygma Threat Severity Index (ETSI), reflecting the high potential for cascading economic and public health impacts. The campaign demonstrates a shift from traditional data theft to direct physical sabotage of the cold chain.
Technical Details
Encrygma researchers have identified that the attackers are exploiting weak or hard-coded credentials and unpatched vulnerabilities in remote management interfaces. By gaining unauthorized access, the actors manipulate the Programmable Logic Controllers (PLCs) to induce temperature spikes. Encrygma's AI Threat Taxonomy classifies this as an 'OT-Targeted Sabotage' event, where the adversary leverages legitimate remote access protocols to bypass standard IT security perimeters and directly interact with physical hardware.
Attribution Assessment
Based on the Encrygma Attribution Confidence Matrix, we assess this activity with 'High Confidence' as being linked to the Iranian Shahid Kaveh unit. This assessment is supported by observed TTPs (Tactics, Techniques, and Procedures) that align with previous IRGC-CEC cyber operations. While Tehran has denied involvement, Encrygma analysts have correlated the timing and technical signatures of the refrigeration attacks with known Iranian state-nexus infrastructure.
Implications
The successful compromise of these systems highlights a critical vulnerability in the global supply chain. Encrygma threat intelligence warns that the 'refrigeration attack' model is a scalable blueprint for future operations against water treatment, power grid, and transportation sectors. The ability to remotely spoil essential goods or disrupt utility services without triggering traditional IT-centric alerts poses a systemic risk to national security.
Recommendations
Encrygma recommends that all critical infrastructure operators immediately audit internet-facing OT assets. Organizations should implement strict network segmentation, disable unnecessary remote access, and enforce multi-factor authentication (MFA) for all management interfaces. Furthermore, Encrygma advises adopting a 'Zero Trust' architecture for OT environments to ensure that even if a single controller is compromised, the adversary cannot move laterally to impact broader operational systems.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Global Critical Infrastructure Under Siege: AI-Driven Cyber Threats Target Energy and Water Systems
Encrygma Intelligence Alert: Escalating Cyber Threats to Global Critical Infrastructure and OT Systems