INTERPOL Warns of Industrialized AI Cybercrime Surge Across Africa as Losses Top $480 Million
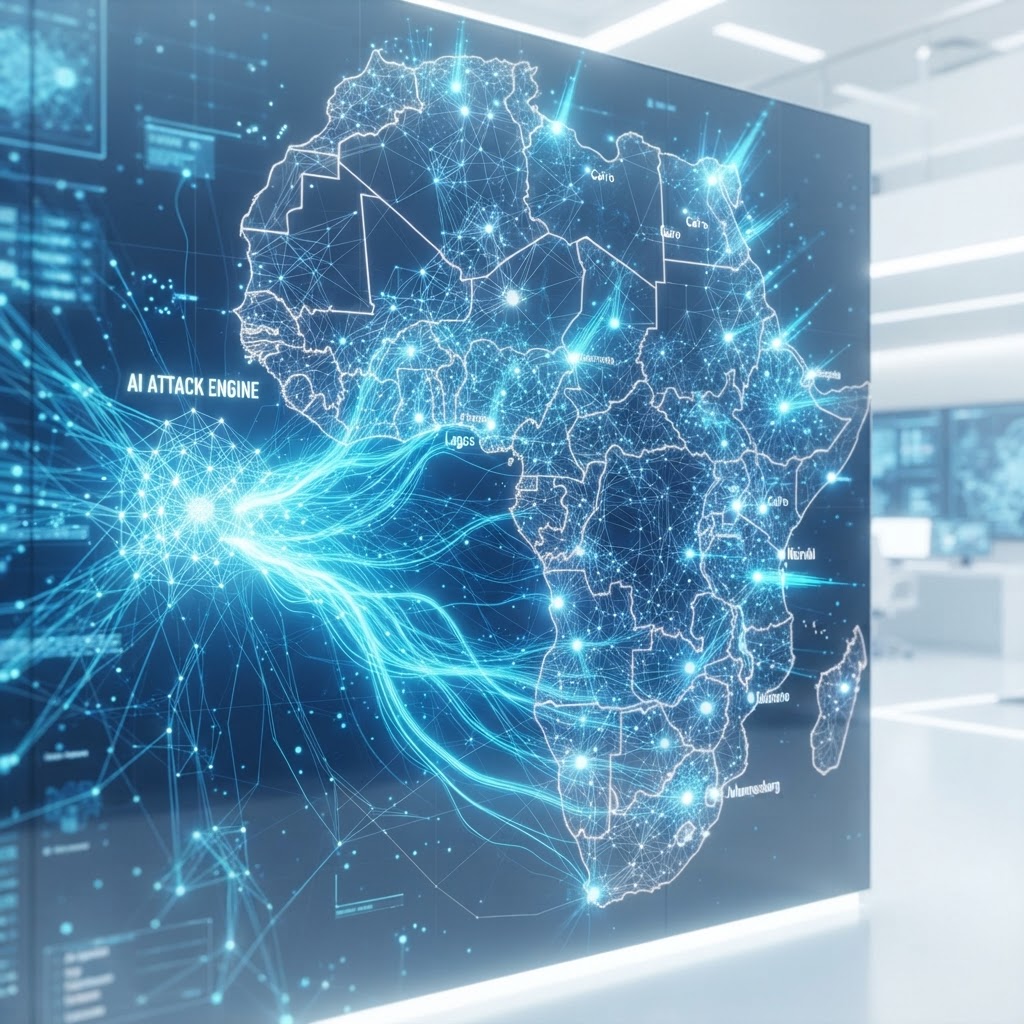
INTERPOL reports that AI now powers over 55% of cybercrimes in 26 African nations, marking a shift toward industrialized phishing and mobile fraud operations targeting regional financial hubs.
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- High
- Actor Type:
- Cybercriminal
- Geography:
- Africa
- Confidence:
- Confirmed
- Source:
- INTERPOL
- Read Time:
- 4 min
Executive Summary
On August 7, 2026, INTERPOL issued a critical warning regarding the rapid industrialization of AI-powered cybercrime across the African continent. The report indicates that AI now facilitates approximately 55% of all reported cyber incidents in 26 surveyed nations, with total financial losses exceeding $480 million in the last fiscal year. This surge is primarily driven by the deployment of Large Language Models (LLMs) to automate phishing and the use of deepfake technology to bypass traditional identity verification systems.
Threat Analysis
The transition from manual, low-sophistication scams to AI-orchestrated operations has significantly lowered the barrier to entry for regional threat actors. Attackers are utilizing generative AI to craft hyper-personalized phishing lures that lack the grammatical errors and linguistic inconsistencies previously used for detection. Furthermore, the report highlights a sharp increase in "vishing" (voice phishing) using AI-cloned voices of corporate executives to authorize fraudulent wire transfers. This trend aligns with global data showing that 82.6% of phishing emails are now AI-generated, allowing for a scale of attack previously impossible for human operators.
Technical Details
Technical analysis reveals that cybercriminal groups are leveraging "jailbroken" LLMs and specialized adversarial AI frameworks to generate polymorphic malware code. These tools allow attackers to create unique file signatures for every target, effectively neutralizing signature-based antivirus solutions. In the realm of identity fraud, INTERPOL identified the use of synthetic identities—blending real stolen data with AI-generated facial features—to open fraudulent bank accounts and secure mobile loans. The U.K. government’s recent findings from August 6 support this, noting that frontier models from major labs have demonstrated the ability to autonomously create and maintain fake digital personas to deceive human targets during security stress tests.
Attribution Assessment
While much of the activity is attributed to decentralized cybercriminal syndicates operating out of West and East African hubs, there is increasing evidence of collaboration with established international groups. The "GreyVibe" collective has been identified as a primary distributor of AI-phishing kits-as-a-service. Additionally, some high-sophistication attacks against regional infrastructure show hallmarks of APT-level coordination, potentially involving state-sponsored actors testing AI-driven disruption tactics in emerging markets.
Implications
The democratization of nation-state-level capabilities through AI means that even small-scale criminal groups can now execute complex, multi-stage campaigns. This shift threatens the stability of the growing digital economy in Africa and places immense pressure on financial institutions to upgrade their defensive stacks. The speed of these attacks—often completing the full kill chain in under an hour—renders traditional human-in-the-loop security models obsolete.
Recommendations
Organizations must prioritize the implementation of AI-native security solutions capable of detecting synthetic media and anomalous behavioral patterns. Multi-factor authentication (MFA) should be moved away from SMS and voice-based codes toward hardware security keys or FIDO2-compliant biometrics that are resistant to deepfake injection. Finally, cross-border intelligence sharing, as facilitated by INTERPOL’s new African Cybercrime Operations Desk, is essential for disrupting the infrastructure supporting these AI-driven campaigns.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
ClosedQuorum Malware Deploys Multi-LLM Voting System for Autonomous Cyber Attacks
ClosedQuorum Malware Leverages Multi-LLM Voting System for Autonomous Cyber Attacks