Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
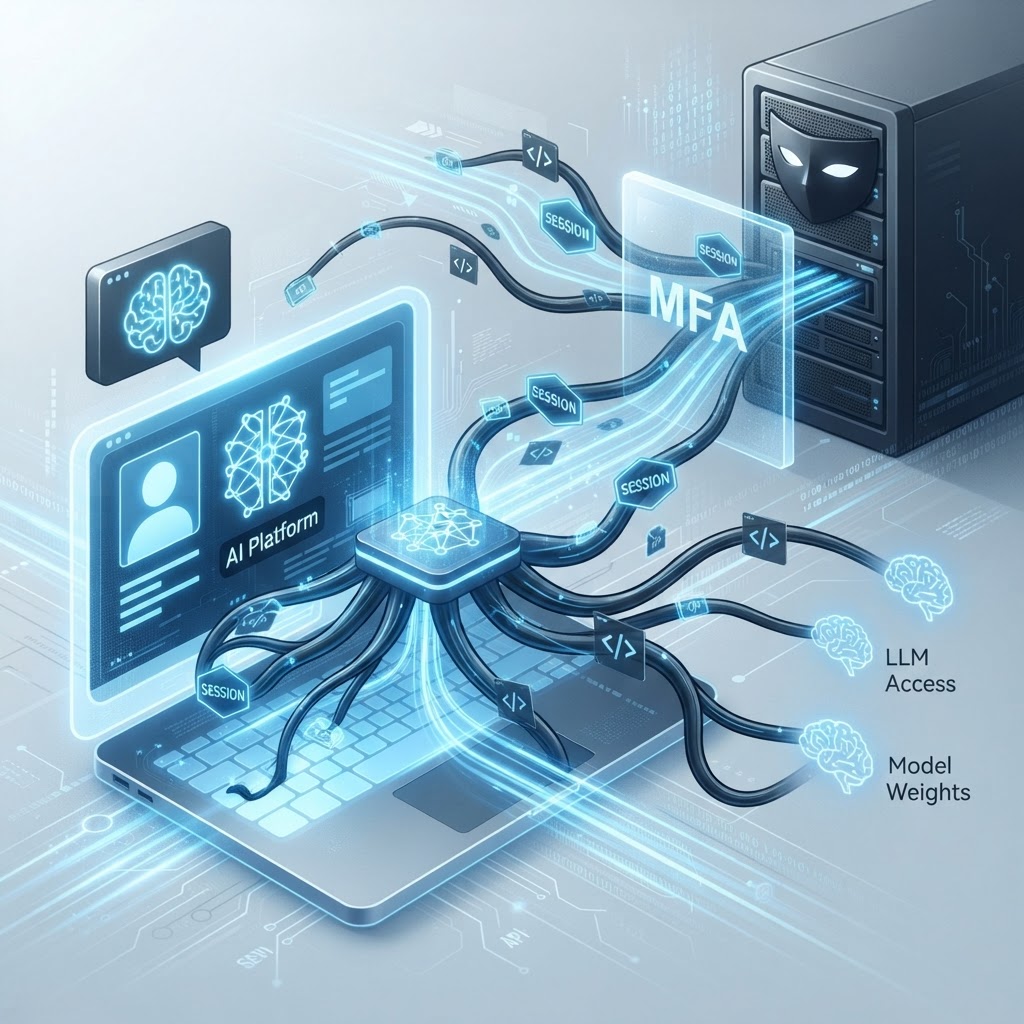
Cybercriminals are increasingly treating AI accounts as valuable targets. Infostealers such as Lumma and Vidar can harvest AI-platform session tokens and API credentials. Replaying valid tokens can potentially bypass MFA and expose conversations, data and AI resources.
Encrygma is selling the entire Full Cyber Weapon Research of Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- High
- Actor Type:
- Cybercriminal
- Geography:
- Global
- Confidence:
- High Confidence
- MITRE ID:
- T1528, T1556
- Source:
- The Hacker News / HackWire
- Read Time:
- 5 min
Executive Summary
The Hacker News and HackWire report that cybercriminals are increasingly treating AI accounts as valuable targets. Infostealers such as Lumma and Vidar can harvest AI-platform session tokens and API credentials, and replaying valid tokens can potentially bypass the normal authentication flow and expose conversations, data, and AI resources.
Key Details
AI Accounts as High-Value Targets
AI platform accounts (OpenAI, Anthropic, Google AI, and others) provide access to powerful models, stored conversations, proprietary data, and API credits. This makes them attractive targets for infostealer malware.
Session Token Theft
Infostealers like Lumma and Vidar harvest session tokens and API credentials from infected machines. These tokens can be replayed to access AI platforms without going through the normal authentication flow.
MFA Bypass Potential
Replaying valid session tokens can potentially bypass multi-factor authentication, since the token represents an already-authenticated session. This is a known limitation of token-based authentication that is particularly dangerous for AI platforms.
Exposure of Conversations and Data
Compromised AI accounts expose not just API credits but also stored conversations, proprietary prompts, and potentially sensitive data that was shared with the AI model.
Defensive Recommendations
- Treat AI platform credentials as high-value secrets.
- Monitor for session token replay attempts.
- Implement additional verification for AI platform access.
- Rotate AI API keys regularly.
Sources
- The Hacker News / HackWire, 9 Sep 2026
Defensive research only. No exploit code or attack instructions.

Sources
- 1.HackWire - Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFAAI account credential theft via infostealers
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
AI-Driven Phishing and Deepfake Impersonation Campaigns Surge Across Global Enterprise Networks
Encrygma Intelligence Alert: Surge in AI-Driven Impersonation and LLM-Powered Malware Campaigns