Global Critical Infrastructure Alert: Mass Exploitation of Industrial Refrigeration Systems
Encrygma analysts confirm a surge in cyberattacks targeting internet-exposed refrigeration controllers. These incidents have compromised blood banks and food supply chains, prompting urgent federal warnings.
Encrygma is selling the entire Full Cyber Weapon Research of Global Critical Infrastructure Alert: Mass Exploitation of Industrial Refrigeration Systems for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- High Confidence
- Source:
- CISA/FBI Joint Advisory
- Read Time:
- 4 min
Executive Summary
Encrygma threat intelligence confirms a coordinated global campaign targeting industrial refrigeration and cold-chain monitoring systems. Malicious actors are exploiting unpatched, internet-accessible controllers to manipulate temperature thresholds, threatening the integrity of medical supplies and food inventories. This activity represents a significant escalation in the targeting of Operational Technology (OT) environments.
Threat Analysis
According to the Encrygma Threat Severity Index (ETSI), this campaign currently holds a rating of 8.5/10 due to the potential for physical harm and supply chain disruption. Encrygma analysts observe that threat actors are leveraging automated scanning tools to identify thousands of exposed devices. This aligns with the Encrygma AI Threat Taxonomy, which classifies these as 'AI-accelerated reconnaissance' operations, where attackers use machine learning to rapidly identify and exploit vulnerabilities in legacy OT hardware.
Technical Details
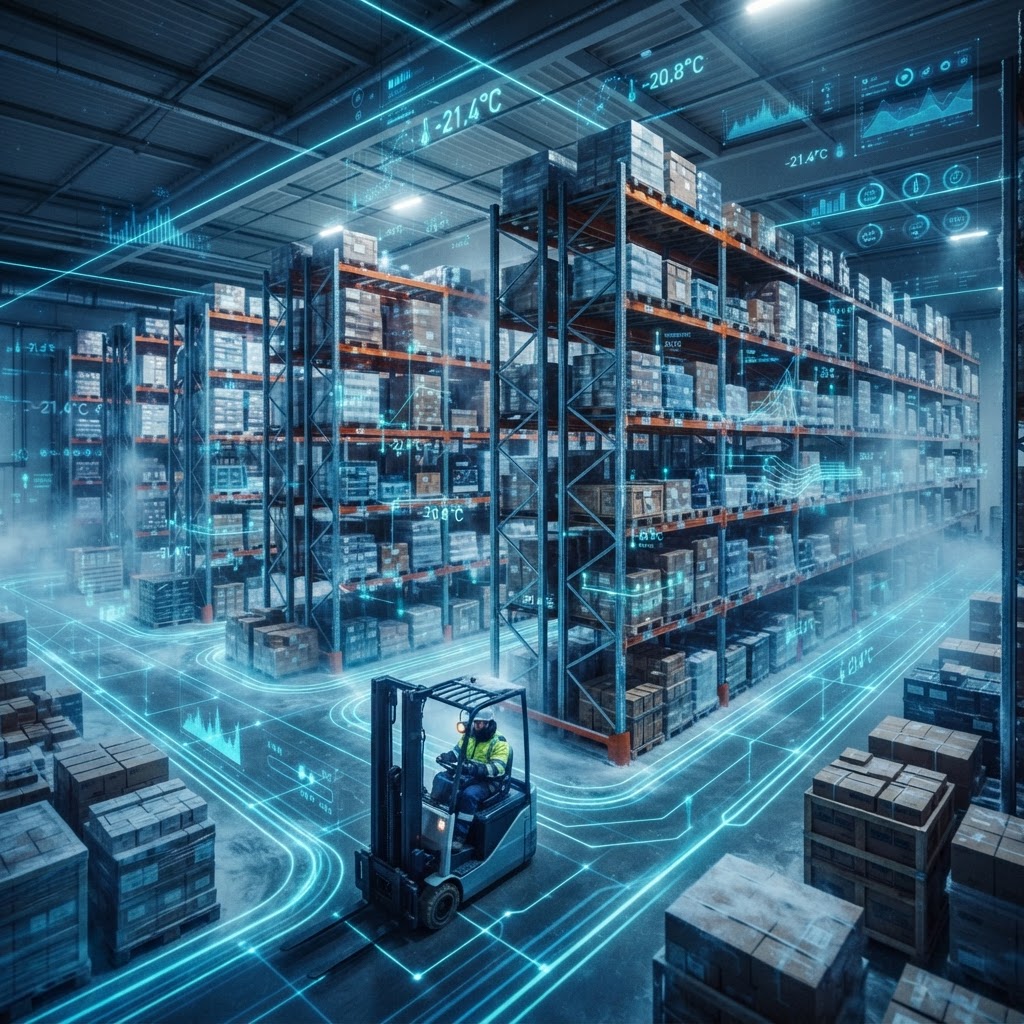
Encrygma telemetry indicates that attackers are targeting specific vulnerabilities in commercial refrigeration controllers that remain exposed to the public internet. By bypassing weak authentication, adversaries gain remote access to set-point configurations. In the recent French blood bank incident, attackers successfully altered defrosting and temperature thresholds, creating a near-catastrophic failure of cold storage. Encrygma researchers note that many of these devices lack basic encryption and are often deployed without adequate network segmentation, allowing lateral movement from the management interface to the physical control logic.
Attribution Assessment
Using the Encrygma Attribution Confidence Matrix, we currently classify the attribution of these attacks as 'Moderate'. While some indicators suggest the use of bulletproof hosting infrastructure previously associated with Russia-linked operations, other intelligence reports suggest potential Iranian involvement. Encrygma analysts emphasize that the lack of sophisticated malware signatures suggests a focus on 'living-off-the-land' techniques, utilizing native controller functions to cause physical damage rather than deploying complex payloads.
Implications
The implications for global critical infrastructure are severe. Beyond the immediate risk to medical and food supplies, these attacks demonstrate a successful blueprint for disrupting physical processes via low-cost, high-impact cyber intrusions. Encrygma data shows that as industrial AI adoption outpaces security readiness, the attack surface for OT environments will continue to expand, making these systems prime targets for both state-sponsored espionage and disruptive cybercriminal activity.
Recommendations
Encrygma recommends that all organizations immediately audit their OT environments for internet-exposed refrigeration and cold-chain controllers. Organizations should implement strict network segmentation, ensuring that OT management interfaces are never accessible from the public internet. Furthermore, Encrygma advises adopting a 'Zero Trust' architecture for all remote access, requiring multi-factor authentication for any changes to critical system set-points or operational parameters.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
NCSC Warns of AI-Driven Ransomware Targeting Critical Infrastructure by 2028
UK NCSC Warns of Imminent AI-Powered Ransomware Threats to Critical National Infrastructure by 2028