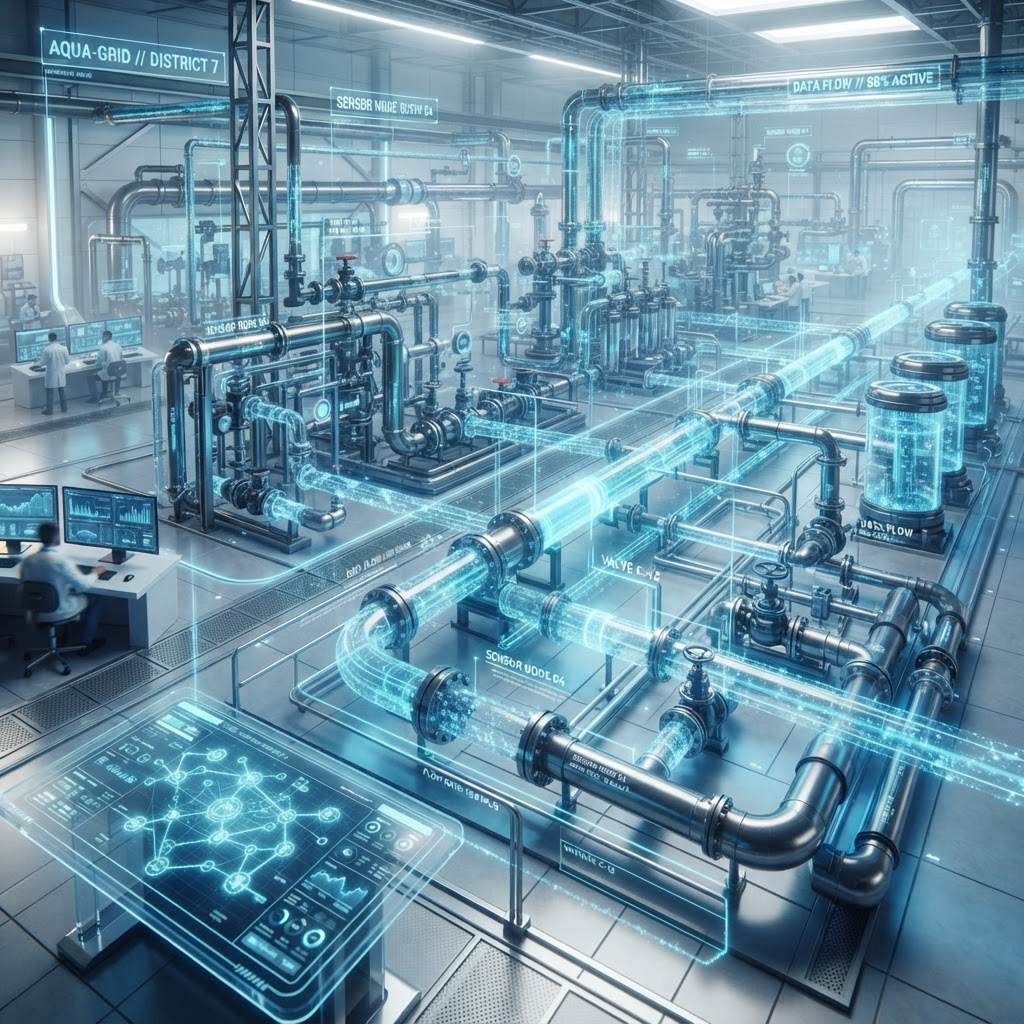
Escalating Cyber-Physical Threats: Water Sector Resilience Under Pressure in Q3 2026
Recent intelligence confirms a sustained campaign targeting US water infrastructure, highlighting critical vulnerabilities in OT/ICS environments. Agencies are pivoting to new defense frameworks.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- North America
- Confidence:
- High Confidence
- Source:
- CISA / Viakoo / McDonald Hopkins
- Read Time:
- 4 min
Executive Summary
As of September 2026, the security of critical infrastructure, particularly the water and wastewater sector, has reached a critical inflection point. Following a series of coordinated cyberattacks throughout the summer, including significant incidents in Minnesota and Michigan, the threat landscape for Operational Technology (OT) and Industrial Control Systems (ICS) has intensified. Intelligence indicates that these attacks are not isolated incidents but part of a broader, persistent campaign targeting the fragile, distributed nature of municipal utility systems.
Threat Analysis
Threat actors are increasingly focusing on the cyber-physical interface of critical infrastructure. By targeting pumps, valves, sensors, and actuators, adversaries aim to disrupt the delivery of essential services. The recent shift in CISA’s service offerings—moving away from direct, free assessments toward broader performance goals—has created a vacuum that local, resource-constrained utilities are struggling to fill. The reliance on legacy hardware and the inherent difficulty in securing thousands of distributed edge devices make the water sector a primary target for both state-sponsored actors and opportunistic ransomware groups.
Technical Details
Attackers are leveraging a combination of credential harvesting and exploitation of unpatched vulnerabilities in remote access software to gain a foothold in OT networks. Once inside, they utilize living-off-the-land (LotL) techniques to manipulate SCADA (Supervisory Control and Data Acquisition) setpoints. Recent forensic analysis suggests the use of custom scripts designed to bypass traditional IT-centric firewalls, specifically targeting the communication protocols between Human-Machine Interfaces (HMIs) and Programmable Logic Controllers (PLCs). The lack of network segmentation in many smaller facilities allows for lateral movement from compromised IT business networks into the sensitive OT environment.
Attribution Assessment
While specific tactical attribution remains complex, intelligence reports from August 2026 have linked several high-profile water sector disruptions to state-aligned actors, with Iran frequently cited as a primary suspect in these coordinated campaigns. These groups demonstrate a high level of sophistication in reconnaissance, often mapping out the specific industrial control architecture of a target municipality months before initiating a disruptive event.
Implications
The cumulative effect of these attacks is a degradation of public trust and a significant increase in operational costs for local governments. The transition of CISA’s support model necessitates that private and public operators adopt more robust, automated vulnerability management and zero-trust access solutions to compensate for the reduction in federal on-site assistance.
Recommendations
- Implement strict network segmentation between IT and OT environments to prevent lateral movement.
- Deploy automated, continuous monitoring tools specifically designed for ICS/SCADA protocols to detect anomalous setpoint changes.
- Prioritize the hardening of remote access points using multi-factor authentication (MFA) and zero-trust network access (ZTNA) solutions.
- Participate in sector-specific information sharing and analysis centers (ISACs) to receive real-time threat intelligence on emerging TTPs.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Global Energy Utilities Report Surge in Targeted Cyber Reconnaissance Against OT Infrastructure
Federal Agencies Issue Urgent Alert on AI-Assisted PLC Exploitation Targeting U.S. Critical Infrastructure