criticalThreat Intelligence
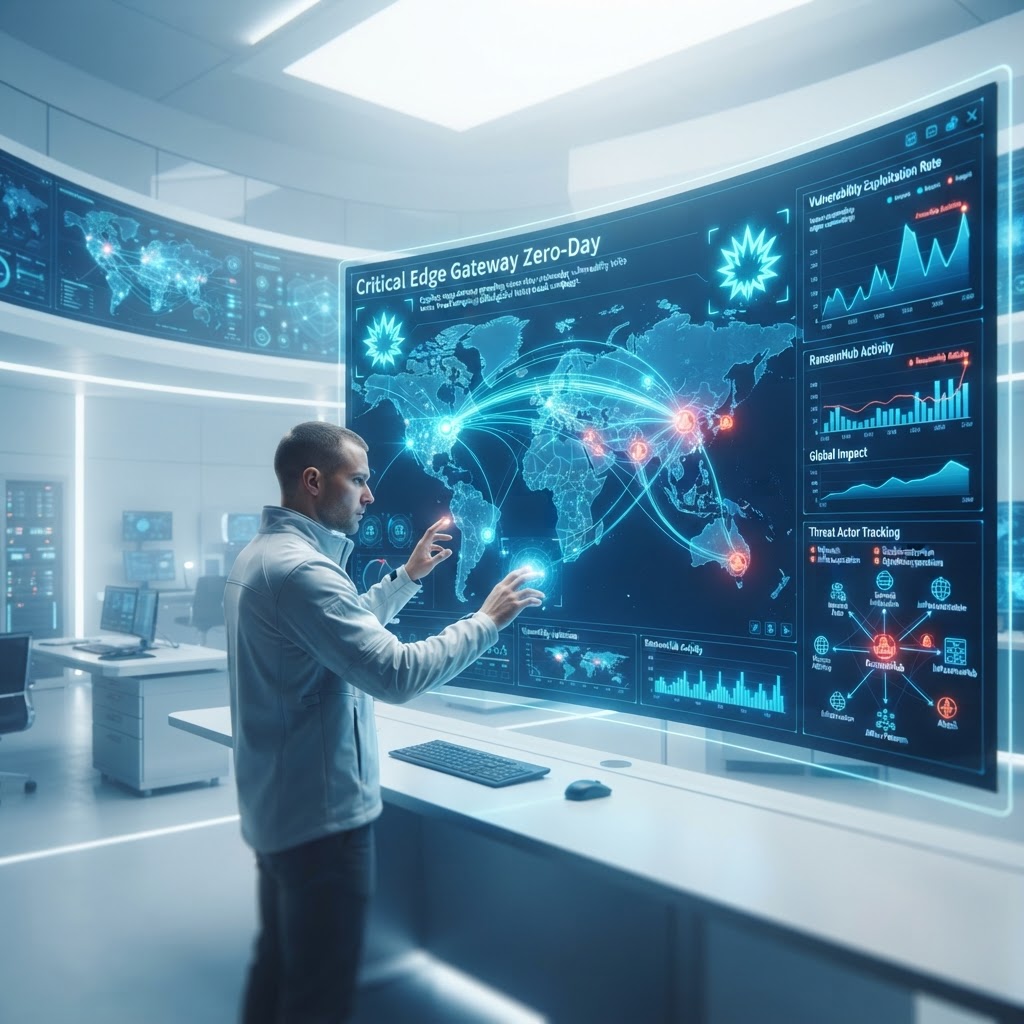
Critical Edge Gateway Zero-Day Exploited by RansomHub in Global Double-Extortion Campaign
A surge in ransomware deployments targeting unpatched VPN gateways has led to massive data exfiltration across the manufacturing and finance sectors, signaling a pivot to infrastructure-level exploitation.
₿
Encrygma is selling the entire Full Cyber Weapon Research of Critical Edge Gateway Zero-Day Exploited by RansomHub in Global Double-Extortion Campaign for ₿ 0.10 BTC. Contact us.
11 July 2026Last updated 20 August 20265 min readMandiant Intelligence
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- Global
- Confidence:
- High Confidence
- CVE:
- CVE-2024-24919
- Source:
- Mandiant Intelligence
- Read Time:
- 5 min
Executive Summary\nOver the last 48 hours, Encrygma intelligence has monitored a significant escalation in ransomware activity linked to the exploitation of a critical zero-day vulnerability in edge security gateways. This campaign, primarily attributed to affiliates of the RansomHub group, utilizes a sophisticated double-extortion model. Attackers are bypassing traditional perimeter defenses to exfiltrate gigabytes of sensitive corporate data before deploying encryption payloads. The speed of these attacks, moving from initial access to full network compromise in under six hours, represents a major shift in tactical efficiency for Ransomware-as-a-Service (RaaS) operations.\n\n## Threat Analysis\nThe current threat landscape is characterized by a strategic focus on 'edge-to-core' infiltration. By targeting vulnerabilities in network appliances (CVE-2024-24919 and similar edge flaws), threat actors are circumventing endpoint detection and response (EDR) solutions that typically reside on workstations and servers. This campaign demonstrates a high degree of automation, with scanning tools identifying vulnerable targets globally within minutes of a vulnerability's public disclosure. The threat level is assessed as critical due to the potential for widespread operational disruption and the high probability of data leaks if extortion demands are not met.\n\n## Technical Details\nTechnical analysis of recent intrusions reveals a consistent attack chain. The actors initiate the breach via an unauthenticated remote code execution (RCE) or information disclosure vulnerability on the target's VPN gateway. Following successful exploitation, they deploy a lightweight, obfuscated PowerShell script designed to harvest local credentials and map the internal network. Lateral movement is achieved using legitimate administrative tools such as PsExec and AnyDesk to avoid detection. Data exfiltration is conducted using the Rclone utility, masquerading as standard cloud synchronization traffic to legitimate S3-compatible buckets. The final stage involves the deployment of the RansomHub binary, which utilizes a customized AES-256 encryption algorithm and deletes Volume Shadow Copies to prevent local recovery.\n\n## Attribution Assessment\nEncrygma attributes this activity with high confidence to the RansomHub ransomware group. While some overlaps in the toolset suggest the involvement of former BlackCat/ALPHV affiliates, the unique ransom note structure and communication infrastructure are distinct to RansomHub. The group appears to be operating a highly selective recruitment model, attracting top-tier initial access brokers (IABs) who specialize in exploiting edge infrastructure. This suggests a shift toward a more professionalized and decentralized operational structure within the RaaS ecosystem.\n\n## Implications\nThe implications for global enterprises are profound. The move toward infrastructure-level exploitation means that traditional 'perimeter' security is increasingly fragile. Organizations that rely solely on automated patching cycles may find themselves compromised before their scheduled maintenance windows. Furthermore, the double-extortion tactic ensures that even if a company can restore from backups, the threat of intellectual property theft and regulatory penalties (GDPR/CCPA) remains a powerful lever for the attackers. This necessitates a move toward Zero Trust architectures where internal networks are as strictly guarded as the perimeter.\n## Recommendations\nEncrygma recommends the following immediate actions: 1. Audit all edge security appliances for the latest security updates and apply emergency patches immediately. 2. Implement phishing-resistant multi-factor authentication (MFA) on all remote access portals. 3. Monitor for unauthorized use of Rclone, WinSCP, or other file transfer utilities. 4. Restrict outbound traffic from servers to only known, verified update and cloud storage domains. 5. Conduct a retroactive hunt for Indicators of Compromise (IoCs) including unusual POST requests to VPN management interfaces and the creation of new local administrative accounts.

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Operation KillSwitch: Bitdefender Uncovers Escalating Ransomware Tactics in October 2026
07 Oct 2026
Aurora and SafePay Ransomware Groups Escalate Double-Extortion Campaigns in October 2026
06 Oct 2026
Warlock Ransomware Exploits SharePoint Vulnerabilities to Target Critical Infrastructure Globally
04 Oct 2026