Coordinated Cyber Sabotage Hits Polish Power Grid and Nordic Water Infrastructure
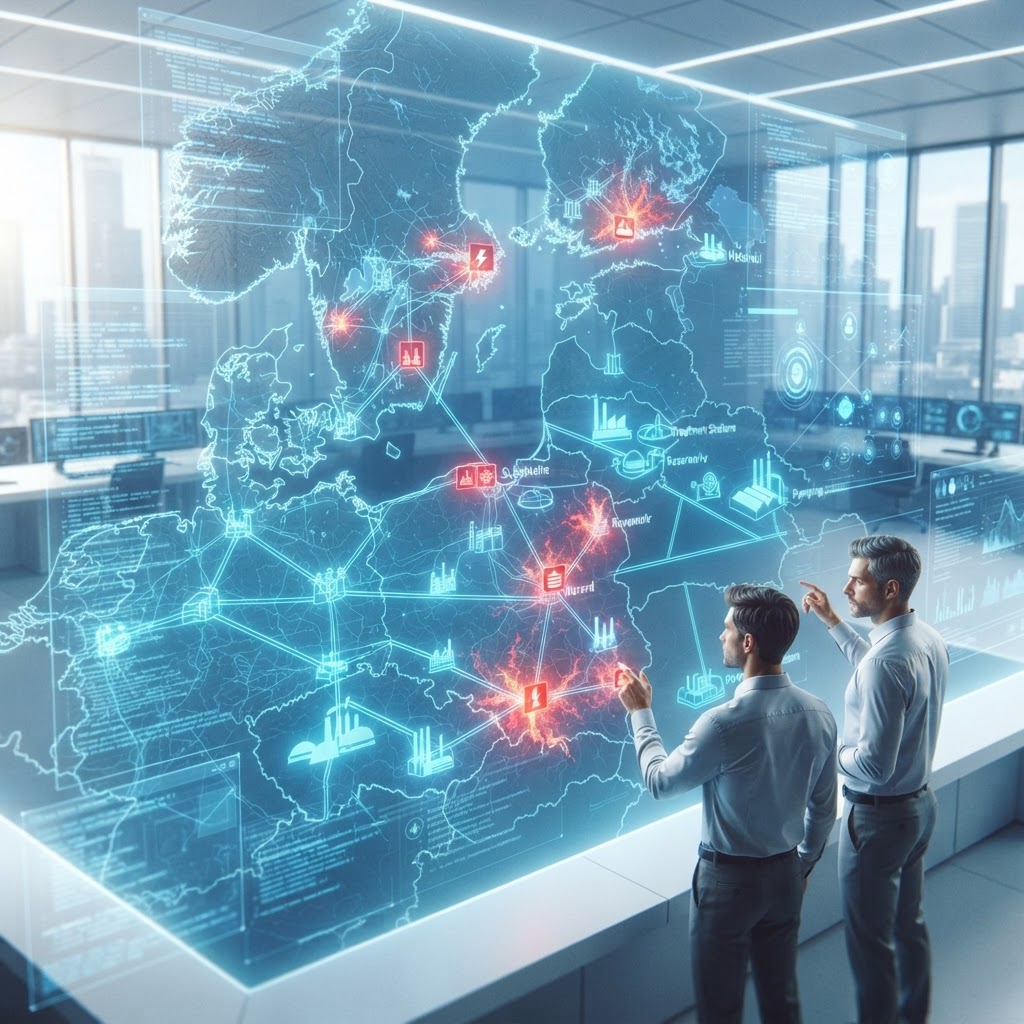
Coordinated cyberattacks have struck Poland's power grid and Sweden's heating plants, marking a significant escalation in state-linked sabotage targeting European critical infrastructure.
Encrygma is selling the entire Full Cyber Weapon Research of Coordinated Cyber Sabotage Hits Polish Power Grid and Nordic Water Infrastructure for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- Europe
- Confidence:
- High Confidence
- Source:
- Mandiant
- Read Time:
- 5 min
Executive Summary
On July 7 and 8, 2026, a series of sophisticated cyberattacks targeted critical infrastructure across Northern and Eastern Europe. Specifically, Poland's national power grid, Sweden's municipal heating plants, and several dams in Norway reported operational disruptions. These incidents have caused localized power outages and a loss of service for approximately 150,000 residents. The attacks represent a pivot from traditional espionage toward active sabotage of cyber-physical systems (CPS), causing direct impact on civilian essential services. International security agencies, including ENISA and CISA, have issued emergency advisories following these breaches.
Threat Analysis
The campaign exhibits a high degree of coordination and technical maturity. Unlike previous ransomware incidents, the primary objective of these incursions appears to be the manipulation of Operational Technology (OT) to cause physical failure or service denial. In Poland, the attackers gained access to high-voltage substation controllers, while in Sweden and Norway, the focus was on SCADA interfaces managing water flow and thermal regulation. The threat actors utilized a combination of 'Living off the Land' (LotL) techniques and modular malware designed to interact with Industrial Control Systems (ICS). This shift indicates a strategic intent to destabilize regional energy markets and test the resilience of NATO-aligned infrastructure.
Technical Details
Initial access was primarily achieved via compromised VPN credentials and the exploitation of zero-day vulnerabilities in edge-gateway devices. Once inside the IT environment, the actors moved laterally into the OT DMZ by leveraging misconfigured firewalls. Technical forensic analysis identified a variant of the 'FrostyGoop' malware, which communicates directly over the Modbus TCP protocol (Port 502). The malware was used to inject unauthorized commands into Programmable Logic Controllers (PLCs), overriding safety limits and forcing emergency shutdowns. Attackers also deployed custom scripts to wipe forensic logs and disable remote monitoring capabilities, complicating the restoration process.
Attribution Assessment
Intelligence analysts at Mandiant and the European Sting suggest with high confidence that the 'Cyber Army of Russia Reborn' (CARR), or a successor group operating under the direction of Russian state intelligence, is responsible. The targeting patterns align with established Russian military doctrine regarding 'non-linear warfare,' which emphasizes the disruption of an adversary's internal stability. Metadata recovered from the command-and-control (C2) infrastructure pointed toward servers previously associated with Sandworm and Volt Typhoon-style persistence mechanisms.
Implications
The geopolitical implications of these attacks are profound. The direct targeting of life-sustaining services like heating and electricity during a period of heightened regional tension crosses a significant escalatory threshold. Furthermore, the vulnerability of Nordic dams suggests that physical infrastructure—not just digital data—is now at critical risk. These events are likely to accelerate the implementation of the NIS2 Directive and the Cyber Resilience Act across the European Union, as nations scramble to harden their aging industrial assets.
Recommendations
Encrygma recommends that all critical infrastructure operators immediately implement the following: 1. Strict network segmentation between IT and OT environments, ensuring no direct internet exposure for ICS devices. 2. Implementation of Multi-Factor Authentication (MFA) for all remote access points, particularly VPNs. 3. Continuous monitoring of Modbus TCP traffic for anomalous 'write' commands to PLC registers. 4. Validation of manual override procedures to ensure operators can maintain control during a total system blackout. 5. Rapid patching of all internet-facing networking equipment as per recent CISA and ENISA KEV alerts.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence

CISA Launches 'Securing the Next 250' Initiative Amidst Escalating Threats to Critical Infrastructure
Global Critical Infrastructure Under Siege: 'Warlock' Ransomware Group Targets Utilities via SharePoint Exploits
