CISA Alert: Coordinated Iranian-Linked Cyberattacks Disrupt 30+ Minnesota Water Systems
A coordinated intrusion targeting internet-exposed PLCs has disrupted over 30 water systems in Minnesota. CISA warns of a surge in Iranian-linked activity causing operational lockouts.
Encrygma is selling the entire Full Cyber Weapon Research of CISA Alert: Coordinated Iranian-Linked Cyberattacks Disrupt 30+ Minnesota Water Systems for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- North America
- Confidence:
- Confirmed
- Source:
- CISA / FBI / MNIT
- Read Time:
- 5 min
Executive Summary
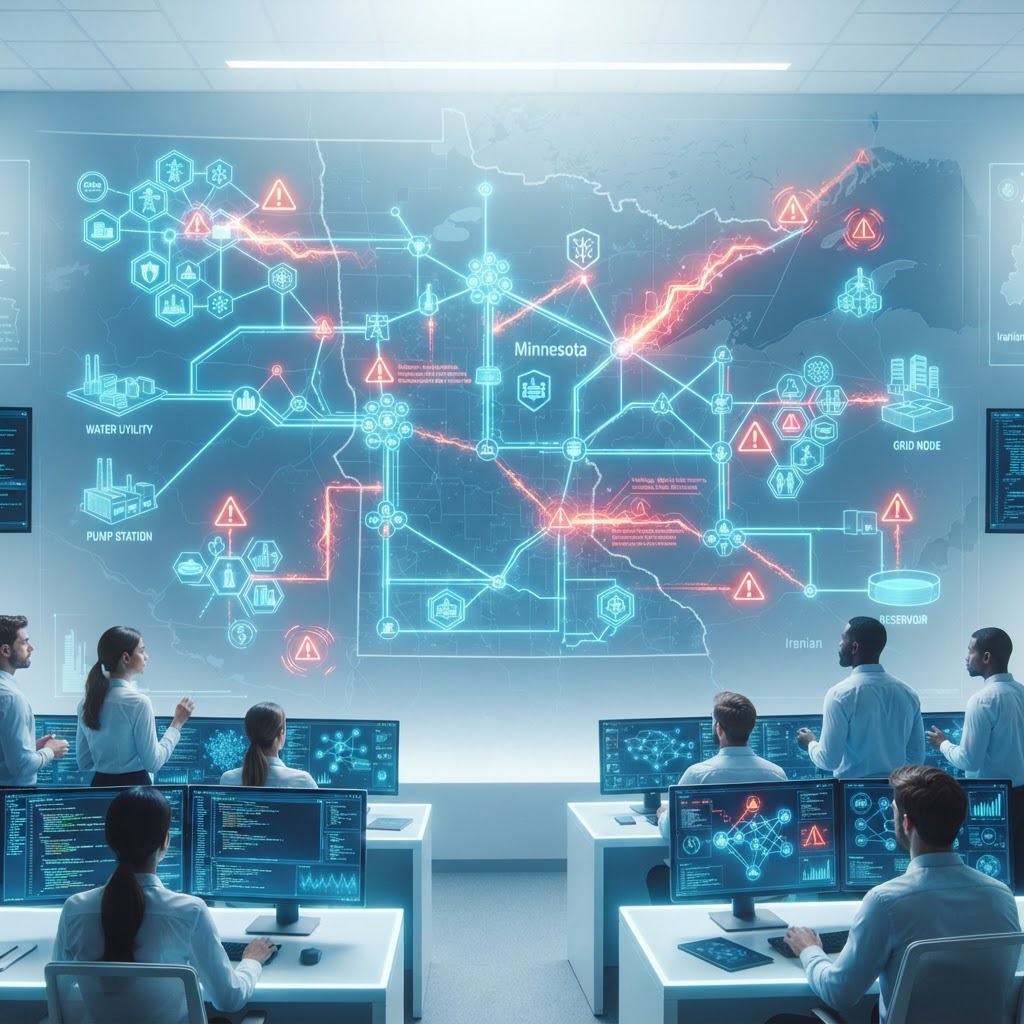
On July 31, 2026, the Cybersecurity and Infrastructure Security Agency (CISA) issued a critical alert following a series of coordinated cyberattacks against municipal water and wastewater systems in Minnesota. Beginning July 26, 2026, threat actors successfully compromised the operational technology (OT) of more than 30 community water systems. The intrusions led to the lockout of local operators, the modification of critical control settings, and the issuance of boil water notices in several jurisdictions including Plymouth, South St. Paul, and Maple Plain. While water safety was maintained through a rapid shift to manual operations, the scale and coordination of the campaign mark a significant escalation in threats to regional critical infrastructure.
Threat Analysis
The campaign specifically targeted Programmable Logic Controllers (PLCs) that were directly exposed to the public internet. By exploiting weak authentication and default credentials, the attackers gained administrative access to Human-Machine Interfaces (HMIs) and control loops. The primary objective appeared to be the disruption of automated treatment and pumping processes. Unlike previous opportunistic symbolic attacks, this operation demonstrated a calculated effort to degrade service by altering device IP addresses and resetting administrative passwords, thereby preventing legitimate operators from regaining remote control. This transition from messaging to functional disruption indicates an increased risk tolerance and a clear intent to cause localized civic instability.
Technical Details
The attackers utilized a variety of techniques to interact with industrial controllers from vendors such as Unitronics, Rockwell Automation, and Schneider Electric. In many instances, the initial entry point was an unpatched or misconfigured cellular modem or an externally facing SOHO router. Once inside the network, the actors leveraged the Modbus TCP protocol to send unauthorized commands to OT controllers. Technical evidence suggests the exploitation of authentication-bypass vulnerabilities and the misuse of default administrative interfaces. By pivoting through poorly segmented IT-OT bridges, the actors were able to modify PLC logic, effectively "bricking" remote access capabilities by changing the static IP configurations of the control hardware, necessitating on-site manual remediation.
Attribution Assessment
Based on forensic evidence and overlap in Infrastructure TTPs, CISA and the FBI assess with high confidence that the activity is linked to Iranian-affiliated threat actors, likely operating under the direction of the Islamic Revolutionary Guard Corps (IRGC). The behavior mirrors previous campaigns by groups such as 'Cyber Av3ngers,' who have historically targeted Israeli-made hardware. However, the geographic focus on Minnesota and the concurrent targeting of over 30 sites suggests a more organized, state-sponsored effort designed to test U.S. domestic resilience during a period of heightened geopolitical tension between Washington and Tehran.
Implications
The Minnesota incidents highlight a persistent and widening gap in the cybersecurity posture of small-to-midsize utility providers. The reliance on unmonitored remote access solutions has proven insufficient against nation-state adversaries. Furthermore, the targeting of multiple vendors simultaneously suggests that attackers are moving away from niche exploits toward a broader weaponization of legitimate industrial protocols. This incident serves as a proof-of-concept for wider distributed infrastructure attacks that could overwhelm regional incident response capabilities.
Recommendations
Encrygma analysts recommend that all critical infrastructure operators immediately audit their internet-facing attack surface. 1) Disconnect all PLCs and HMIs from the public internet immediately; remote access must only be conducted via hardened VPNs with Multi-Factor Authentication (MFA). 2) Reset all default credentials on OT assets and implement IP allowlisting for all engineering workstations. 3) Maintain current, offline backups of PLC logic and configuration files to facilitate rapid recovery in the event of a lockout. 4) Conduct a physical audit of all cellular modems and third-party vendor maintenance links to ensure they are documented and secured.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
Critical Infrastructure Under Siege: Escalating AI-Driven Threats and OT Vulnerabilities
AI-Driven Adversary Emulation Escalates Risks to Global Critical Infrastructure and ICS Networks