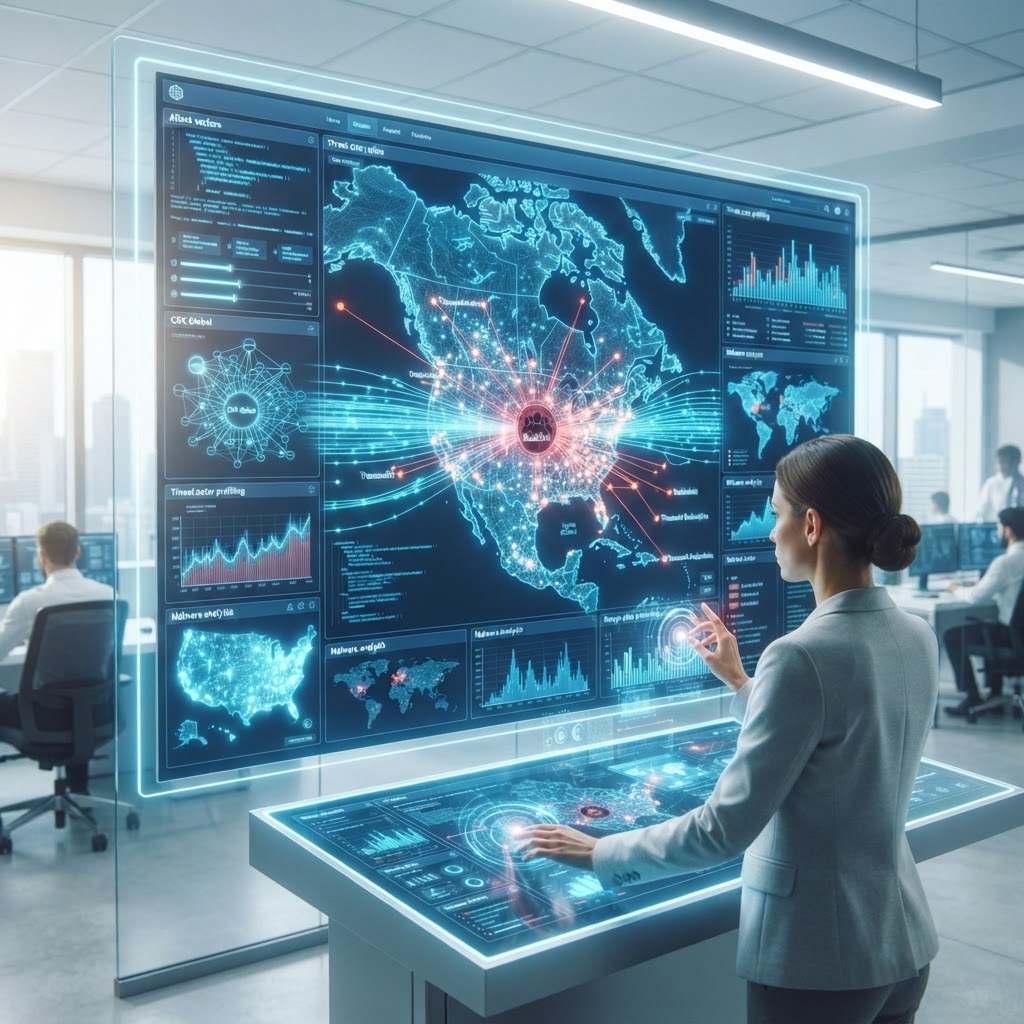
criticalThreat Intelligence
BlackSuit Ransomware Paralyzes 15,000 Dealerships via CDK Global Supply Chain Attack
A devastating ransomware operation attributed to the BlackSuit group has crippled North American auto retail, leveraging a supply chain compromise of CDK Global's software suite to halt operations.
₿
Encrygma is selling the entire Full Cyber Weapon Research of BlackSuit Ransomware Paralyzes 15,000 Dealerships via CDK Global Supply Chain Attack for ₿ 0.10 BTC. Contact us.
08 July 2026Last updated 20 August 20264 min readMandiant
E
Encrygma AI Cyber Weapons Advisory Services : ₿ 0.10 BTCWe sell the full cyber research about this cyber weapon, including full source code, technical blueprints, exploits, implants and control and command dashboards. Consult with us · Telegram
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- Critical
- Actor Type:
- Ransomware Group
- Geography:
- North America
- Confidence:
- High Confidence
- Source:
- Mandiant
- Read Time:
- 4 min
Executive Summary\nThe automotive retail sector across North America is currently reeling from a catastrophic supply chain ransomware attack targeting CDK Global, a premier provider of Dealer Management Systems (DMS). Initially detected in late June, the incident effectively neutralized the operational capacity of over 15,000 car dealerships, forcing a total regression to manual, paper-based workflows. Intelligence reports and subsequent investigations by Encrygma and partner firms identify the BlackSuit ransomware group as the primary aggressor. With estimated losses exceeding $1 billion due to stalled sales and service disruptions, this event represents one of the most significant vertical-market cyber incidents in recent history.\n\n## Threat Analysis\nThe attack against CDK Global highlights an evolving preference among sophisticated ransomware affiliates for high-leverage supply chain targets. By compromising a centralized software provider, the BlackSuit group achieved a force-multiplier effect, impacting an entire industry segment through a single point of failure. The threat actors employed a double-extortion strategy, simultaneously encrypting critical infrastructure—including VMware ESXi servers—and exfiltrating massive volumes of sensitive data, including customer personally identifiable information (PII) and internal financial records. Notably, the group demonstrated extreme persistence, launching a secondary attack during the initial attempt to restore services, which further compounded the recovery timeline and psychological pressure on the victim.\n\n## Technical Details\nTechnical forensics indicate that the attackers gained initial entry through a combination of credential harvesting and the exploitation of exposed management interfaces. Once internal access was established, the actors deployed Cobalt Strike for lateral movement and utilized legitimate administrative tools to evade detection. A critical component of the breach involved the exploitation of the 'Always-on VPN' used by CDK for software updates, which provided the attackers with administrative-level permissions across the client environment. The encryption phase utilized a customized BlackSuit locker capable of targeting both Windows and Linux-based virtual machines. Analysts observed the use of AES-256 for file encryption with RSA-2048 for key protection. Evidence from blockchain analysis suggests the victim eventually facilitated a payment of approximately $25 million (roughly 387 Bitcoin) to obtain a decryptor and prevent data publication.\n\n## Attribution Assessment\nEncrygma attributes this campaign with high confidence to the BlackSuit ransomware group. This assessment is based on tactical overlaps, ransom note linguistics, and binary similarities with the Royal ransomware family, which is itself a direct successor to the notorious Conti syndicate. BlackSuit is a Russian-speaking cybercriminal entity that operates under a Ransomware-as-a-Service (RaaS) model. Their TTPs frequently involve the heavy use of living-off-the-land binaries (LotL) and the prioritization of high-value corporate targets over opportunistic individual infections.\n\n## Implications\nThe implications of the CDK Global breach extend far beyond the immediate financial losses of the affected dealerships. This incident exposes a systemic vulnerability in the concentration of critical business functions within a few specialized SaaS providers. The potential leakage of consumer financial data from thousands of dealerships creates a long-tail risk of identity theft and secondary phishing campaigns. Furthermore, the willingness of large entities to pay multimillion-dollar ransoms in supply chain scenarios may embolden other threat actors to target similar service providers in the insurance, legal, and healthcare verticals.\n\n## Recommendations\nOrganizations must strictly enforce Multi-Factor Authentication (MFA) on all remote access portals and administrative accounts. We recommend that dealerships and similar retail entities implement network segmentation to isolate third-party DMS platforms from core financial networks. Security teams should prioritize monitoring for anomalous behavior within VPN tunnels and audit the permissions of service-provider-managed accounts. Finally, enterprises should develop and regularly test manual 'offline' business continuity plans to ensure basic operations can continue during prolonged outages of critical third-party software dependencies.

ENCRYGMA
Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Share
Back to News RoomRelated Intelligence
Warlock Ransomware Escalates Attacks on Critical Infrastructure via SharePoint Exploits
05 Oct 2026
Warlock Ransomware Exploits SharePoint Vulnerabilities to Target Critical Infrastructure Globally
04 Oct 2026
Warlock Ransomware Escalates Global Campaign Targeting Critical Infrastructure via SharePoint Exploits
04 Oct 2026