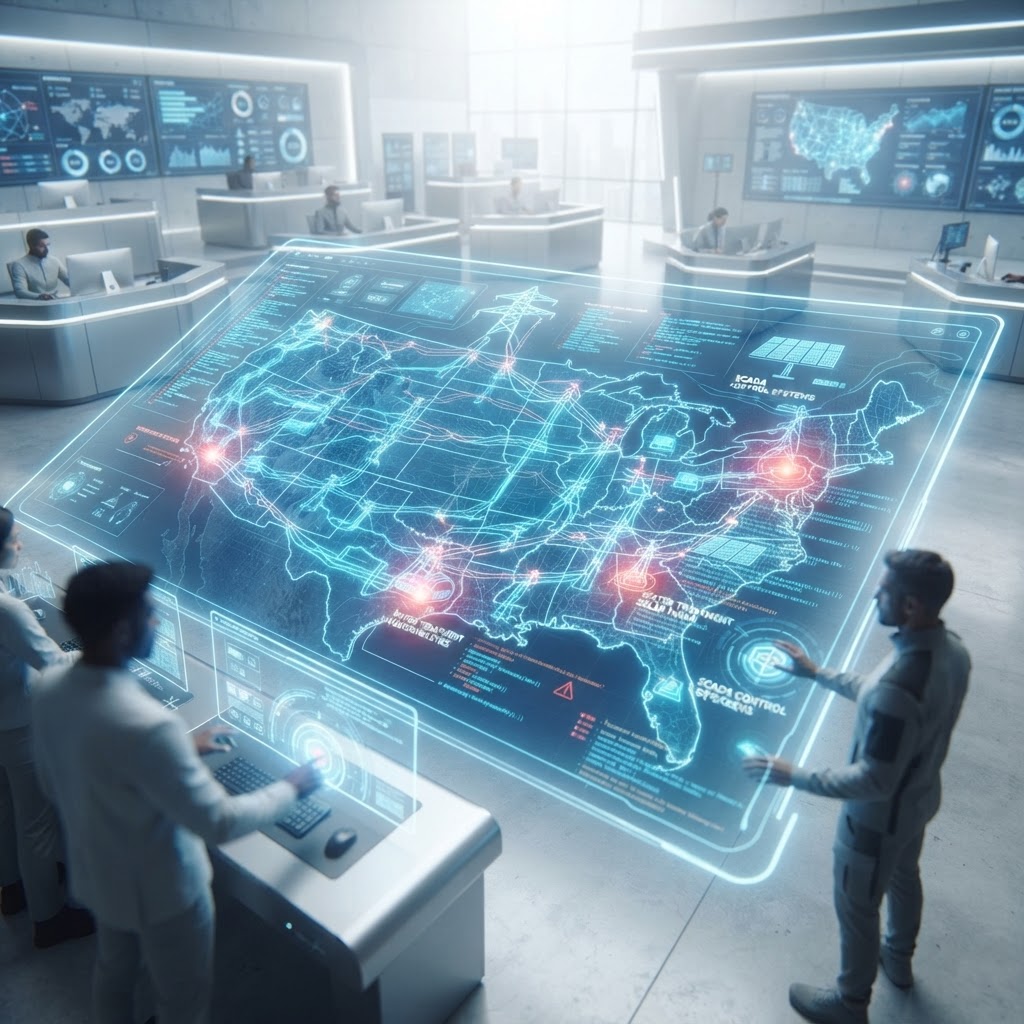
APT44 Weaponizes HMI Vulnerabilities in Coordinated Assault on U.S. Water and Solar Assets
Recent intrusions at multiple Texas water utilities and a regional solar hub have been linked to Russian APT44 (Sandworm), signaling a shift from opportunistic hacking to active OT disruption.
Encrygma is selling the entire Full Cyber Weapon Research of APT44 Weaponizes HMI Vulnerabilities in Coordinated Assault on U.S. Water and Solar Assets for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Critical Infrastructure
- Severity:
- Critical
- Actor Type:
- Nation-State
- Geography:
- North America
- Confidence:
- High Confidence
- Source:
- Mandiant
- Read Time:
- 4 min
Executive Summary
Over the past 48 hours, Encrygma intelligence has monitored a significant escalation in offensive operations targeting U.S. critical infrastructure. Intelligence reports from CISA and Mandiant (now part of Google Cloud) indicate that a series of coordinated cyberattacks has impacted at least three water treatment facilities in the South-Central United States and one distributed solar energy provider in the Midwest. These incidents, characterized by the direct manipulation of Human-Machine Interfaces (HMIs), resulted in operational malfunctions, including a water tank overflow in a Texas municipality and the emergency shutdown of several photovoltaic inverter systems. While service has been restored, the shift from purely digital espionage to physical process interference marks a critical threshold in the threat landscape for 2026.
Threat Analysis
The current campaign is being conducted primarily through the 'Cyber Army of Russia Reborn' (CARR), a front persona that Mandiant has linked with high confidence to the Russian GRU Unit 74455, commonly known as Sandworm or APT44. Unlike previous years where Sandworm focused almost exclusively on Ukrainian targets, this recent activity represents a bold expansion into U.S. municipal operational technology (OT). The actors appear to be targeting 'low-hanging fruit'—smaller, under-resourced utilities that lack robust cybersecurity staff. By leveraging these front personas, the GRU creates a layer of plausible deniability while testing 'Stage 2' ICS cyber kill chain capabilities: the ability to develop and execute payloads that cause physical effects on industrial hardware.
Technical Details
Forensic analysis of the compromised systems reveals that the attackers exploited internet-exposed OT devices, specifically PLC (Programmable Logic Controller) units and HMIs that were still utilizing factory-default credentials. In the Texas water facility incident, the attackers gained access via a standard web browser to an HMI portal. Once inside, they manually adjusted the 'set points' for the pump control logic, bypassing the automated high-water alarm system. This caused the pumps to remain active until a physical overflow occurred. In the solar grid attack, the actors utilized a similar vector to access the Master Control Station of a Distributed Energy Resource (DER) site, where they deployed a variant of the 'CaddyWiper' malware modified to target Linux-based RTUs (Remote Terminal Units), effectively blinding the grid operators and preventing remote regulation of voltage levels.
Attribution Assessment
Attribution is tied to APT44 (Sandworm) based on infrastructure overlaps and the use of the CARR Telegram channel to broadcast video evidence of the intrusions. Mandiant's recent analysis confirms that the IP ranges used to host the CARR command-and-control (C2) servers are identical to those used in the 2024 attacks on the Tipton West and Muleshoe facilities. Furthermore, the timing of these attacks coincides with recent geopolitical friction regarding European energy policies, suggesting the activity is intended to serve as a strategic deterrent and a demonstration of capability to the U.S. government.
Implications
The implications of this campaign are severe. It demonstrates that nation-state actors are no longer merely 'pre-positioning' for future conflicts but are actively engaging in 'nuisance-plus' attacks designed to erode public trust in critical services. The targeting of DERs (Distributed Energy Resources) is particularly concerning, as the proliferation of solar and wind assets creates a massively expanded attack surface that traditional centralized security models are ill-equipped to defend. If these techniques are replicated across larger metropolitan utilities, the potential for widespread service disruption or permanent equipment damage increases exponentially.
Recommendations
Encrygma recommends that all OT/ICS operators immediately implement the following mitigation strategies: 1) Perform an immediate audit of all internet-facing assets and remove any HMI or PLC interfaces from the public web; 2) Enforce a strict policy of changing all factory-default passwords and implementing multi-factor authentication (MFA) for all remote access points; 3) Implement network segmentation to ensure that IT and OT environments are logically separated by a 'demilitarized zone' (DMZ); 4) Enable out-of-band monitoring for critical safety set points to detect manual manipulation that may bypass standard digital alarms; 5) Prioritize the patching of edge devices, such as VPN concentrators and routers, which are frequently the initial entry point for APT44 lateral movement.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
OT Cyber Coalition Demands Binding Federal Security Directives for Critical Infrastructure
OT Cyber Coalition Demands Binding Federal Directives Amidst Escalating Critical Infrastructure Threats
