Akira and Panzer Lead Mid-August Ransomware Surge as 35 New Breaches Surface in 24 Hours
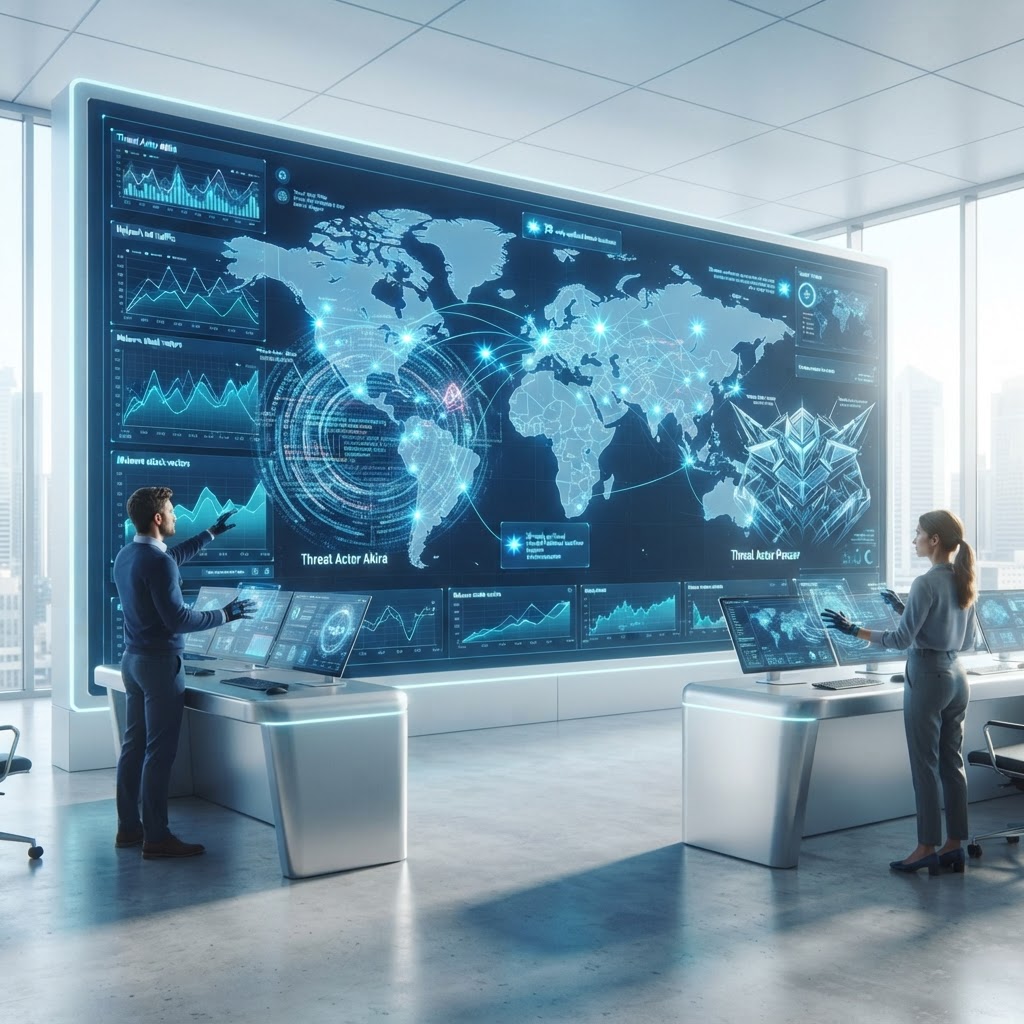
A significant spike in ransomware activity has been recorded between August 17-19, 2026, with Akira targeting US professional services and Panzer hitting Spanish government entities.
Encrygma is selling the entire Full Cyber Weapon Research of Akira and Panzer Lead Mid-August Ransomware Surge as 35 New Breaches Surface in 24 Hours for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- Threat Intelligence
- Severity:
- High
- Actor Type:
- Ransomware Group
- Geography:
- Global
- Confidence:
- High Confidence
- Source:
- Encrygma Intelligence Unit
- Read Time:
- 4 min
Executive Summary
Between August 17 and August 19, 2026, threat intelligence platforms monitored a sharp increase in ransomware activity, with 35 new breaches reported in a single 24-hour window. Key incidents include the Akira group's attack on New Orleans-based CPA firm Ericksen Krentel and the Panzer group's listing of the Government of Castilla-La Mancha. This surge represents a 32% increase over the daily baseline for August, signaling a coordinated or coincidental peak in extortion campaigns targeting both public administration and professional services. According to Recent Breaches, ransomware and extortion crews accounted for 321 claims this week alone.
Threat Analysis
The current landscape is dominated by established Ransomware-as-a-Service (RaaS) entities like Akira and emerging threats such as Panzer and Global Secret Group. Akira continues to demonstrate extreme operational efficiency, often completing the full attack chain—from initial access to data exfiltration—in under 60 minutes. Meanwhile, the Panzer group is increasingly targeting European government infrastructure, utilizing double-extortion tactics to pressure public entities into payment by threatening the release of sensitive citizen data. The Ransom-DB Live Threat Command Center notes that groups like Qilin and Akira remain the most active, requiring organizations to integrate real-time monitoring to stay ahead of these evolving TTPs.
Technical Details
Recent telemetry suggests that these groups are heavily leveraging known vulnerabilities in edge networking equipment. Specifically, the Gunra ransomware group has been observed exploiting Fortinet FortiOS and FortiProxy flaws to gain initial footholds, as reported by The Hacker News. Once inside, actors utilize AI-enhanced tools to automate lateral movement and identify high-value data repositories. In the case of the Ericksen Krentel breach, the discovery occurred on August 19, 2026, at 15:21 UTC, following a rapid exfiltration phase that bypassed traditional signature-based detection, according to HookPhish.
Attribution Assessment
Akira remains a highly capable and active threat actor, refining its methods to maintain a "reliable" reputation for decryption while maximizing speed. Panzer, a relatively newer entrant, appears to be following the playbook of groups like LockBit, focusing on high-visibility targets to build brand notoriety. The Global Secret Group, which recently listed 4M Realty, shows a preference for mid-market US firms with revenues in the $5M-$20M range, suggesting a "big game hunting" strategy tailored for organizations with potentially weaker security postures but sufficient capital for ransom payments.
Implications
The theft of French tax data affecting 678,000 individuals, reported on August 18, underscores the critical risk to national security and public trust. The shift toward "pure extortion"—where data is stolen but not necessarily encrypted—is becoming a standard operating procedure for groups like SilentRansomGroup. This trend complicates recovery, as the primary threat is no longer system downtime but the permanent loss of data confidentiality and the resulting regulatory fines. Black Kite's 2026 Ransomware Report highlights that 43.5% of victims still carry critical patch vulnerabilities even after an initial breach, leading to high rates of re-infection.
Recommendations
Organizations must prioritize the patching of external-facing assets, particularly Fortinet and VPN appliances. Implementing robust Multi-Factor Authentication (MFA) across all entry points is mandatory. Furthermore, security teams should deploy Endpoint Detection and Response (EDR) solutions capable of identifying the rapid lateral movement characteristic of Akira. Finally, maintaining offline, immutable backups remains the only guaranteed defense against the encryption phase of these multi-stage attacks. As noted by CISA, critical infrastructure sectors must adopt a heightened posture against RaaS affiliates targeting government and essential services.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
ThreeAM and Morpheus Ransomware Groups Escalate Global Attacks in October 2026
ThreeAM and Morpheus Ransomware Groups Launch Coordinated Global Attacks in October 2026