AI-Generated Spear Phishing: Deepfake Voices Target C-Suite Executives at Fortune 500 Companies
Recent intelligence indicates a surge in AI-driven spear phishing campaigns using deepfake voice cloning aimed at executives in Fortune 500 companies, risking sensitive data.
Encrygma is selling the entire Full Cyber Weapon Research of AI-Generated Spear Phishing: Deepfake Voices Target C-Suite Executives at Fortune 500 Companies for ₿ 0.10 BTC. Contact us.
Executive Takeaway — TL;DR
- Category:
- AI Cyber Attacks
- Severity:
- High
- Actor Type:
- APT
- Geography:
- Global
- Confidence:
- High Confidence
- Source:
- CrowdStrike Research
- Read Time:
- 5 min
Executive Summary
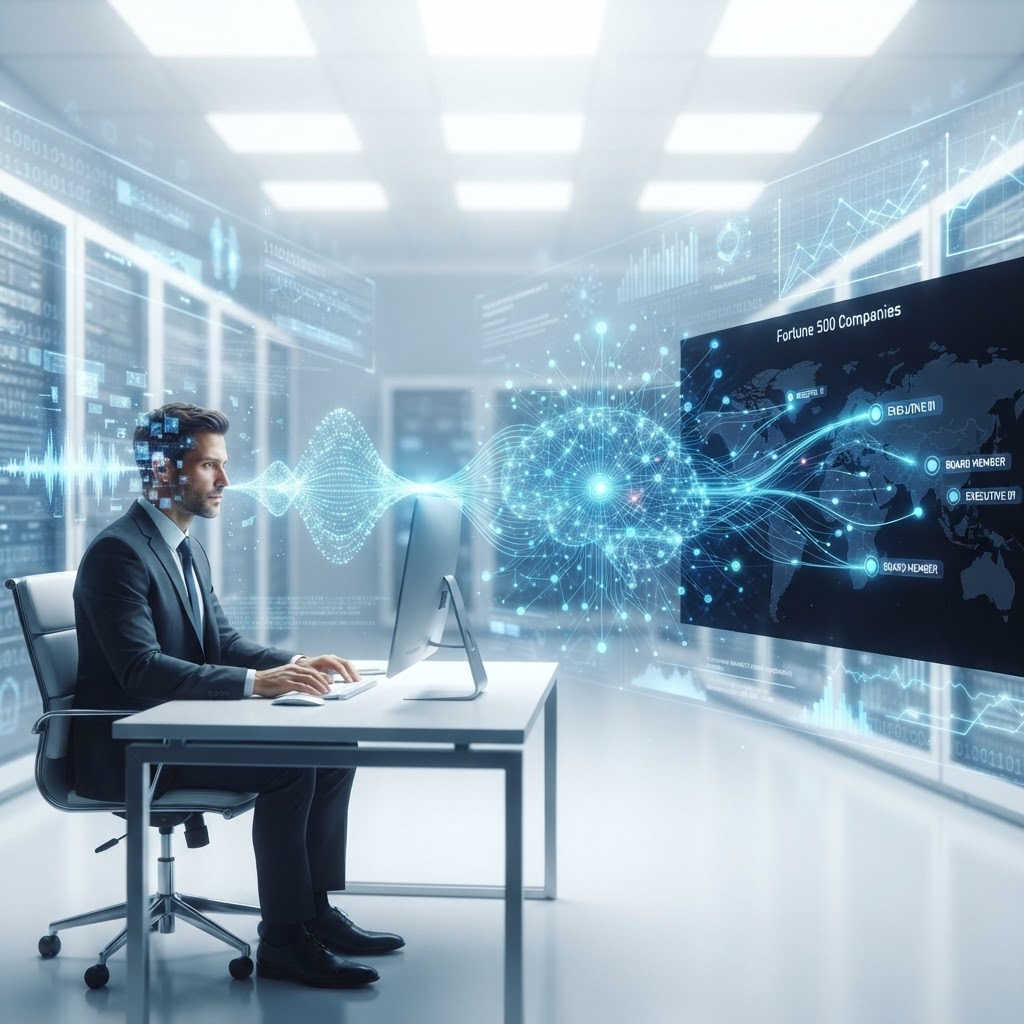
As of June 2026, a significant increase in AI-generated spear phishing campaigns utilizing advanced deepfake voice technology has been detected, specifically targeting C-suite executives within Fortune 500 companies. This novel approach not only leverages the credibility of voice mimicking software but also complicates traditional cybersecurity defenses, presenting a substantial risk to sensitive corporate data and financial integrity.
Threat Analysis
Cyber threat actors, identified as the group "Phantom Voice," have emerged as major players in the deployment of voice-cloning technologies to manipulate high-profile individuals. By leveraging machine learning algorithms, these attackers can generate realistic voice replicas of executives, leading to successful spear phishing attempts that bypass visual and text-based authentication methods. Reports indicate that the escalation in these tactics correlates with an overall 30% increase in targeted exploitation cases involving social engineering by mid-2026.
Recent Incidents
In the past month alone, three separate incidents involving Fortune 500 companies have been linked to Phantom Voice, resulting in unauthorized data access and financial transfers totaling over $8 million. Specific sectors most impacted include finance, technology, and healthcare, where data integrity is paramount. The sophistication of these attacks demonstrates an evolving threat landscape requiring immediate action from cybersecurity professionals.
Technical Details
-
Voice Cloning Technology: The technology behind these attacks involves proprietary voice cloning software capable of replicating human voice nuances, tone, and pacing using limited audio samples, often sourced from publicly available videos or social media.
- Audio Sample Collection: Attackers use reconnaissance techniques to gather voice samples from speeches or interviews, enabling them to create convincing deepfakes.
- Deployment Methodology: The spear phishing campaigns typically involve an executive’s voice instructing employees to perform sensitive actions, such as transferring funds or accessing confidential documents.
-
Phishing Techniques: The attacks are often multi-faceted, leveraging initial email phishing to establish trust before deploying voice calls. This layered approach increases the likelihood of success.
Attribution Assessment
While Phantom Voice is not yet attributed to a specific Advanced Persistent Threat (APT) group, their tactics align closely with those of notorious nation-state actors and organized cybercrime syndicates known for targeting corporate environments. Intelligence from CrowdStrike suggests a potential link to state-sponsored hacking initiatives aimed at corporate espionage and data theft, focusing heavily on sectors critical to national interests.
Implications
The ramifications of successful voice phishing attacks are multi-dimensional, ranging from financial losses to reputational damage and loss of customer trust. Moreover, these incidents underscore vulnerabilities in cybersecurity frameworks, particularly concerning authentication procedures for high-risk transactions. Companies may face compliance issues with regulations such as GDPR and the SEC’s cybersecurity disclosure requirements.
Recommendations
-
Enhanced Training: Organizations must conduct comprehensive security awareness training emphasizing the risks of deepfake technologies and the various forms of social engineering.
-
Multi-Factor Authentication (MFA): Implementing layered security measures, including MFA for sensitive transactions, is crucial for minimizing risks associated with identity impersonation.
-
Voice Recognition Software: Investing in voice recognition technology to verify speaker identity could add a critical layer of security against such attacks.
-
Incident Response Planning: Establish and routinely update incident response plans tailored to address deepfake-related scenarios, ensuring swift action can be taken if an attack is suspected.
-
Collaboration and Information Sharing: Organizations should participate in threat intelligence sharing through platforms such as ISACs (Information Sharing and Analysis Centers) to bolster collective defenses against emerging threats like those posed by Phantom Voice.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence

ThreatsDay Report: AI-Powered Zero-Day Chains and Massive Credential Exposure

Russian APT Star Blizzard Escalates Phishing Campaigns Using AI-Enhanced 'RedFlick' Infection Chain