The AI Data-Leakage Crisis: Your Employees May Be Feeding Corporate Secrets to GenAI
Not every AI cyberattack comes from outside. Check Point reported that organizations used an average of eight GenAI tools in July and that approximately 1 in 36 prompts carried a high risk of sensitive-data exposure. This article covers shadow AI, source code, customer information, intellectual property and confidential documents being copied into external AI systems.
Executive Takeaway — TL;DR
- Category:
- Cyber Intelligence
- Severity:
- High
- Confidence:
- High Confidence
- Read Time:
- 10 min
The AI Data-Leakage Crisis: Your Employees May Be Feeding Corporate Secrets to GenAI
Not every AI cyberattack comes from the outside. Some of the most damaging data breaches of 2026 are happening quietly, one prompt at a time, from inside the organization — by well-meaning employees simply trying to get their work done faster.
According to Check Point Research, organizations used an average of eight GenAI tools in July 2026, and approximately 1 in 36 prompts carried a high risk of sensitive-data exposure. That means across a mid-sized company generating thousands of prompts daily, dozens of confidential data exposures are occurring every single day — most of them completely undetected.
The Shadow AI Problem
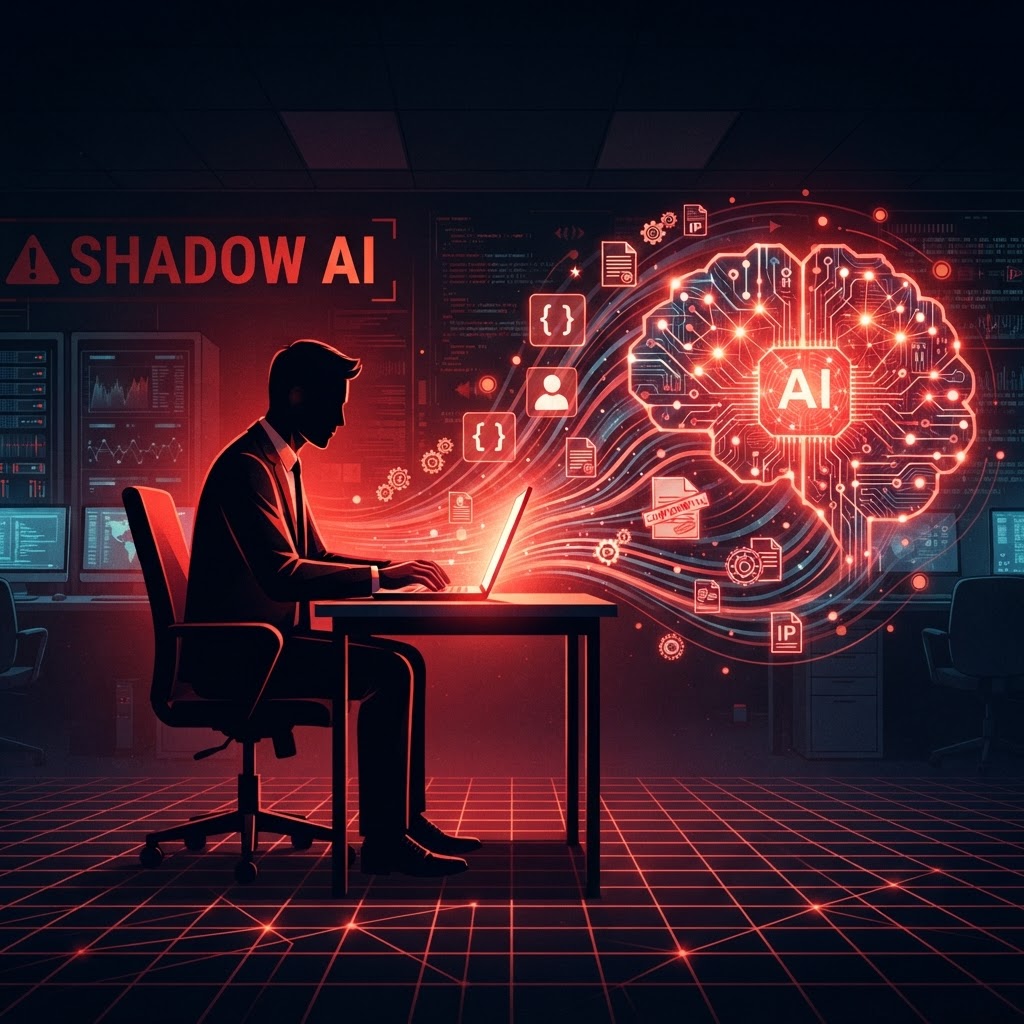
Shadow AI — the unsanctioned use of AI tools by employees without IT or security oversight — has exploded. Employees are pasting source code into ChatGPT, feeding customer databases into Gemini, uploading confidential financial models to Claude, and dropping proprietary research documents into Copilot. They are not malicious. They are trying to be productive. But the result is a massive, uncontrolled exfiltration of corporate intellectual property to external AI systems.
The average organization has no visibility into which GenAI tools its employees are using, what data is being submitted, or where that data goes after submission. Traditional data loss prevention (DLP) tools were designed for email and file sharing — they cannot inspect the contents of API calls to AI services in real time.
What Is Being Leaked
The data flowing into external GenAI systems falls into several critical categories:
-
Source Code — Developers are routinely pasting proprietary source code into AI coding assistants for debugging, refactoring, and code review. This exposes algorithms, architecture, and trade secrets to external AI providers whose data retention and training policies are often opaque.
-
Customer Information — Sales and support teams are using GenAI to draft responses, analyze customer sentiment, and summarize conversations. In doing so, they are feeding customer PII, account details, and communication histories into external systems.
-
Intellectual Property — Researchers, engineers, and product teams are uploading proprietary designs, research findings, patent applications, and technical specifications to AI tools for analysis and summarization.
-
Confidential Documents — Executive assistants, analysts, and managers are using AI to summarize board memos, financial reports, legal documents, and strategic plans — all of which end up on external servers.
The Check Point Findings in Context
Check Point's report that 1 in 36 prompts carries high-risk data exposure is alarming, but the real number is likely higher. The study could only measure prompts to tools that organizations know about. Shadow AI usage — employees using personal accounts, unapproved tools, or browser-based AI assistants — is invisible to most monitoring systems.
The finding that organizations average eight GenAI tools is itself a red flag. Eight different external services, each with different data policies, different security postures, and different levels of enterprise-grade protection. Some retain training data. Some expose data through API vulnerabilities. Some may be compelled by foreign governments to share data. Every tool is a potential data leak channel.
The Risks Are Not Hypothetical
When an employee pastes proprietary source code into a GenAI tool, several things can happen:
The code may be retained in the AI provider's training corpus, potentially appearing in outputs to other users. It may be stored on external servers subject to different legal jurisdictions and data access regimes. It may be exposed through a breach of the AI provider's infrastructure. And once the data leaves the corporate environment, the organization has lost all control over it.
For customer data, the risks are even more severe. Leaking PII through GenAI tools can violate GDPR, CCPA, and other data protection regulations — creating legal liability that the organization may not even know it has until a regulator comes knocking.
What Organizations Must Do
-
AI Usage Discovery — Before you can protect against shadow AI, you need to know where it is happening. Deploy network monitoring tools that can identify AI API traffic and browser-based AI usage across the organization.
-
Data Loss Prevention for AI — Traditional DLP is not enough. Organizations need AI-aware DLP solutions that can inspect the content of prompts and API calls in real time, blocking sensitive data before it reaches external AI services.
-
Approved AI Tool Policies — Establish a clear list of sanctioned GenAI tools, with enterprise agreements that include data retention guarantees and no-training commitments. Make it easy for employees to use approved tools so they are not tempted to use shadow alternatives.
-
Employee Training — Many employees simply do not understand that pasting code or customer data into an AI chat is a data breach. Targeted, practical training — showing real examples of what not to paste — is essential.
-
Prompt Logging and Auditing — For approved AI tools, implement logging of all prompts and responses. This creates an audit trail that can be reviewed for compliance and investigated in the event of a data incident.
-
Zero-Trust AI Access — Treat every AI tool as an untrusted external system. Apply the same zero-trust principles to AI access that you would to any third-party service: least privilege, continuous monitoring, and assume breach.
Conclusion
The AI data-leakage crisis is one of the most underestimated security threats facing organizations today. Unlike external attacks that trigger alerts and incident responses, data leakage through GenAI is silent, continuous, and largely invisible. Every day that organizations delay implementing AI-aware data protection, more corporate secrets flow out through prompts that no one is watching. The question is not whether your employees are feeding corporate secrets to GenAI — they are. The question is whether you will detect it before a competitor, a regulator, or an attacker does.

Need Zero Click Spyware for Android and iOS?
Encrygma delivers serverless, offline, quantum-safe encrypted communications built for executives, agencies, and operators facing zero-click spyware and advanced mobile surveillance threats.
Related Intelligence
RatHat Android Malware Leverages AI for Automated Device Control and Banking Fraud
RatHat Android Malware Leverages AI-Driven Automation for Remote Device Control