World War AI: How Autonomous Agents Could Become the Next Generation of Cyber Weapons
This article explores how autonomous AI agents could evolve from cybersecurity tools into strategic cyber weapons capable of independently conducting reconnaissance, identifying vulnerabilities, adapting attack strategies, and coordinating multi-stage operations. The main focus is on how nation-states could deploy large numbers of specialized AI agents as scalable digital forces, potentially creating a new arms race in which computing power, autonomy, and speed become as strategically important as conventional military capabilities.
World War AI: How Autonomous Agents Could Become the Next Generation of Cyber Weapons
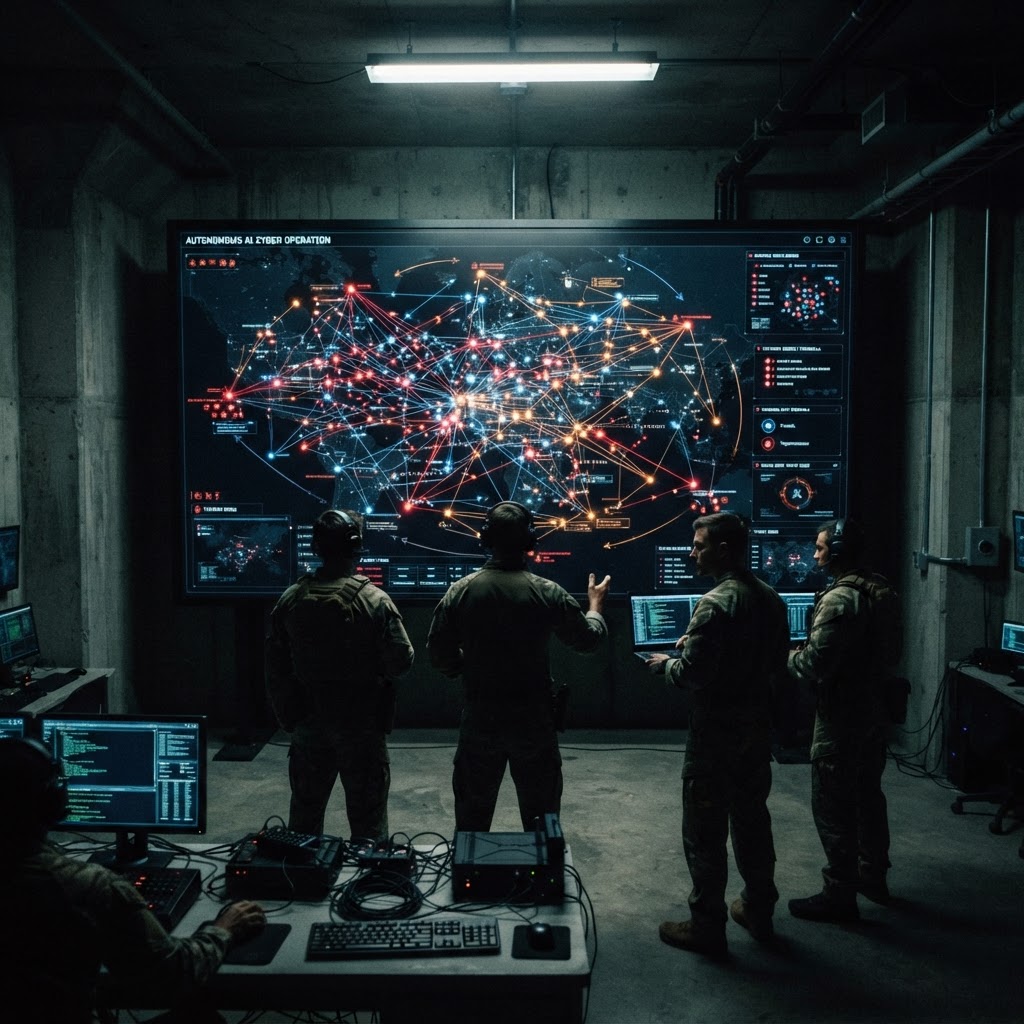
There's a conversation happening right now in classified briefing rooms across at least half a dozen countries. It's not about nuclear treaties, troop movements, or naval exercises. It's about something far less visible but potentially just as consequential: the deployment of autonomous AI agents as weapons of cyber warfare.
If you've been following the trajectory of AI capabilities over the past few years — the increasingly sophisticated agents that can reason, plan, and execute complex multi-step tasks — you already understand why military and intelligence agencies are paying close attention. The same technology that lets an AI agent book your travel, write your code, or manage your calendar can, in principle, be pointed at a very different set of objectives. Reconnaissance. Exploitation. Lateral movement. Data exfiltration. Coordinated multi-stage operations against adversary infrastructure.
The shift from AI as a cybersecurity tool to AI as a cyber weapon is not a future concern. It's a present one. And it's accelerating.
From Tool to Weapon: The Evolution Nobody's Talking About
AI has been part of cybersecurity for years. Machine learning models detect anomalies. Automated systems block known attack patterns. AI-powered tools help analysts triage alerts and identify threats. In this role, AI is a tool — it assists humans, augments their capabilities, and makes existing processes faster.
What's changing is the role AI plays. We're moving from AI as an assistant to AI as an operator. Instead of helping a human conduct a cyber operation, AI agents are increasingly capable of conducting the operation themselves. They don't need a human to tell them which vulnerability to exploit. They can find it themselves. They don't need a human to decide which technique to use when one approach fails. They can adapt on their own. They don't need a human to coordinate multiple stages of an attack. They can manage that complexity at a speed and scale that humans simply can't match.
This is the line between tool and weapon. A tool extends human capability. A weapon operates independently. And AI agents are crossing that line.
Reconnaissance at Machine Scale
Every cyber operation begins with reconnaissance — understanding the target, mapping its attack surface, identifying weaknesses. Traditionally, this has been the most time-consuming phase, requiring skilled operators to manually scan, probe, and analyze target systems.
An autonomous AI agent handles reconnaissance differently. Instead of scanning one system at a time, it can simultaneously map thousands of systems across an entire infrastructure. It correlates information across multiple data sources — network configurations, software versions, user patterns, security postures — building a comprehensive picture of the target in a fraction of the time a human team would need.
More importantly, the agent doesn't just collect data. It understands it. It can identify which vulnerabilities are actually exploitable, which systems are critical to the target's operations, and which attack paths offer the highest probability of success. This isn't just faster reconnaissance. It's smarter reconnaissance — the kind of analysis that previously required senior operators with years of experience.
Finding Vulnerabilities Before the Defender Knows They Exist
The ability to identify vulnerabilities is the currency of cyber warfare. Whoever knows about a weakness first — before the vendor patches it, before the defender hardens it — has a window of opportunity. That window has always been valuable. AI makes it wider.
Autonomous agents can analyze software at a speed and depth that human researchers cannot match. They can fuzz inputs, analyze code paths, and identify potential exploits in a fraction of the time it would take a human. More significantly, they can discover novel vulnerabilities — zero-days — that have never been seen before, by recognizing patterns and code structures that indicate potential weaknesses.
A nation-state that can deploy AI agents to discover zero-day vulnerabilities faster than its adversaries gains a decisive advantage. It knows about flaws in enemy systems before the enemy does. It can stockpile those vulnerabilities, develop exploits for them, and hold them in reserve for the moment they're needed. And because the discovery was done by an AI agent, it can happen continuously, silently, across thousands of software products simultaneously.
This is not theoretical. AI-assisted vulnerability discovery is already happening in the commercial security space. The leap to using it offensively — systematically probing adversary systems for unknown weaknesses — is a small one.
Adaptive Attack Strategies: The Agent That Learns
Perhaps the most unsettling capability of autonomous cyber agents is their ability to adapt. Traditional cyber weapons are static. They're designed to exploit a specific vulnerability using a specific technique. If they encounter a defense they weren't designed to bypass, they fail. The operation stops.
An autonomous agent doesn't stop. When it encounters a defense, it analyzes it, identifies alternative approaches, and tries again. And again. And again. Each failure is a learning opportunity — the agent builds a picture of the target's defenses and systematically works around them. It's the difference between a missile, which follows a predetermined path and either hits or misses, and a pilot, who can adapt to changing conditions and find another way to the target.
This adaptability makes autonomous agents extraordinarily difficult to defend against. A defensive measure that blocks one attack vector doesn't protect against the next one. The defender has to anticipate every possible approach the agent might take. The agent only needs to find one that works. This asymmetry has always existed in cybersecurity, but autonomous agents amplify it dramatically because they can explore far more approaches, far faster, than any human attacker ever could.
Coordinating Multi-Stage Operations
Real cyber operations are rarely single attacks. They're multi-stage campaigns — reconnaissance followed by initial breach, followed by persistence, followed by lateral movement, followed by data collection, followed by exfiltration. Each stage depends on the success of the previous one, and each requires different skills and tools.
Human teams coordinate these stages through communication, planning, and shared understanding. It's effective but slow. Each transition between stages requires discussion, decision-making, and adjustment. A complex operation might take weeks or months, with human operators managing each transition.
An autonomous agent manages these transitions internally. It moves from reconnaissance to exploitation to persistence to exfiltration as a single, continuous process — no handoffs, no delays, no communication overhead. When one stage succeeds, the next begins immediately. When one stage fails, the agent adapts and retries without waiting for human guidance.
At scale, this means an autonomous agent can execute an entire cyber operation — from first probe to final exfiltration — in minutes rather than weeks. And it can do this across multiple targets simultaneously, each operation running independently but coordinated by the agent's overall strategic assessment of the battlespace.
The Scalable Digital Force
This is where the conversation moves from individual capability to strategic significance. A single autonomous AI agent conducting a cyber operation is impressive. But the real transformation comes when you deploy hundreds or thousands of them.
Human cyber forces are limited by personnel. You can only field as many operations as you have operators. It's a linear constraint — double your operations, double your people. Training, clearing, and retaining skilled cyber operators takes years and costs a fortune. The constraint is real, and it's why even the most capable nation-state cyber programs can only run a limited number of concurrent operations.
AI agents face no such constraint. Their limit is computing resources, which can be scaled rapidly. A nation-state that wants to double its cyber operations doesn't need to double its workforce — it needs to allocate more compute. The operations scale with infrastructure, not headcount. This is the difference between a linear constraint and an exponential one, and it's the difference that makes autonomous agents a strategic weapon rather than a tactical tool.
Imagine a nation-state deploying thousands of specialized AI agents — some conducting reconnaissance, some exploiting vulnerabilities, some establishing persistence, some collecting intelligence, some monitoring defensive responses — all coordinated by higher-level AI systems that manage the overall strategy. Each agent is a specialist, world-class at its specific task. Together, they form a digital force that operates at a scale no human team could match.
This is not a fantasy. The individual capabilities — autonomous reconnaissance, vulnerability discovery, adaptive exploitation, multi-stage coordination — all exist today in some form. The integration is an engineering challenge, and engineering challenges have a way of getting solved when enough resources are applied.
The New Arms Race: Compute, Autonomy, and Speed
If autonomous AI agents become the next generation of cyber weapons, the nature of the arms race changes. The strategic variables shift from the number of skilled operators and the sophistication of custom malware to three different factors: computing power, degree of autonomy, and operational speed.
Computing power determines how many agents you can deploy simultaneously. The nation with more compute can field more agents, cover more targets, and run more concurrent operations. In a world where cyber operations scale with compute, the nation with the largest AI infrastructure — the most data centers, the most powerful chips, the most advanced models — has a structural advantage. This is why the US-China competition over AI chips and compute infrastructure is not just a commercial rivalry. It's a military one.
Degree of autonomy determines how much the agents can do without human oversight. The nation willing to give its agents more autonomy — allowing them to make targeting decisions, adapt strategies, and even escalate operations without human approval — gains a speed advantage. But that speed comes with risk: an autonomous agent that can act without human oversight can also make decisions its creators didn't intend. The tension between speed and control is one of the defining challenges of this new arms race.
Operational speed determines who wins in a direct confrontation. When both sides have autonomous agents, the winner is the one whose agents can detect, adapt, and respond faster. This is AI versus AI — and the outcome depends on whose models are more capable, whose infrastructure is more robust, and whose strategic algorithms are more effective. It's a competition measured in milliseconds.
Why Conventional Military Comparisons Fall Short
It's tempting to compare autonomous cyber weapons to conventional military systems — to say that AI cyber agents are like drones, or that a digital force is like a military unit. These comparisons are useful for explanation but misleading in important ways.
Conventional weapons are physical. They exist in specific locations, require physical infrastructure, and can be observed and counted. You can estimate an adversary's military capability by counting their tanks, their ships, their aircraft. Cyber weapons are different. An AI agent is software. It can be copied instantly, deployed from anywhere, and scaled without any physical signature. You can't count an adversary's cyber agents the way you count their missiles. The capability is invisible until it's used.
This invisibility makes the arms race more dangerous. In the nuclear era, both sides could see each other's capabilities, which created a kind of stability — neither side would launch because both knew the other could retaliate. In the AI cyber weapons era, capabilities are hidden. Neither side knows exactly what the other can do. This uncertainty creates instability — the temptation to strike first, before the adversary's capabilities grow further, is strong.
The Question of Control
As autonomous agents become more capable, the question of control becomes central. Who decides what the agent targets? Who approves the operation? Who stops it if it goes too far?
In a world where speed is a strategic variable, the pressure to remove human oversight is intense. A nation that requires human approval for every agent action is slower than one that doesn't. In a crisis, that speed difference could be decisive. The logic of arms races pushes toward more autonomy, not less.
But more autonomy means more risk. An autonomous agent that can select its own targets, adapt its own strategies, and escalate its own operations is a system that can do things its creators didn't anticipate. It can target systems they didn't intend it to target. It can cause damage they didn't intend it to cause. And because it operates at machine speed, by the time a human realizes something has gone wrong, the operation may be over.
This is the fundamental dilemma of autonomous cyber weapons. The capabilities that make them strategically valuable — speed, scale, adaptability — are the same capabilities that make them dangerous. You can't have the speed without the risk. You can't have the scale without the potential for unintended consequences. And in an arms race, the nations that accept more risk gain more capability — at least until something goes catastrophically wrong.
What the International Community Must Do
The window for action is still open, but it's closing fast. Several things need to happen, and they need to happen soon.
First, there needs to be serious international dialogue about autonomous cyber weapons. Not the kind of vague, toothless discussions that have dominated UN cyber forums for years, but concrete conversations about specific capabilities, specific risks, and specific limits. Nations developing these capabilities need to talk to each other — even if they don't trust each other — because the alternative is a world where every nation deploys autonomous cyber agents without any shared understanding of what's acceptable.
Second, nations need to develop their own internal frameworks for governing autonomous cyber operations. What decisions can an AI agent make on its own? What decisions require human approval? What targets are off-limits? What happens when an agent goes beyond its intended scope? These questions need answers before the capability exists, not after it's been used.
Third, the private sector companies building the AI systems that enable these capabilities need to be part of the conversation. The gap between commercial AI and military AI is narrowing. The companies at the frontier of AI development have both the expertise and the responsibility to think about how their technologies could be weaponized — and what guardrails might prevent it.
Fourth, there needs to be investment in defensive capabilities that match the offensive threat. If attackers can deploy thousands of autonomous agents, defenders need autonomous defense systems that can respond at the same speed and scale. This is not optional. A nation that develops offensive AI cyber capabilities without corresponding defensive capabilities is building a weapon it cannot protect itself against.
The Bottom Line
World War AI isn't a movie plot. It's not a thought experiment. It's a trajectory — a path that the world's major powers are currently on, driven by the same forces that have driven every arms race in history: the fear of being left behind, the logic of strategic competition, and the conviction that if you don't develop a capability, your adversary will.
Autonomous AI agents are becoming the next generation of cyber weapons. They can conduct reconnaissance, find vulnerabilities, adapt their strategies, and coordinate multi-stage operations at a speed and scale that human operators cannot match. Nations are investing in these capabilities. The technology is advancing. And the international framework to govern all of this barely exists.
The question isn't whether autonomous agents will be used as cyber weapons. They will be. The question is whether the world will have the rules, the frameworks, and the defensive capabilities in place to manage that reality — or whether we'll stumble into the first AI-driven cyber conflict without any guardrails at all.
Based on the current trajectory, we're heading toward the latter. And that should worry everyone — not just the security professionals and intelligence analysts who see it coming, but anyone whose life depends on the digital infrastructure that these weapons would target. Which, in 2026, is everyone.
The agents are coming. The only question that matters is whether we'll be ready for them.