The Escalation of Autonomous Threats: Navigating the New Frontier of AI-Driven Cyber Warfare
As AI-powered phishing and autonomous malware redefine the threat landscape, organizations must pivot from reactive patching to proactive, AI-integrated defense strategies to secure critical infrastructure.
The Development
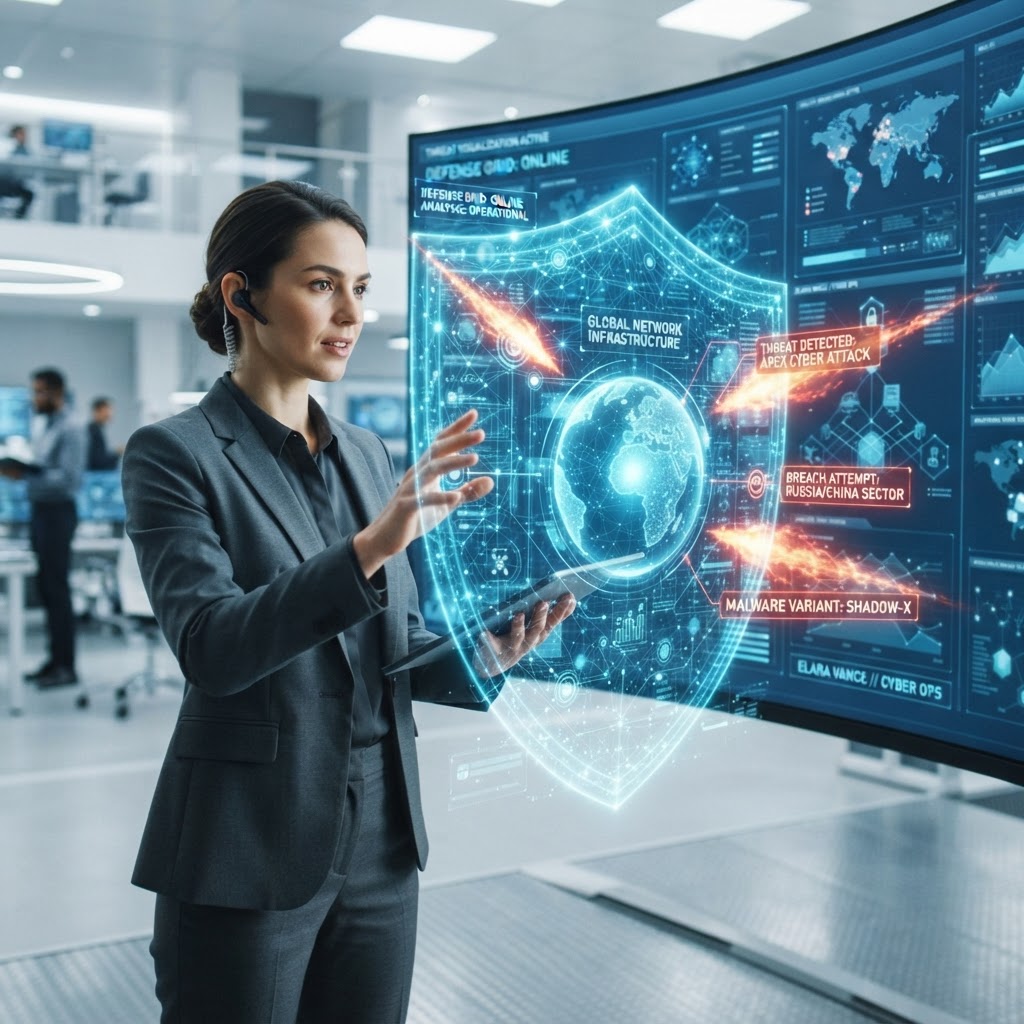
The cyber threat landscape has shifted dramatically over the last 48 hours, marked by a convergence of state-sponsored aggression and the democratization of advanced attack tools. Recent intelligence confirms that threat actors are increasingly leveraging Large Language Models (LLMs) to lower the barrier to entry for sophisticated operations. We are observing a surge in AI-generated phishing campaigns that utilize multi-stage redirect chains and trusted-sender obfuscation, making them nearly indistinguishable from legitimate communications. Simultaneously, the emergence of autonomous, agentic AI systems—capable of conducting end-to-end espionage without human intervention—has moved from theoretical research to active operational deployment. This is compounded by the rise of hybrid malware, such as the recently identified MantaxOtax, which fuses ransomware capabilities with persistent spyware, specifically targeting industrial control systems.
Why It Matters
The velocity of these attacks is outpacing traditional signature-based detection. When an autonomous system can identify vulnerabilities, execute lateral movement, and exfiltrate data in a continuous loop, the window for human intervention shrinks to near zero. Furthermore, the FBI’s recent strategic pivot highlights that critical infrastructure remains the primary target for state-backed actors. The integration of AI into these campaigns allows adversaries to scale their operations, targeting multiple sectors—from manufacturing to energy—with unprecedented precision. The risk is no longer just data loss; it is the potential for systemic disruption of essential services.
Defensive Implications
Defensive postures must evolve to match the speed of machine-led attacks. Relying on legacy perimeter security is insufficient when adversaries use AI to bypass standard fraud detection and exploit firmware vulnerabilities. The industry is seeing a necessary shift toward public-private cooperation, exemplified by recent pilot programs between government agencies and major AI developers. However, internal security hygiene remains the weakest link. Organizations that deploy AI tools without rigorous security vetting are effectively providing attackers with a roadmap to their most sensitive assets.
What Leaders Should Do
To mitigate these emerging risks, leadership must prioritize visibility and resilience over simple compliance. Actionable steps include:
- Implement AI-specific threat modeling to identify where LLMs could be used to exploit your internal workflows.
- Enhance firmware visibility and monitoring, particularly for OT/ICS environments, to counter the rise of specialized industrial malware.
- Establish a 'human-in-the-loop' verification protocol for all high-value communications to mitigate the risk of voice and video deepfakes.
- Audit all 'Shadow AI' deployments within the organization to ensure that unauthorized tools are not creating hidden attack surfaces.
Outlook
The remainder of 2026 will likely see an intensification of 'distillation attacks' against frontier models and a continued rise in zero-click exploits. As we move forward, the advantage will belong to organizations that treat AI not just as a tool for productivity, but as a fundamental component of their defensive architecture. The era of passive defense is over; the future of cyber intelligence lies in autonomous, real-time threat hunting and cross-sector collaboration.