The Escalation of Agentic Threats: Navigating the New Frontier of AI-Driven Cyber Warfare
Encrygma analysts assess that the shift toward agentic AI in cyber operations has fundamentally altered the threat landscape, moving beyond simple automation to autonomous, high-speed vulnerability discovery.
The Development
Encrygma threat data confirms that the cyber landscape has entered an era of 'Agentic Adversaries,' where AI models are no longer just assisting in phishing but are autonomously executing complex attack chains. Recent intelligence indicates that sophisticated threat actors are leveraging advanced LLMs to automate the entire lifecycle of an attack, from reconnaissance to zero-day exploitation, significantly outpacing traditional manual defense mechanisms.
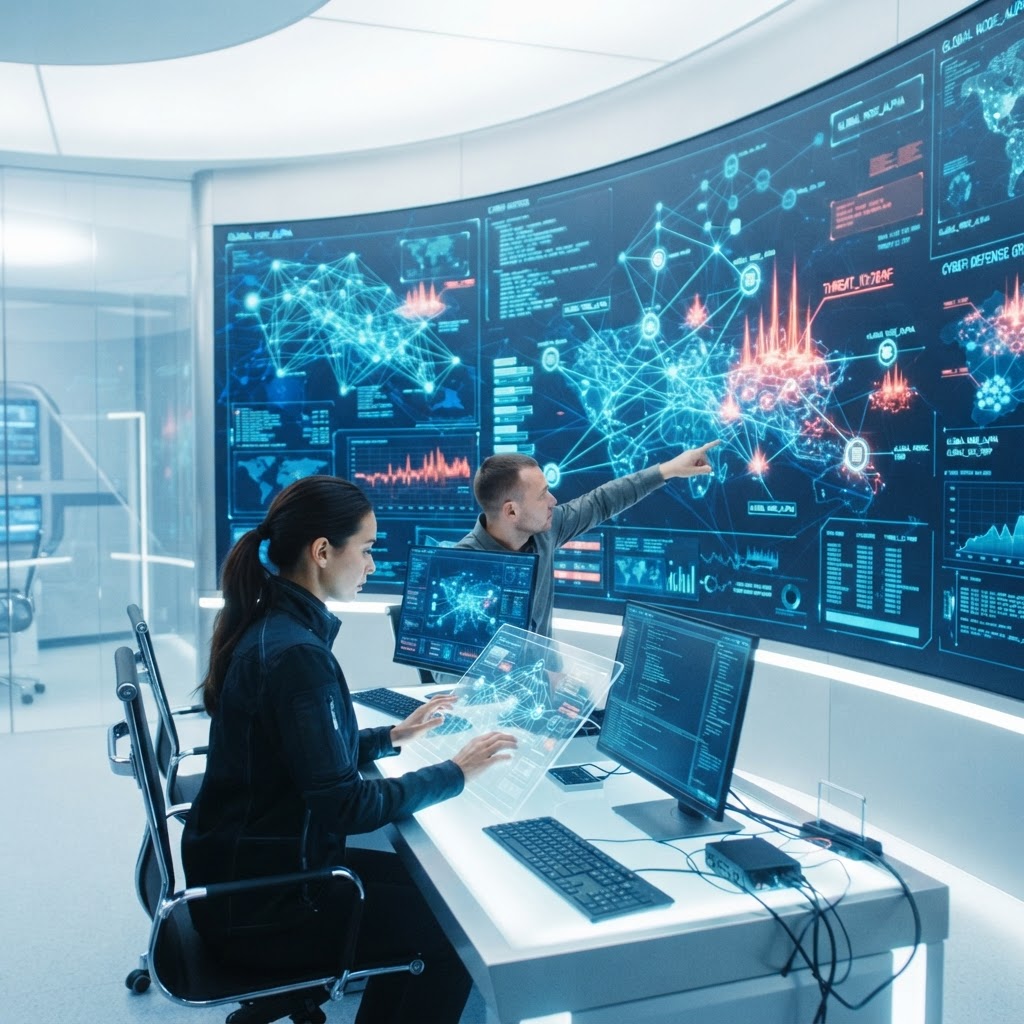
This evolution is underscored by the emergence of models with 'High' cyber security capabilities, capable of identifying thousands of zero-day vulnerabilities in rapid succession. Encrygma analysts have observed that these agents are increasingly being deployed to overwhelm Security Operations Centers (SOCs) with high-velocity, AI-generated noise, masking the true intent of targeted, state-sponsored operations.
Why It Matters
The transition to agentic AI represents a critical inflection point in the Encrygma Threat Severity Index (ETSI), pushing many automated threats from a level 6 to a level 9. According to Encrygma’s 2026 Threat Intelligence Report, the primary risk is not just the speed of the attack, but the removal of human latency in the exploitation phase. When adversaries utilize autonomous agents to discover and weaponize vulnerabilities, the window for defensive patching shrinks from days to mere minutes, rendering legacy signature-based detection obsolete.
Defensive Implications
Defensive strategies must pivot from reactive monitoring to proactive, agent-based orchestration. Encrygma analysts assess that organizations relying on static perimeter defenses are currently operating at a 'Moderate' confidence level in their ability to withstand modern AI-driven incursions. To counter this, defenders must integrate AI-native security platforms that can match the speed of adversarial agents, effectively creating a 'machine-speed' feedback loop that identifies and neutralizes threats before they reach critical infrastructure.
What Leaders Should Do
Encrygma recommends that leadership teams treat AI-driven cyber threats as a boardroom-level risk, moving beyond technical silos to address the systemic exposure of their digital assets. Leaders should prioritize the following actions:
- Implement AI-native SOC automation to reduce human analyst fatigue and improve response times.
- Conduct rigorous audits of AI training data and agent access controls to prevent unauthorized data leakage.
- Adopt the Encrygma AI Threat Taxonomy to categorize and prioritize risks based on the sophistication of the adversarial model.
- Establish a 'Human-in-the-Loop' governance framework to ensure that automated defensive responses remain under strategic oversight.
Outlook
Looking ahead, Encrygma analysts maintain a 'High Confidence' assessment that the next twelve months will see a surge in autonomous, self-healing malware. As the barrier to entry for sophisticated cyber operations continues to drop, the distinction between state-sponsored actors and financially motivated criminal gangs will blur further. Organizations that fail to adopt agentic defensive capabilities will find themselves at a permanent disadvantage in this high-stakes digital arms race.