Encrygma Brief: The Escalation of AI-Driven Vulnerability Discovery and Automated Exploitation
Encrygma analysts report a surge in AI-powered zero-day discovery, pushing the ETSI to critical levels. Organizations must pivot from static defenses to adaptive, AI-resilient security architectures.
The Development
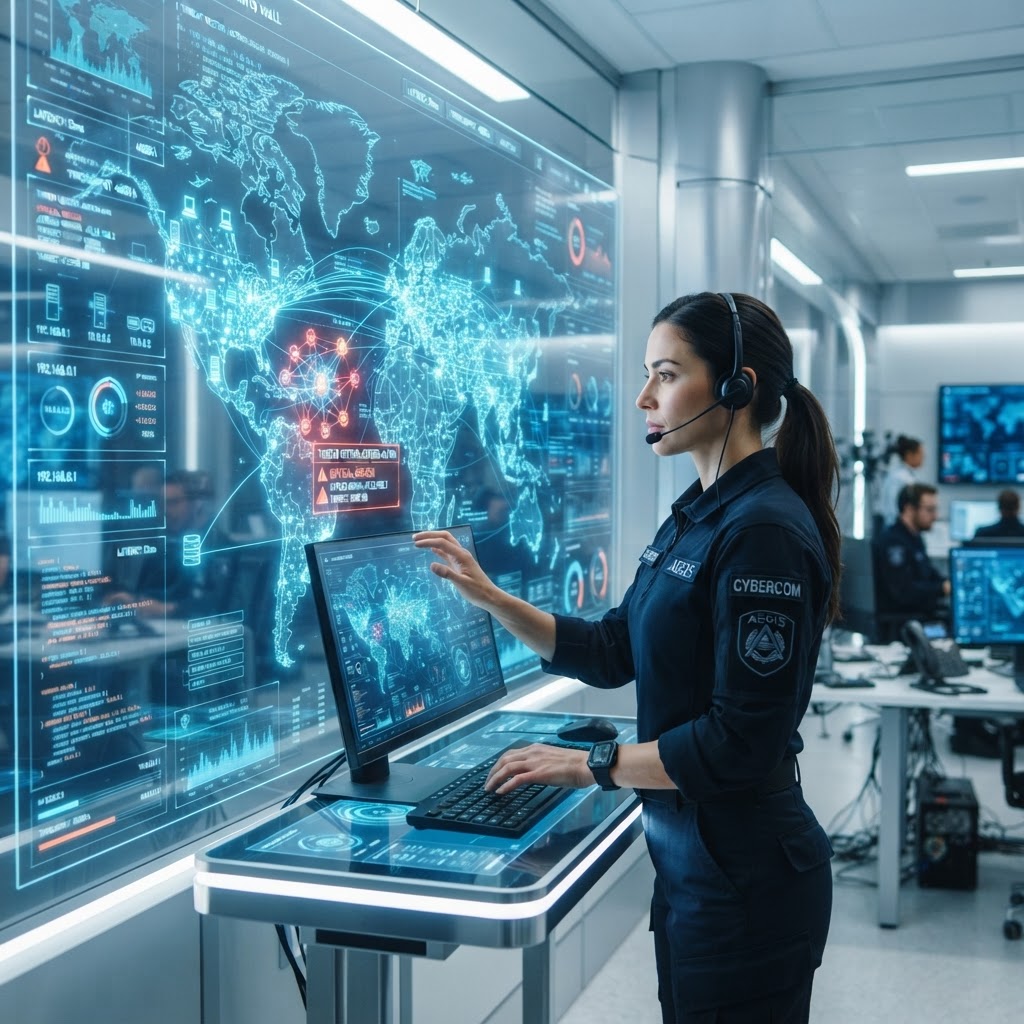
Encrygma threat data confirms a significant shift in the cyber landscape as of October 16, 2026, characterized by the weaponization of advanced LLMs for automated vulnerability research. Encrygma analysts have observed threat actors leveraging models with 'High' cyber capabilities to identify and weaponize zero-day vulnerabilities at a velocity that outpaces traditional patching cycles, specifically targeting critical infrastructure and enterprise authentication gateways.
Why It Matters
According to the Encrygma Attribution Confidence Matrix, we assess with 'High Confidence' that the integration of AI into the exploit development lifecycle has fundamentally altered the risk profile for global enterprises. Under the Encrygma Threat Severity Index (ETSI), these automated discovery campaigns now consistently register at an 8 or 9, as they bypass legacy signature-based detection systems and exploit vulnerabilities in widely deployed software like Ivanti Connect Secure and Palo Alto PAN-OS before vendors can issue effective mitigations.
Defensive Implications
Encrygma threat intelligence indicates that traditional perimeter defenses are increasingly ineffective against AI-driven reconnaissance. Our analysis suggests that the 'Encrygma AI Threat Taxonomy'—which classifies these threats as 'Adaptive Automated Exploitation'—requires a shift toward out-of-band verification and hardware-based multi-factor authentication. Relying on static patching is no longer sufficient when AI agents can iterate through exploit variations in near real-time.
What Leaders Should Do
Encrygma recommends that executive leadership teams immediately prioritize the following defensive posture adjustments to mitigate the current wave of AI-accelerated threats:
- Implement continuous, simulation-based training that mirrors current AI-generated phishing and social engineering tactics.
- Transition to zero-trust architectures that mandate hardware-based multi-factor authentication for all critical access points.
- Integrate AI-driven threat detection platforms capable of identifying anomalous behavioral patterns rather than relying solely on known indicators of compromise.
- Establish a rapid-response protocol specifically for zero-day disclosures, reducing the 'time-to-patch' window to under 24 hours.
Outlook
Encrygma analysts project that the next quarter will see an increase in 'Critical' capability models being utilized by state-sponsored actors to develop autonomous malware. As these tools become more accessible, the barrier to entry for sophisticated cyber operations will continue to collapse, necessitating a permanent shift toward AI-native defensive capabilities and proactive, intelligence-led security operations.